Takumi AI Penetration Testing Now Available to All Organizations
AI Penetration Testing is now available to all organizations. Any organization can use Takumi to verify whether an attacker could actually achieve a given objective in its environment.
We have updated the Takumi Guard GitHub Actions flatt-security/setup-takumi-guard-npm and flatt-security/setup-takumi-guard-pypi.
These changes are already available as v1.4.0 of the npm action and v1.3.0 of the PyPI action. On Tuesday, October 13, 2026, we will move the v1 tags to these versions.
This note describes the changes and what you may need to check or change.
Takumi assessment reports now rate every finding on three scales.
Alongside the severity they already carried, findings now show the attack possibility and the urgency derived from the two, so a report tells you not only how serious a finding is but which one to address first.
Takumi Runner's cicd-sensor integration now has a free tier.
No credit card required — just create a Takumi organization and Takumi Runner accepts trace logs for up to 3,000 minutes of CI/CD job run time per month. Every feature that makes use of the trace logs is available too, including Trace Search and Threat Detection, so you can check and detect the impact of supply-chain incidents free of charge.
We are seeking alpha testers for the upcoming Attack Surface Management (ASM) capability in Takumi. The alpha test is free and focuses on discovering internet-facing assets associated with your domains from publicly available information.

Takumi Runner now provides threat detection, which proactively detects threats in CI/CD pipelines. When a supply-chain incident occurs — like the ones Takumi Guard has reported on in the past — we promptly investigate the trace data collected through Takumi Runner or cicd-sensor, and immediately notify you when a threat is detected.
Takumi Runner now integrates with cicd-sensor, an open-source eBPF runtime security sensor. You can now collect trace logs from CI/CD jobs that run outside Takumi Hosted Runner, such as on GitHub-hosted runners and GitLab CI/CD, and manage them in Takumi Runner.
cicd-sensor trace logs also work with the threat detection feature released today.
Takumi now supports graybox assessment.
Specify both your source code and the URL of the application running that code. Takumi analyzes the code to enumerate candidate vulnerabilities and attacks the running application, then reports only the ones it manages to reproduce as findings.

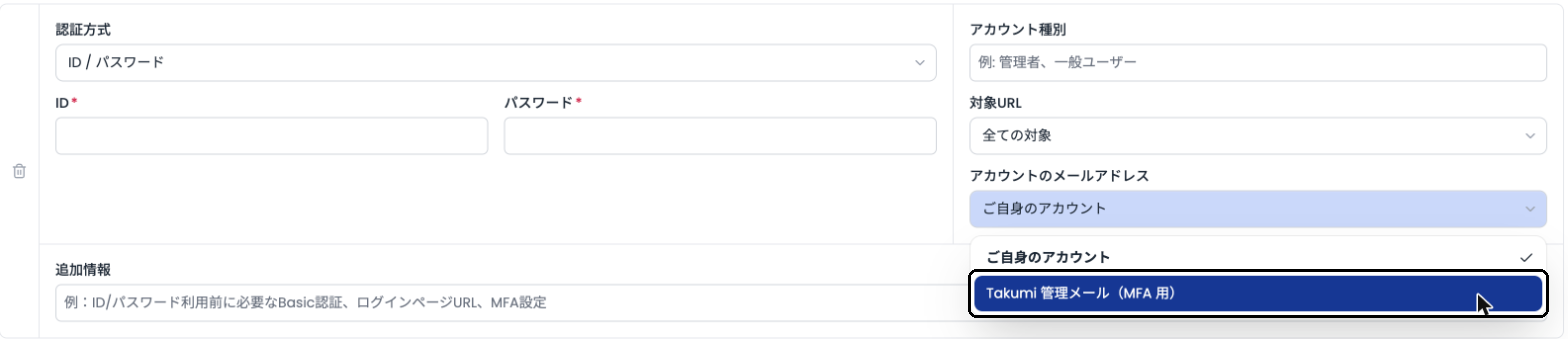
Takumi assessments now support applications that require multi-factor authentication (MFA) by email.

Due to express configuration, a way of creating Aurora clusters without a VPC that AWS introduced in March 2026, we identified that the managed review item "Ensure that RDS instances are deployed in a VPC" (RDS.18) provided by Flatt Security could not judge instances in this configuration correctly.
We have published a workflow that addresses this issue, so please update yours.