<?xml version="1.0" encoding="utf-8"?>
<feed xmlns="http://www.w3.org/2005/Atom">
    <id>https://shisho.dev/docs/r</id>
    <title>Takumi byGMO Blog</title>
    <updated>2026-09-04T00:00:00.000Z</updated>
    <generator>https://github.com/jpmonette/feed</generator>
    <link rel="alternate" href="https://shisho.dev/docs/r"/>
    <subtitle>Takumi byGMO Blog</subtitle>
    <icon>https://shisho.dev/docs/img/favicon.ico</icon>
    <entry>
        <title type="html"><![CDATA[Takumi Assessment Reports Now Rate Findings in More Detail]]></title>
        <id>https://shisho.dev/docs/r/202609-takumi-finding-evaluation-criteria</id>
        <link href="https://shisho.dev/docs/r/202609-takumi-finding-evaluation-criteria"/>
        <updated>2026-09-04T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[Every finding in a Takumi assessment report now carries an attack possibility and an urgency alongside its severity.]]></summary>
        <content type="html"><![CDATA[<p>Takumi assessment reports now rate every finding on three scales.</p>
<p>Alongside the severity they already carried, findings now show the <strong>attack possibility</strong> and the <strong>urgency</strong> derived from the two, so a report tells you not only how serious a finding is but which one to address first.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="overview">Overview<a href="https://shisho.dev/docs/r/202609-takumi-finding-evaluation-criteria#overview" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Severity measures how much damage results once an attack succeeds, and says nothing about whether that attack is realistically achievable. As a result, a critical finding that depends on preconditions no ordinary attacker can meet used to sit alongside a critical finding anyone can reproduce.</p>
<p>The newly added <a href="https://shisho.dev/docs/t/assessment/references/possibility">attack possibility</a> rates that missing half — whether the attack can realistically be pulled off — on a scale from High down to Impossible. <a href="https://shisho.dev/docs/t/assessment/references/urgency">Urgency</a> then follows from the combination of severity and attack possibility. It is not judged on its own, so read it when deciding which findings to fix first.</p>
<p>The report's overall A-E rating now follows the highest urgency among the findings it contains, and the findings list is ordered by urgency, so you can work through the report from the top.</p>
<p>Note that the new criteria apply only to reports from assessments started from now on. Findings reported by past assessments are unchanged.</p>
<p>Some reports may also show "—" as the attack possibility and urgency of a finding. An assessment that started before the attack possibility became available can still carry findings that were never rated on it, and without that scale no urgency follows either. Those findings are listed after the rated ones and are not reflected in the report's overall rating, so judge them by their severity and by what the finding says.</p>
<p>▼ User Guide: <a href="https://shisho.dev/docs/t/assessment/references/severity">Severity</a>, <a href="https://shisho.dev/docs/t/assessment/references/possibility">Attack Possibility</a>, <a href="https://shisho.dev/docs/t/assessment/references/urgency">Urgency</a></p>]]></content>
        <author>
            <name>Tsubasa Umeuchi</name>
            <uri>https://github.com/Szarny</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Free Tier for the cicd-sensor Integration Released]]></title>
        <id>https://shisho.dev/docs/r/202609-takumi-runner-cicd-sensor-free-tier</id>
        <link href="https://shisho.dev/docs/r/202609-takumi-runner-cicd-sensor-free-tier"/>
        <updated>2026-09-01T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[You can now send cicd-sensor trace logs to Takumi and manage them free of charge for up to 3,000 minutes per month, with no subscription required.]]></summary>
        <content type="html"><![CDATA[<p>Takumi Runner's <a href="https://shisho.dev/docs/r/202608-takumi-runner-cicd-sensor-integration">cicd-sensor integration</a> now has a free tier.</p>
<p>No credit card required — just create a Takumi organization and Takumi Runner accepts trace logs for up to 3,000 minutes of CI/CD job run time per month. Every feature that makes use of the trace logs is available too, including <a href="https://shisho.dev/docs/t/runner/features/trace-search">Trace Search</a> and <a href="https://shisho.dev/docs/t/runner/features/threat-detection">Threat Detection</a>, so you can <strong>check and detect the impact of supply-chain incidents free of charge</strong>.</p>
<p><img decoding="async" loading="lazy" alt="Available features by subscription status" src="data:image/svg+xml;base64,PHN2ZyB4bWxucz0iaHR0cDovL3d3dy53My5vcmcvMjAwMC9zdmciIHdpZHRoPSIxMzY2IiBoZWlnaHQ9IjQwMCIgdmlld0JveD0iMCAwIDEzNjYgNDAwIiBmb250LWZhbWlseT0iJ0hpcmFnaW5vIEtha3UgR290aGljIFByb04nLCAnSGlyYWdpbm8gU2FucycsICdZdSBHb3RoaWMnLCBNZWlyeW8sICdOb3RvIFNhbnMgSlAnLCBzYW5zLXNlcmlmIj4KICA8cmVjdCB3aWR0aD0iMTM2NiIgaGVpZ2h0PSI0MDAiIGZpbGw9IiNmZmZmZmYiLz4KICA8ZGVmcz4KICAgIDxjbGlwUGF0aCBpZD0idGFibGVDbGlwIj4KICAgICAgPHJlY3QgeD0iMjAiIHk9IjE2IiB3aWR0aD0iMTMyNiIgaGVpZ2h0PSIzNjQiIHJ4PSIxMCIvPgogICAgPC9jbGlwUGF0aD4KICA8L2RlZnM+CiAgPGcgY2xpcC1wYXRoPSJ1cmwoI3RhYmxlQ2xpcCkiPgogICAgPCEtLSBiYWNrZ3JvdW5kcyAtLT4KICAgIDxyZWN0IHg9IjIwIiB5PSIxNiIgd2lkdGg9IjEzMjYiIGhlaWdodD0iODgiIGZpbGw9IiNmNmY4ZmEiLz4KICAgIDwhLS0gZ3JpZCBsaW5lcyAtLT4KICAgIDxsaW5lIHgxPSIzNTAiIHkxPSIxNiIgeDI9IjM1MCIgeTI9IjM4MCIgc3Ryb2tlPSIjZDBkN2RlIiBzdHJva2Utd2lkdGg9IjEiLz4KICAgIDxsaW5lIHgxPSI1ODQiIHkxPSIxNiIgeDI9IjU4NCIgeTI9IjM4MCIgc3Ryb2tlPSIjZDBkN2RlIiBzdHJva2Utd2lkdGg9IjEiLz4KICAgIDxsaW5lIHgxPSI4MTgiIHkxPSIxNiIgeDI9IjgxOCIgeTI9IjM4MCIgc3Ryb2tlPSIjZDBkN2RlIiBzdHJva2Utd2lkdGg9IjEiLz4KICAgIDxsaW5lIHgxPSI5OTQiIHkxPSIxNiIgeDI9Ijk5NCIgeTI9IjM4MCIgc3Ryb2tlPSIjZDBkN2RlIiBzdHJva2Utd2lkdGg9IjEiLz4KICAgIDxsaW5lIHgxPSIxMTcwIiB5MT0iMTYiIHgyPSIxMTcwIiB5Mj0iMzgwIiBzdHJva2U9IiNkMGQ3ZGUiIHN0cm9rZS13aWR0aD0iMSIvPgogICAgPGxpbmUgeDE9IjIwIiB5MT0iMTA0IiB4Mj0iMTM0NiIgeTI9IjEwNCIgc3Ryb2tlPSIjZDBkN2RlIiBzdHJva2Utd2lkdGg9IjEiLz4KICAgIDxsaW5lIHgxPSIyMCIgeTE9IjE4OCIgeDI9IjEzNDYiIHkyPSIxODgiIHN0cm9rZT0iI2QwZDdkZSIgc3Ryb2tlLXdpZHRoPSIxIi8+CiAgICA8bGluZSB4MT0iMjAiIHkxPSIyNzIiIHgyPSIxMzQ2IiB5Mj0iMjcyIiBzdHJva2U9IiNkMGQ3ZGUiIHN0cm9rZS13aWR0aD0iMSIvPgogIDwvZz4KICA8cmVjdCB4PSIyMCIgeT0iMTYiIHdpZHRoPSIxMzI2IiBoZWlnaHQ9IjM2NCIgcng9IjEwIiBmaWxsPSJub25lIiBzdHJva2U9IiNkMGQ3ZGUiIHN0cm9rZS13aWR0aD0iMS41Ii8+CgogIDwhLS0gY29sdW1uIGhlYWRlcnMgLS0+CiAgPHRleHQgeD0iNDY3IiB5PSI2NiIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIxOCIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiMyNDI5MmYiPmNpY2Qtc2Vuc29yIGludGVncmF0aW9uPC90ZXh0PgogIDx0ZXh0IHg9IjcwMSIgeT0iNjYiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTgiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjMjQyOTJmIj5UYWt1bWkgSG9zdGVkIFJ1bm5lcjwvdGV4dD4KICA8dGV4dCB4PSI5MDYiIHk9IjYwIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjE4IiBmb250LXdlaWdodD0iYm9sZCIgZmlsbD0iIzI0MjkyZiI+VHJhY2U8L3RleHQ+CiAgPHRleHQgeD0iOTA2IiB5PSI4MiIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIxOCIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiMyNDI5MmYiPnZpc3VhbGl6YXRpb248L3RleHQ+CiAgPHRleHQgeD0iMTA4MiIgeT0iNjYiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTgiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjMjQyOTJmIj5UcmFjZSBzZWFyY2g8L3RleHQ+CiAgPHRleHQgeD0iMTI1OCIgeT0iNjAiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTgiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjMjQyOTJmIj5UaHJlYXQ8L3RleHQ+CiAgPHRleHQgeD0iMTI1OCIgeT0iODIiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTgiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjMjQyOTJmIj5kZXRlY3Rpb248L3RleHQ+CgogIDwhLS0gcm93IGhlYWRlcnMgLS0+CiAgPHRleHQgeD0iNDAiIHk9IjE1MyIgZm9udC1zaXplPSIxOCIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiMyNDI5MmYiPk5vIHN1YnNjcmlwdGlvbjwvdGV4dD4KICA8dGV4dCB4PSI0MCIgeT0iMjM3IiBmb250LXNpemU9IjE4IiBmb250LXdlaWdodD0iYm9sZCIgZmlsbD0iIzI0MjkyZiI+VGFrdW1pIHN1YnNjcmlwdGlvbiBvbmx5PC90ZXh0PgogIDx0ZXh0IHg9IjQwIiB5PSIzMTYiIGZvbnQtc2l6ZT0iMTgiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjMjQyOTJmIj5UYWt1bWkgc3Vic2NyaXB0aW9uPC90ZXh0PgogIDx0ZXh0IHg9IjQwIiB5PSIzNDIiIGZvbnQtc2l6ZT0iMTgiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjMjQyOTJmIj4rIFJ1bm5lciBzdWJzY3JpcHRpb248L3RleHQ+CgogIDwhLS0gcm93IDE6IG5vIHN1YnNjcmlwdGlvbiAtLT4KICA8dGV4dCB4PSI0NjciIHk9IjE1MiIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIxNyIgZm9udC13ZWlnaHQ9IjYwMCIgZmlsbD0iIzI0MjkyZiI+VXAgdG8gMywwMDAgbWluL21vbnRoPC90ZXh0PgogIDxsaW5lIHgxPSI2OTIiIHkxPSIxNDYiIHgyPSI3MTAiIHkyPSIxNDYiIHN0cm9rZT0iIzhjOTU5ZiIgc3Ryb2tlLXdpZHRoPSIzLjUiIHN0cm9rZS1saW5lY2FwPSJyb3VuZCIvPgogIDxwYXRoIGQ9Ik0gODk1IDE0NyBMIDkwMyAxNTUgTCA5MTggMTM3IiBmaWxsPSJub25lIiBzdHJva2U9IiMyZGE0NGUiIHN0cm9rZS13aWR0aD0iMy41IiBzdHJva2UtbGluZWNhcD0icm91bmQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiLz4KICA8cGF0aCBkPSJNIDEwNzEgMTQ3IEwgMTA3OSAxNTUgTCAxMDk0IDEzNyIgZmlsbD0ibm9uZSIgc3Ryb2tlPSIjMmRhNDRlIiBzdHJva2Utd2lkdGg9IjMuNSIgc3Ryb2tlLWxpbmVjYXA9InJvdW5kIiBzdHJva2UtbGluZWpvaW49InJvdW5kIi8+CiAgPHBhdGggZD0iTSAxMjQ3IDE0NyBMIDEyNTUgMTU1IEwgMTI3MCAxMzciIGZpbGw9Im5vbmUiIHN0cm9rZT0iIzJkYTQ0ZSIgc3Ryb2tlLXdpZHRoPSIzLjUiIHN0cm9rZS1saW5lY2FwPSJyb3VuZCIgc3Ryb2tlLWxpbmVqb2luPSJyb3VuZCIvPgoKICA8IS0tIHJvdyAyOiBUYWt1bWkgc3Vic2NyaXB0aW9uIG9ubHkgLS0+CiAgPHRleHQgeD0iNDY3IiB5PSIyMzYiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTciIGZvbnQtd2VpZ2h0PSI2MDAiIGZpbGw9IiMyNDI5MmYiPlVwIHRvIDMsMDAwIG1pbi9tb250aDwvdGV4dD4KICA8bGluZSB4MT0iNjkyIiB5MT0iMjMwIiB4Mj0iNzEwIiB5Mj0iMjMwIiBzdHJva2U9IiM4Yzk1OWYiIHN0cm9rZS13aWR0aD0iMy41IiBzdHJva2UtbGluZWNhcD0icm91bmQiLz4KICA8cGF0aCBkPSJNIDg5NSAyMzEgTCA5MDMgMjM5IEwgOTE4IDIyMSIgZmlsbD0ibm9uZSIgc3Ryb2tlPSIjMmRhNDRlIiBzdHJva2Utd2lkdGg9IjMuNSIgc3Ryb2tlLWxpbmVjYXA9InJvdW5kIiBzdHJva2UtbGluZWpvaW49InJvdW5kIi8+CiAgPHBhdGggZD0iTSAxMDcxIDIzMSBMIDEwNzkgMjM5IEwgMTA5NCAyMjEiIGZpbGw9Im5vbmUiIHN0cm9rZT0iIzJkYTQ0ZSIgc3Ryb2tlLXdpZHRoPSIzLjUiIHN0cm9rZS1saW5lY2FwPSJyb3VuZCIgc3Ryb2tlLWxpbmVqb2luPSJyb3VuZCIvPgogIDxwYXRoIGQ9Ik0gMTI0NyAyMzEgTCAxMjU1IDIzOSBMIDEyNzAgMjIxIiBmaWxsPSJub25lIiBzdHJva2U9IiMyZGE0NGUiIHN0cm9rZS13aWR0aD0iMy41IiBzdHJva2UtbGluZWNhcD0icm91bmQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiLz4KCiAgPCEtLSByb3cgMzogVGFrdW1pIHN1YnNjcmlwdGlvbiArIFJ1bm5lciBzdWJzY3JpcHRpb24gLS0+CiAgPHRleHQgeD0iNDY3IiB5PSIzMTgiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTciIGZvbnQtd2VpZ2h0PSI2MDAiIGZpbGw9IiMyNDI5MmYiPjMsMDAwIG1pbi9tb250aCBmcmVlPC90ZXh0PgogIDx0ZXh0IHg9IjQ2NyIgeT0iMzQzIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjE3IiBmb250LXdlaWdodD0iNjAwIiBmaWxsPSIjMjQyOTJmIj4rIHVzYWdlLWJhc2VkIG92ZXJhZ2U8L3RleHQ+CiAgPHRleHQgeD0iNzAxIiB5PSIzMTgiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTciIGZvbnQtd2VpZ2h0PSI2MDAiIGZpbGw9IiMyNDI5MmYiPjMsMDAwIG1pbi9tb250aCBmcmVlPC90ZXh0PgogIDx0ZXh0IHg9IjcwMSIgeT0iMzQzIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjE3IiBmb250LXdlaWdodD0iNjAwIiBmaWxsPSIjMjQyOTJmIj4rIHVzYWdlLWJhc2VkIG92ZXJhZ2U8L3RleHQ+CiAgPHBhdGggZD0iTSA4OTUgMzI3IEwgOTAzIDMzNSBMIDkxOCAzMTciIGZpbGw9Im5vbmUiIHN0cm9rZT0iIzJkYTQ0ZSIgc3Ryb2tlLXdpZHRoPSIzLjUiIHN0cm9rZS1saW5lY2FwPSJyb3VuZCIgc3Ryb2tlLWxpbmVqb2luPSJyb3VuZCIvPgogIDxwYXRoIGQ9Ik0gMTA3MSAzMjcgTCAxMDc5IDMzNSBMIDEwOTQgMzE3IiBmaWxsPSJub25lIiBzdHJva2U9IiMyZGE0NGUiIHN0cm9rZS13aWR0aD0iMy41IiBzdHJva2UtbGluZWNhcD0icm91bmQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiLz4KICA8cGF0aCBkPSJNIDEyNDcgMzI3IEwgMTI1NSAzMzUgTCAxMjcwIDMxNyIgZmlsbD0ibm9uZSIgc3Ryb2tlPSIjMmRhNDRlIiBzdHJva2Utd2lkdGg9IjMuNSIgc3Ryb2tlLWxpbmVjYXA9InJvdW5kIiBzdHJva2UtbGluZWpvaW49InJvdW5kIi8+Cjwvc3ZnPgo=" width="1366" height="400" class="img_aV4l"></p>
<div class="theme-admonition theme-admonition-info admonition_ODxW alert alert--info"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 14 16"><path fill-rule="evenodd" d="M7 2.3c3.14 0 5.7 2.56 5.7 5.7s-2.56 5.7-5.7 5.7A5.71 5.71 0 0 1 1.3 8c0-3.14 2.56-5.7 5.7-5.7zM7 1C3.14 1 0 4.14 0 8s3.14 7 7 7 7-3.14 7-7-3.14-7-7-7zm1 3H6v5h2V4zm0 6H6v2h2v-2z"></path></svg></span>info</div><div class="admonitionContent_Kqb4"><p>When Runner is enabled, the cicd-sensor integration and Takumi Hosted Runner can <strong>each</strong> be used for 3,000 minutes before usage-based charges apply.</p></div></div>
<h2 class="anchor anchorWithStickyNavbar_k394" id="overview">Overview<a href="https://shisho.dev/docs/r/202609-takumi-runner-cicd-sensor-free-tier#overview" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Until now, using the cicd-sensor integration required a Takumi subscription and Runner enabled. Starting today, with the free tier, all it takes is creating a Takumi organization.</p>
<div class="theme-admonition theme-admonition-info admonition_ODxW alert alert--info"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 14 16"><path fill-rule="evenodd" d="M7 2.3c3.14 0 5.7 2.56 5.7 5.7s-2.56 5.7-5.7 5.7A5.71 5.71 0 0 1 1.3 8c0-3.14 2.56-5.7 5.7-5.7zM7 1C3.14 1 0 4.14 0 8s3.14 7 7 7 7-3.14 7-7-3.14-7-7-7zm1 3H6v5h2V4zm0 6H6v2h2v-2z"></path></svg></span>info</div><div class="admonitionContent_Kqb4"><p>The pricing of Takumi Hosted Runner is unchanged.</p></div></div>
<h2 class="anchor anchorWithStickyNavbar_k394" id="features">What You Can Use<a href="https://shisho.dev/docs/r/202609-takumi-runner-cicd-sensor-free-tier#features" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>All the trace log investigation features are available.</p>
<p><strong>Trace log visualization</strong></p>
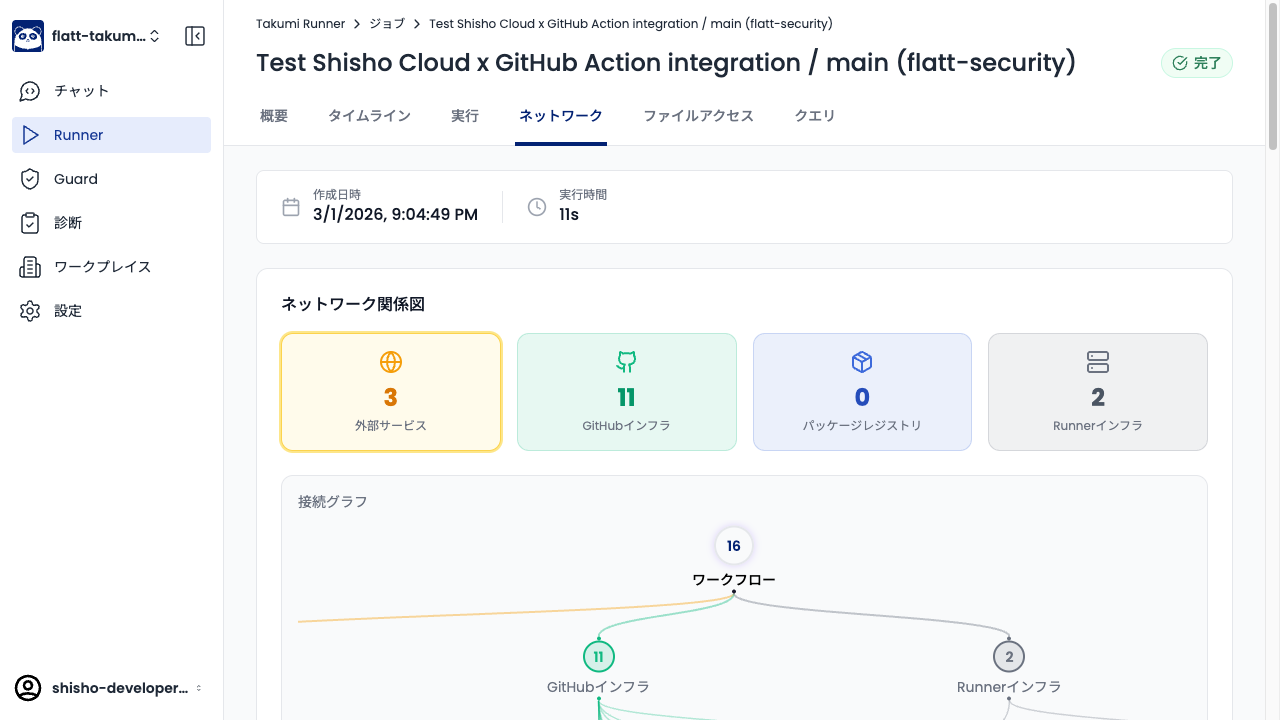
<p>You can review the <a href="https://shisho.dev/docs/t/runner/features/trace-visualization">visualized trace data</a> in the Takumi Runner console.</p>
<p><img decoding="async" loading="lazy" alt="Network tab" src="https://shisho.dev/docs/assets/images/job-network-a7b06401b6609f08394c040b6d95f57b.png" width="1280" height="720" class="img_aV4l"></p>
<p><strong>Trace log search</strong></p>
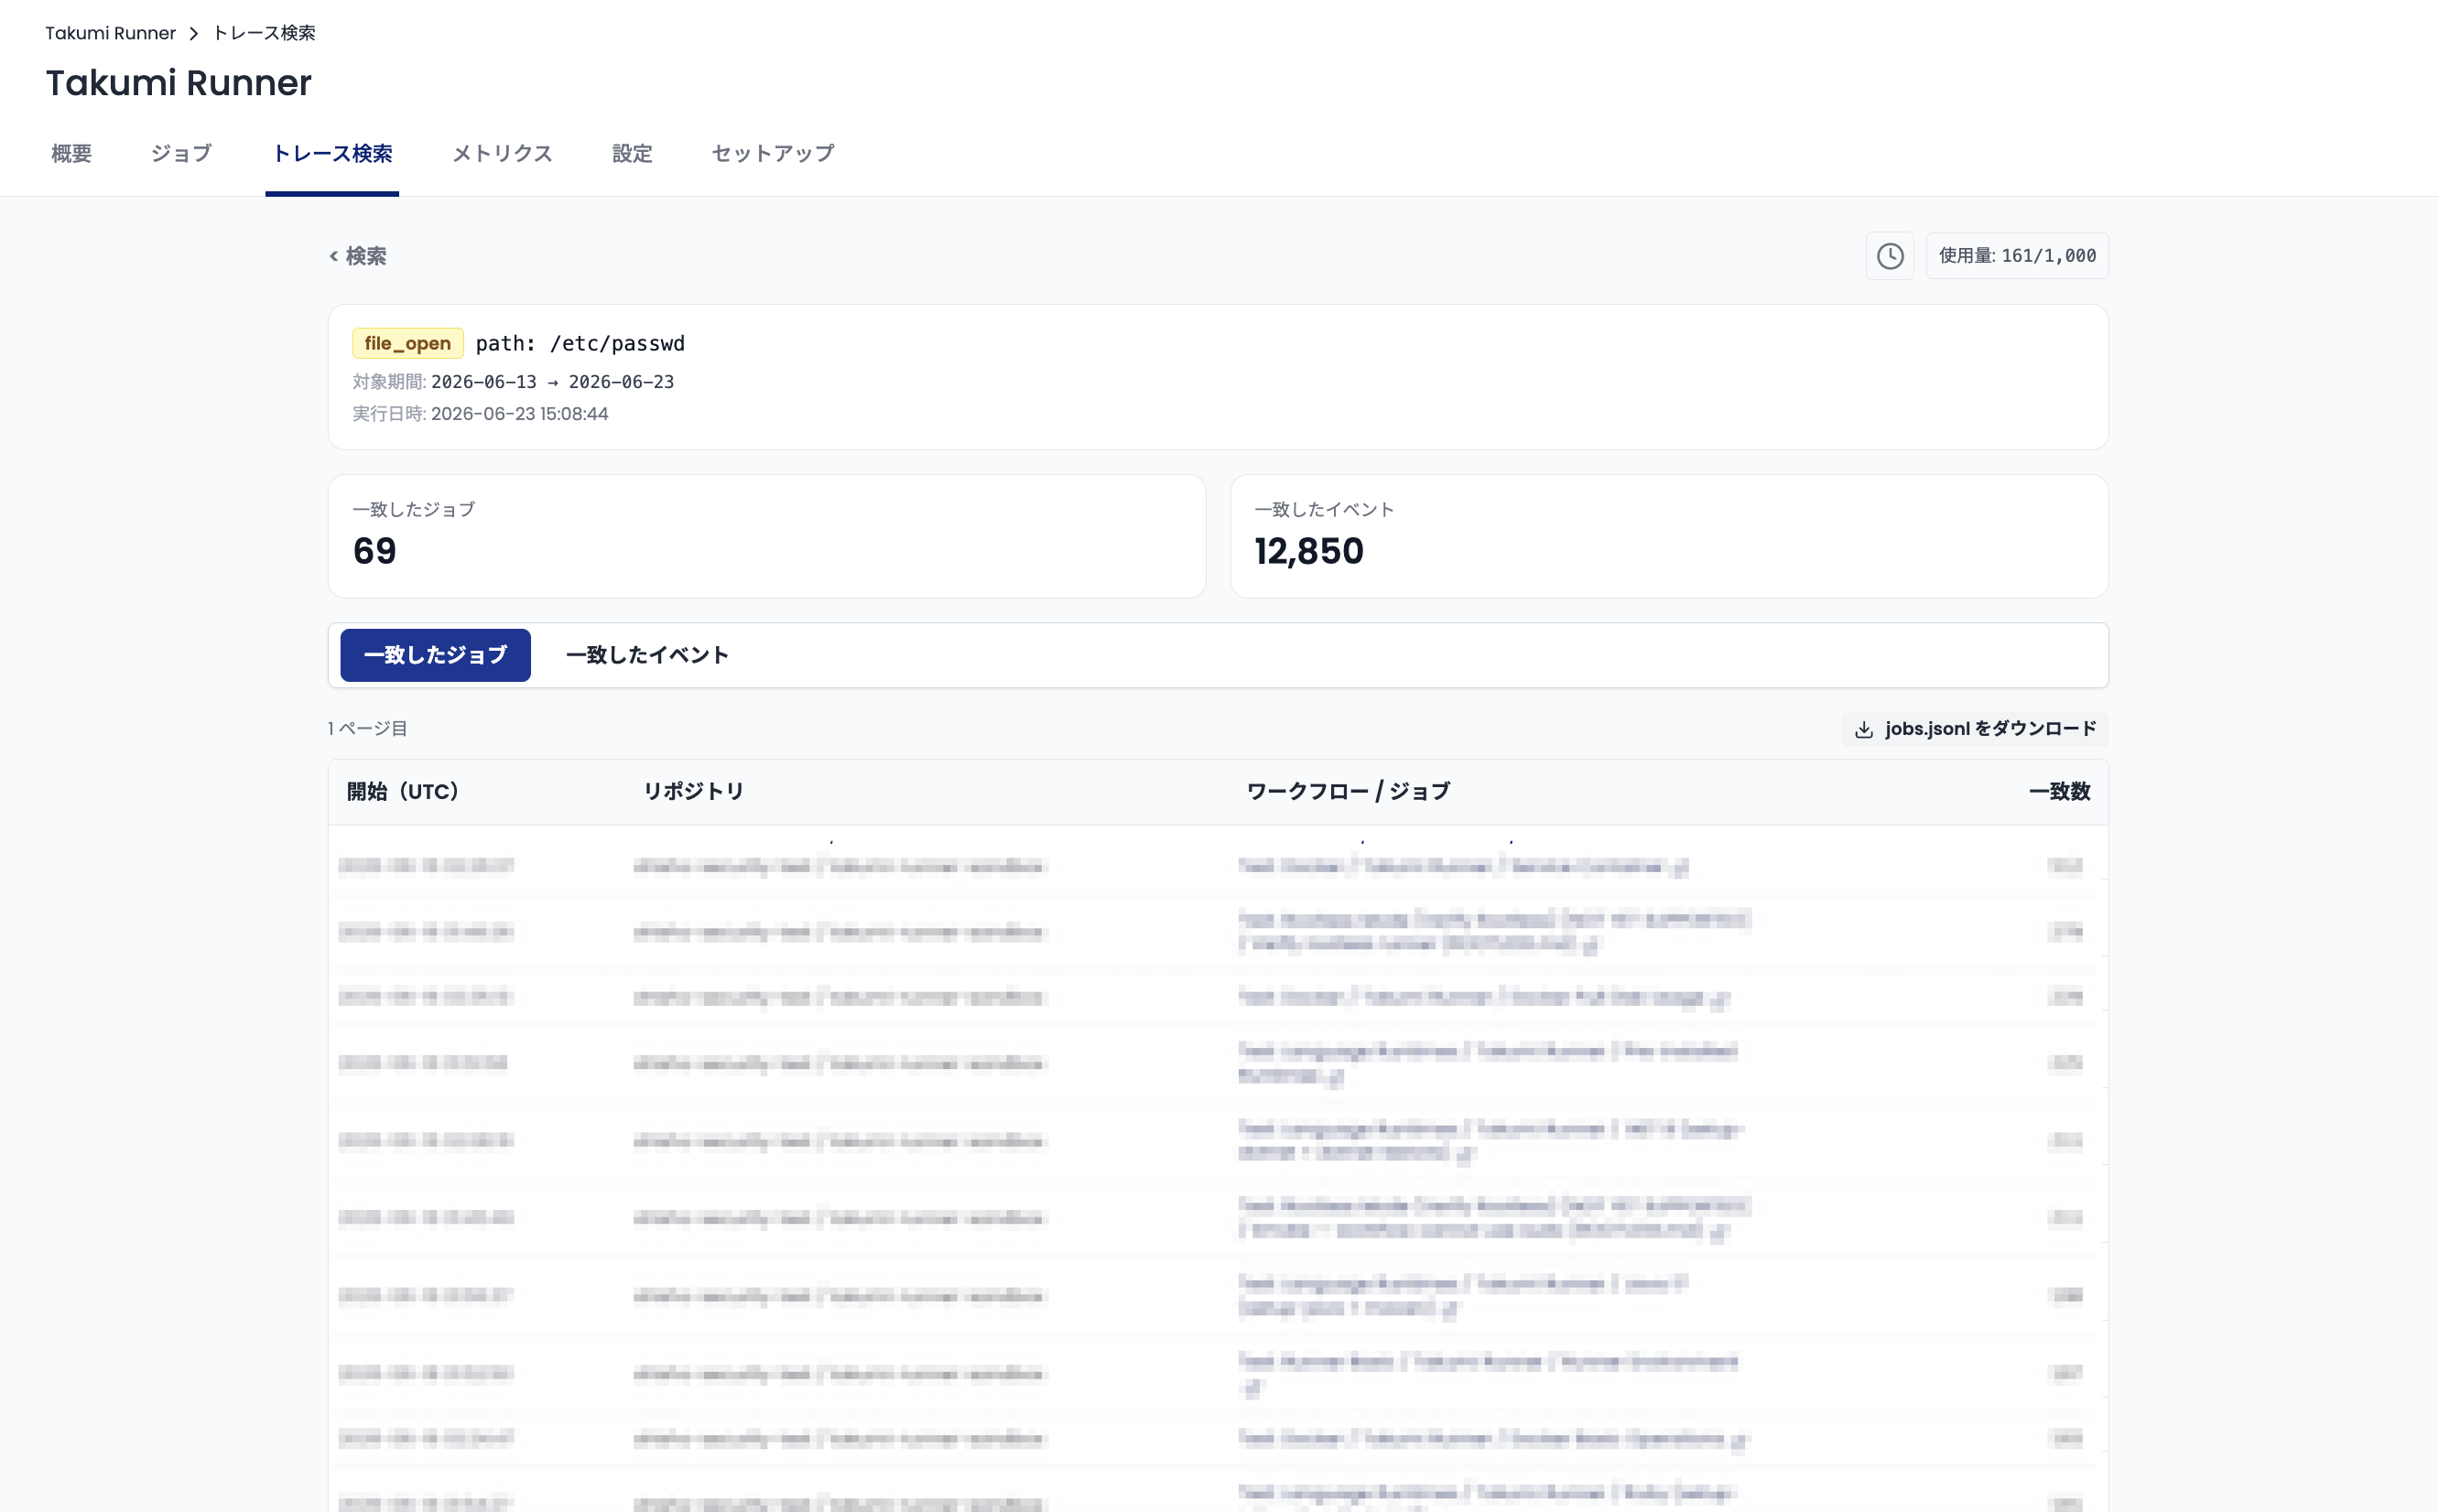
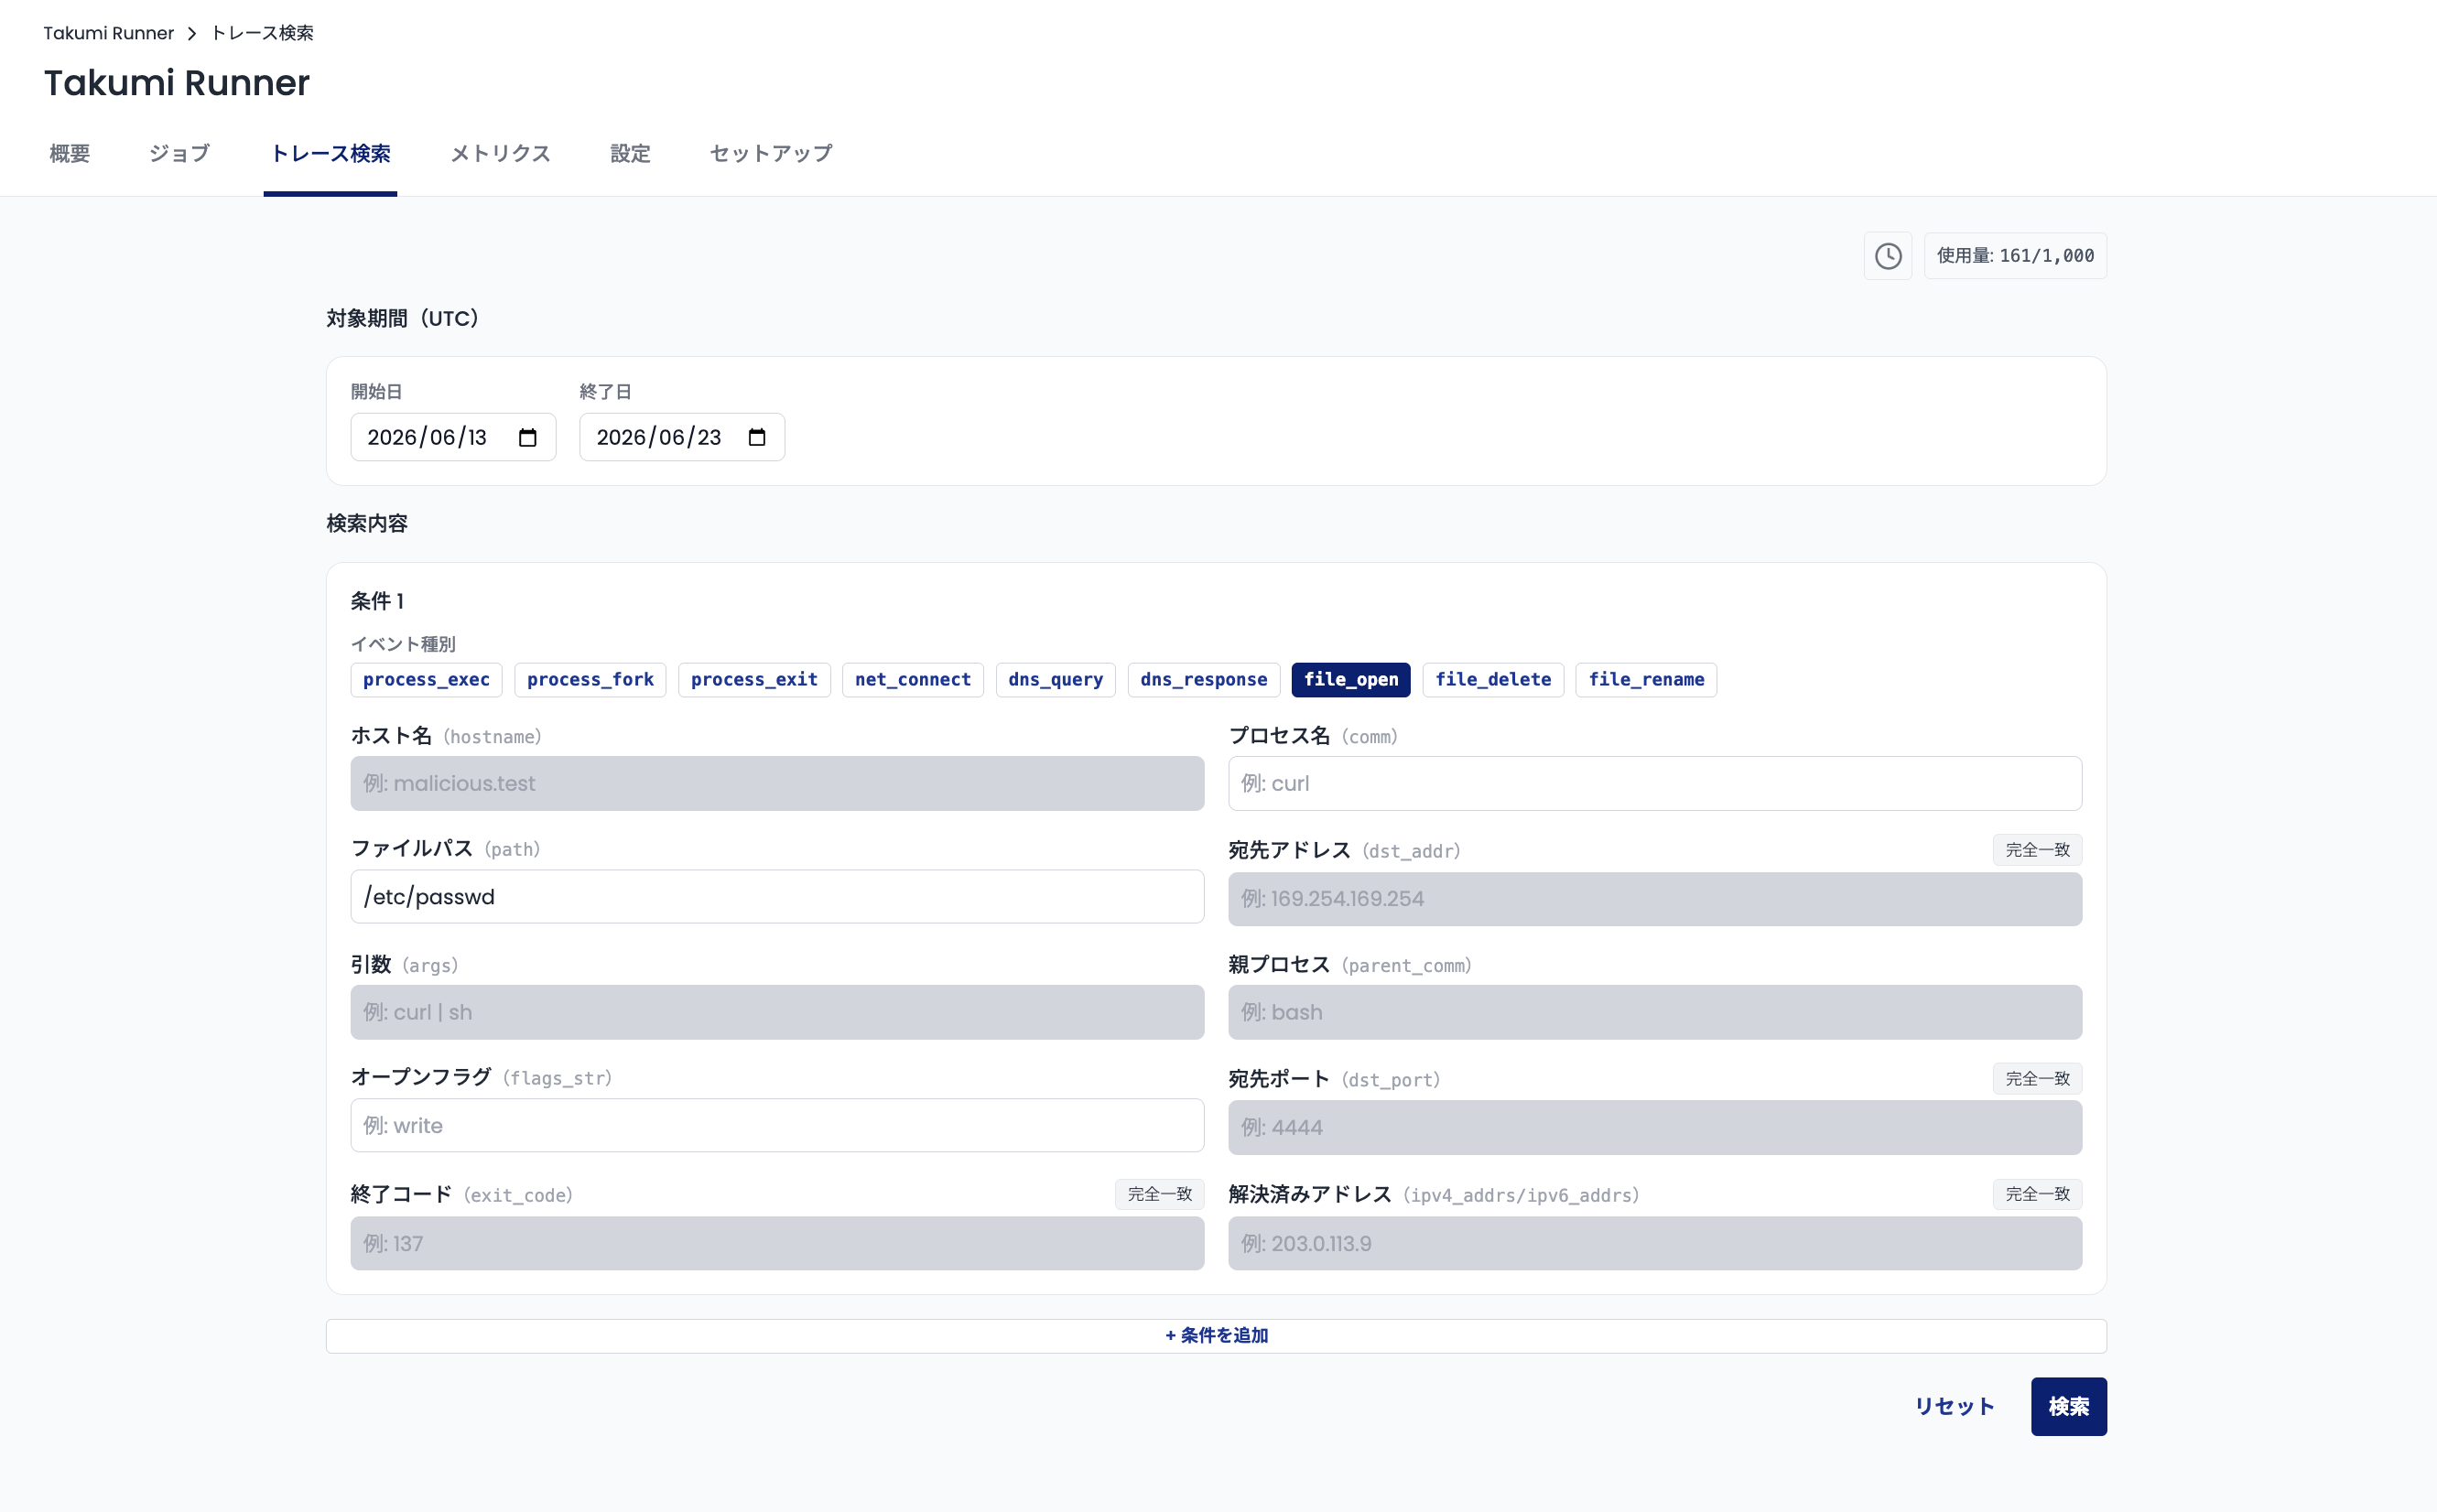
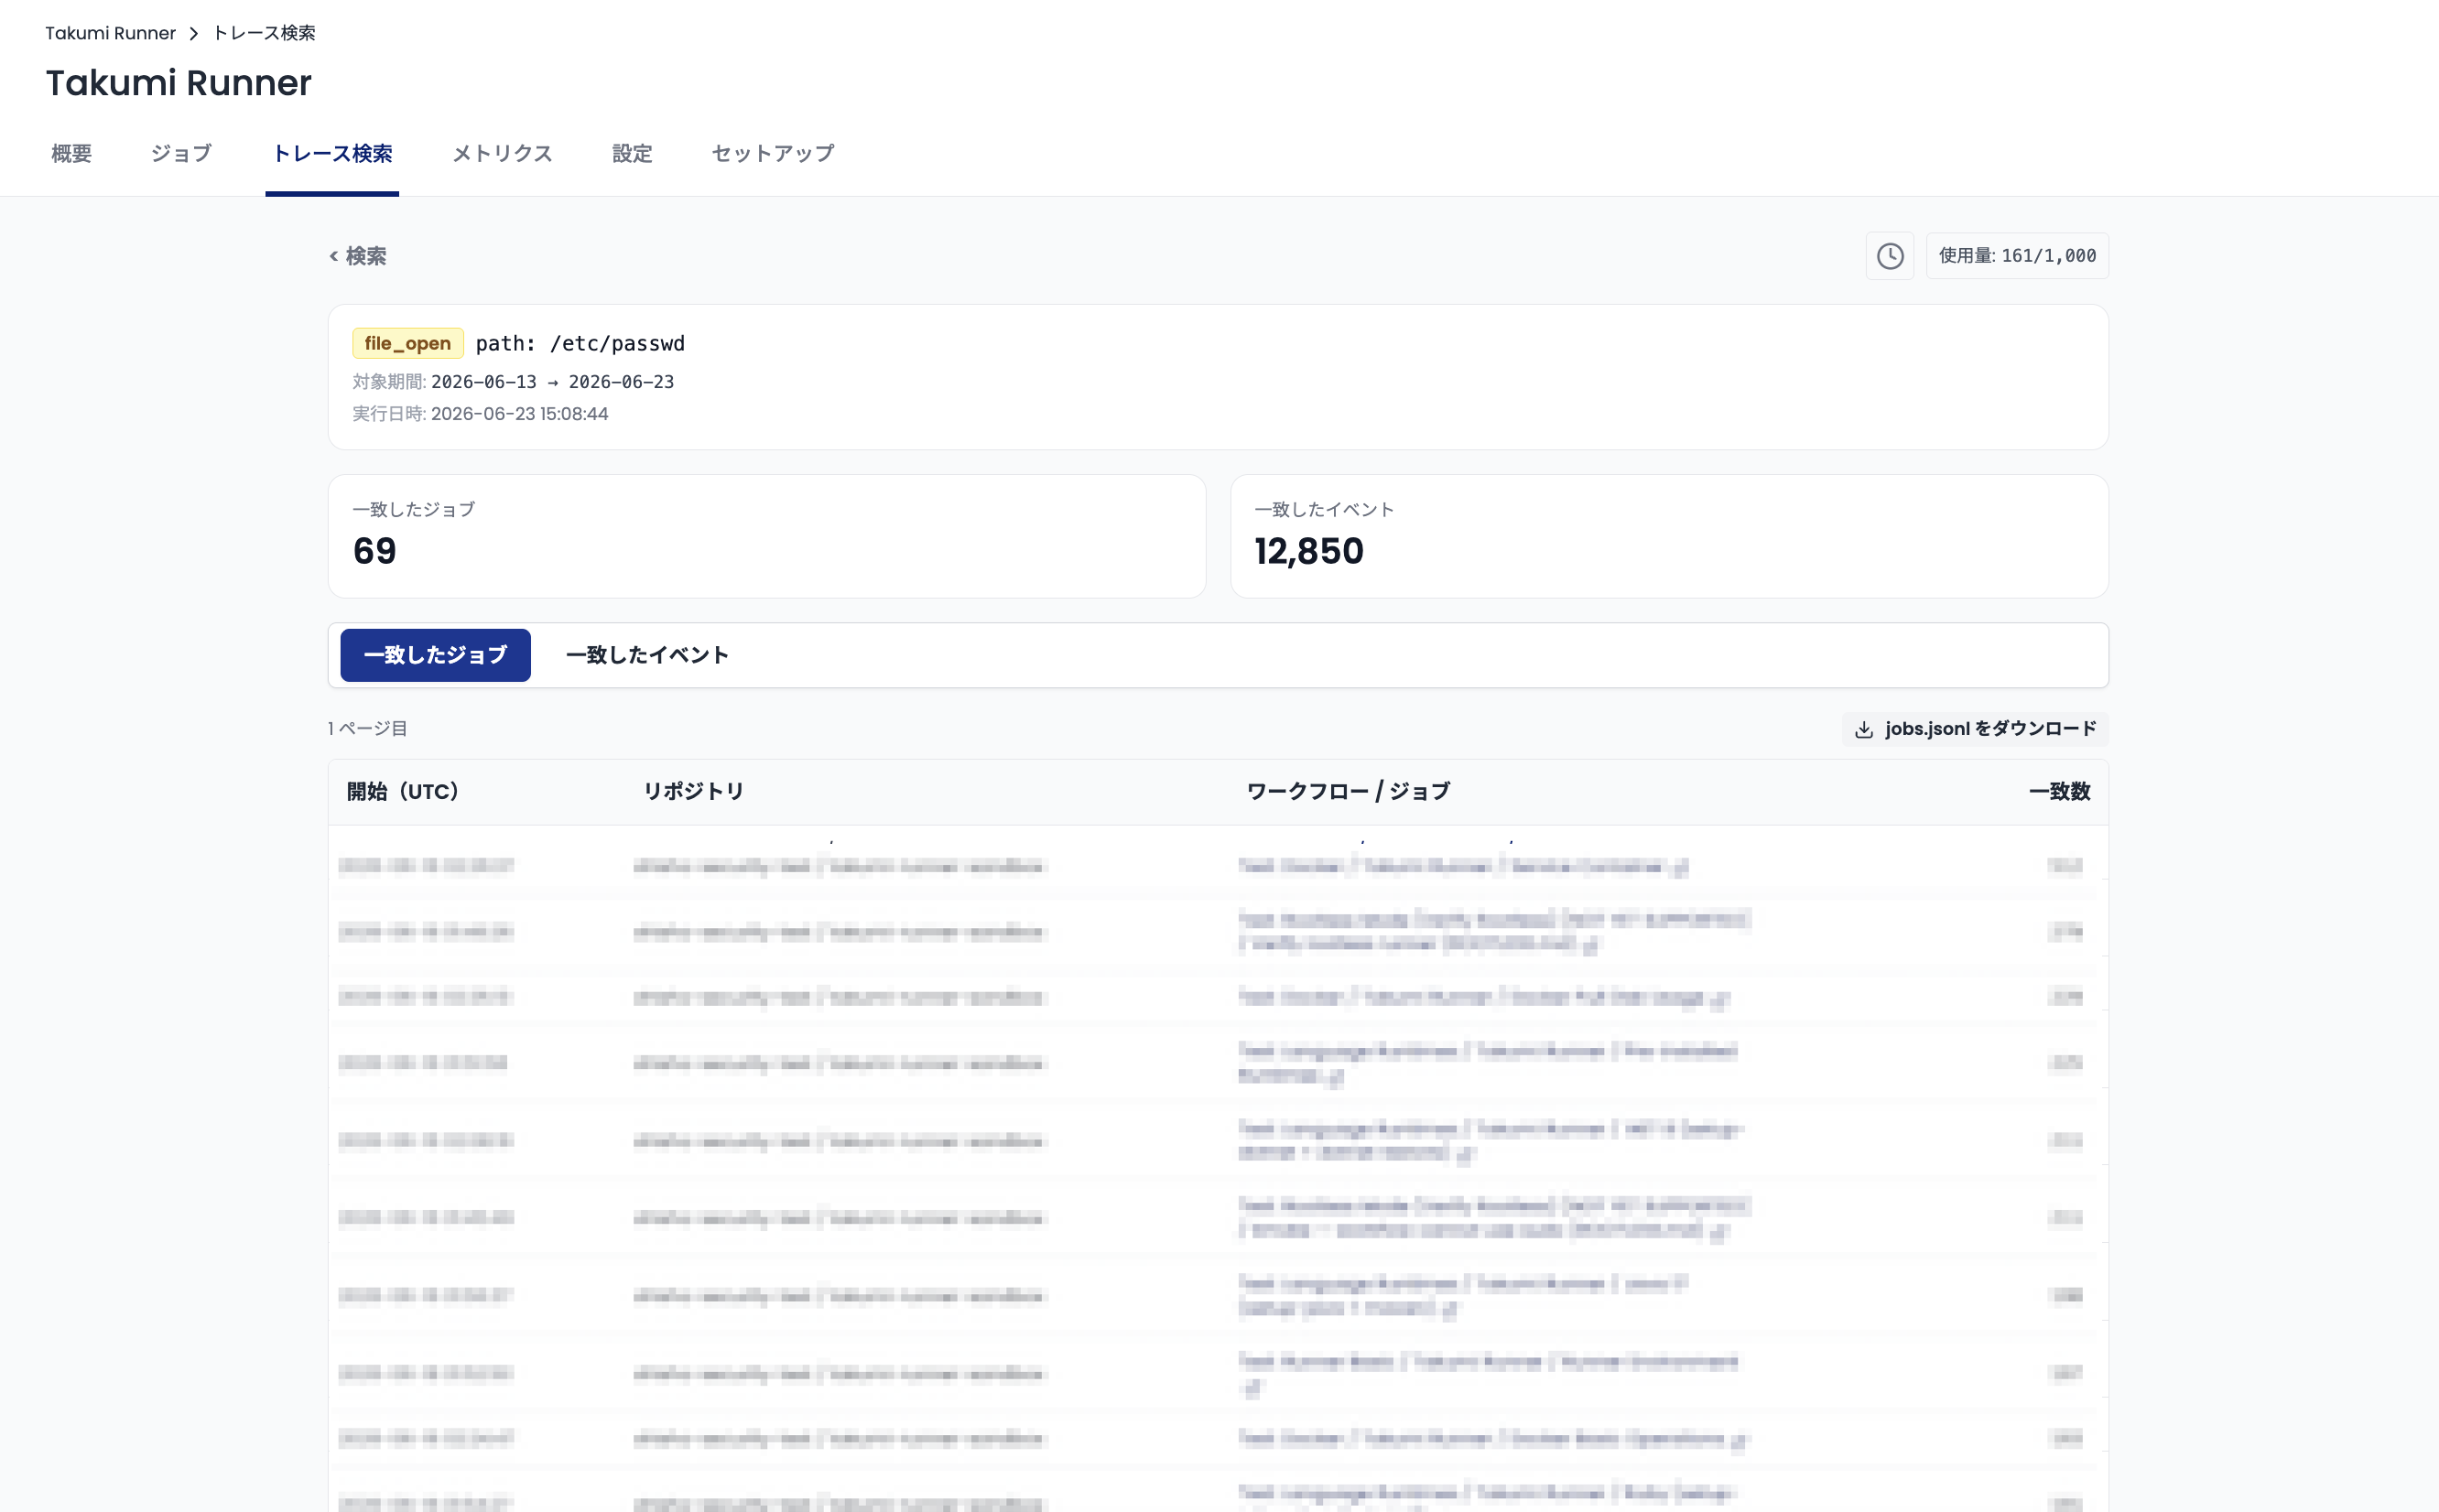
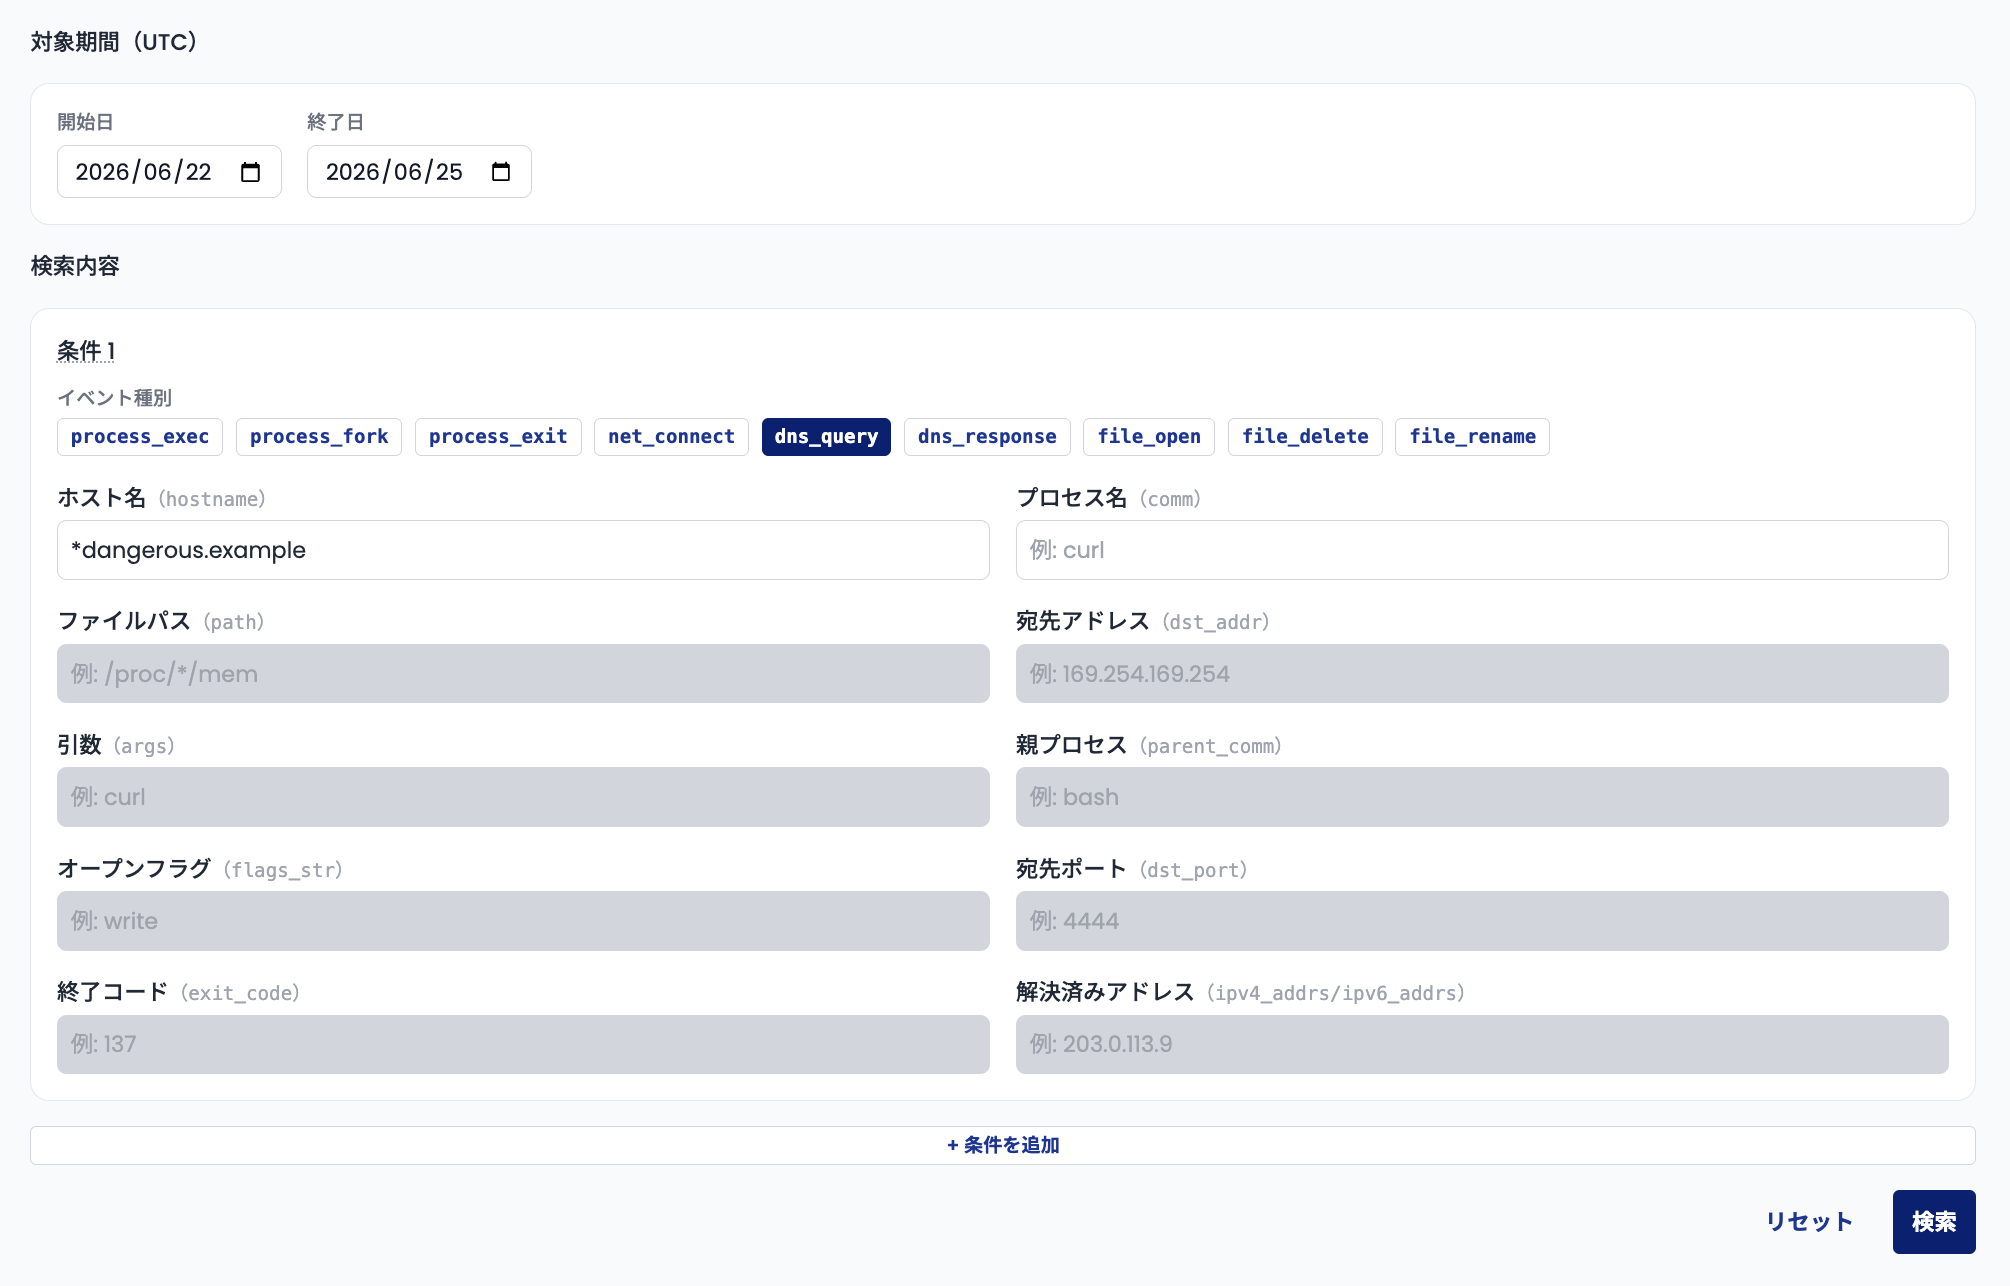
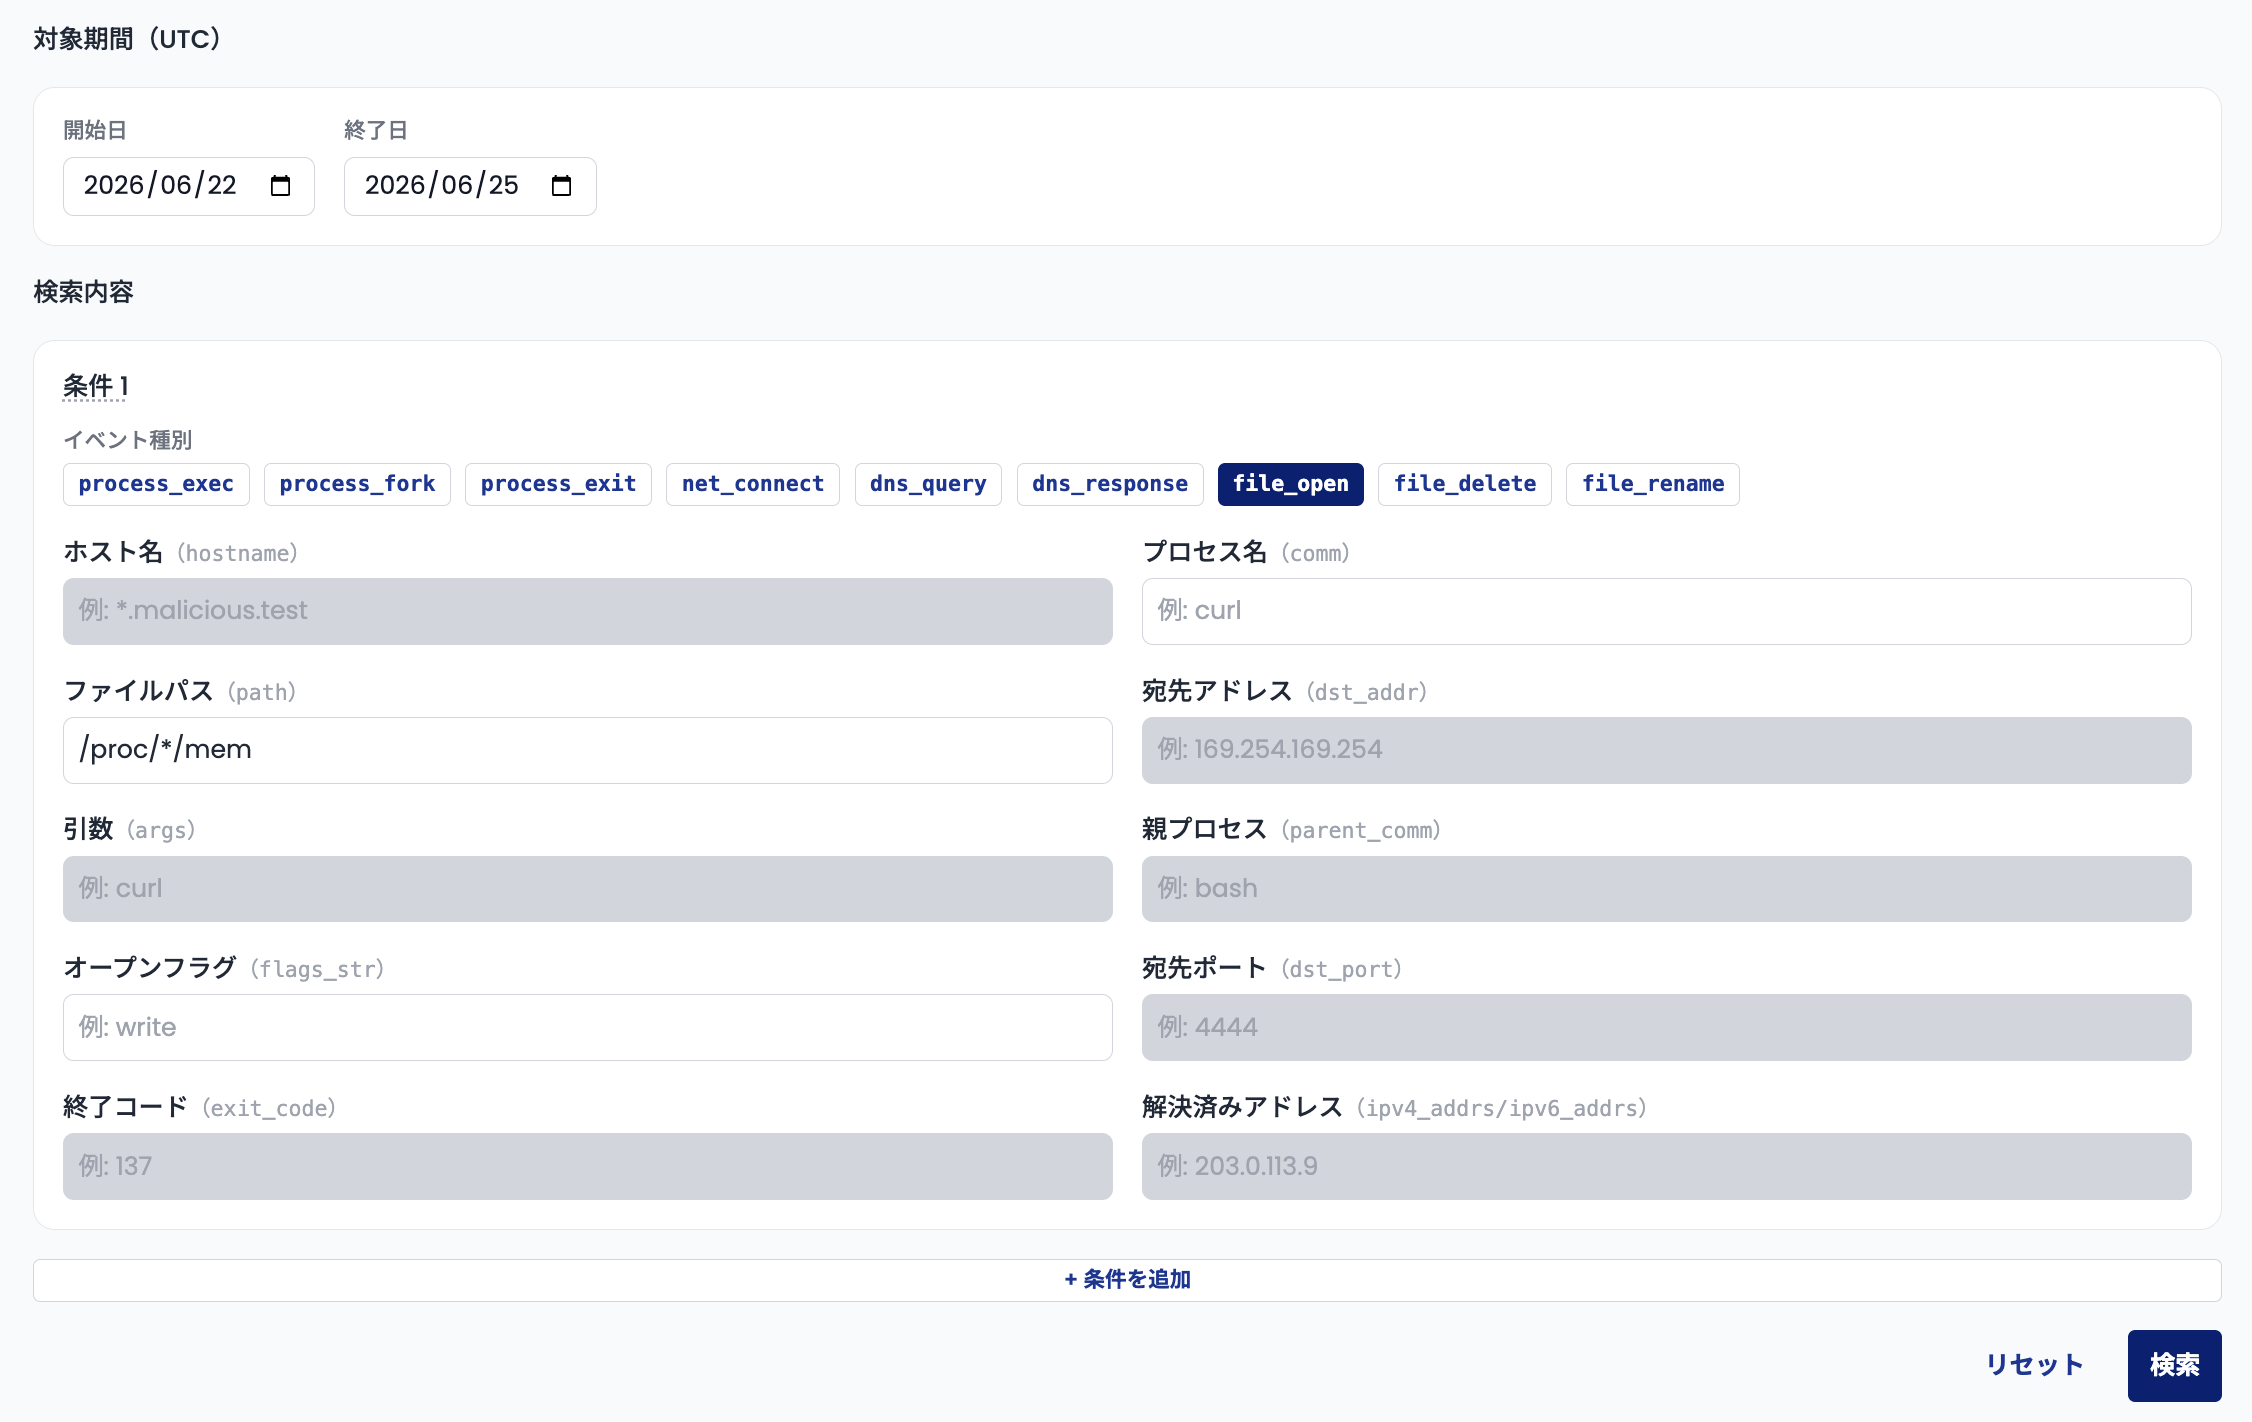
<p>From the Takumi Runner console, you can <a href="https://shisho.dev/docs/t/runner/features/trace-search">search the contents of the collected trace logs</a>. You can check whether the CI/CD jobs that ran during a supply-chain incident were affected.</p>
<p><img decoding="async" loading="lazy" alt="Search results" src="https://shisho.dev/docs/assets/images/trace-search-results-f60887104370d8c0fc20b3d2ac58a145.png" width="2664" height="1652" class="img_aV4l"></p>
<p><strong>Threat detection</strong></p>
<p><a href="https://shisho.dev/docs/r/202608-takumi-runner-threat-detection">Threat detection</a> proactively investigates the impact of a supply-chain incident based on the trace logs and notifies you if you are affected. Since it removes the need to investigate yourself, it addresses gaps in expertise and the risk of missing an incident.</p>
<p><img decoding="async" loading="lazy" alt="Responding to a supply-chain incident: before vs. with threat detection" src="data:image/svg+xml;base64,PHN2ZyB4bWxucz0iaHR0cDovL3d3dy53My5vcmcvMjAwMC9zdmciIHhtbG5zOnhsaW5rPSJodHRwOi8vd3d3LnczLm9yZy8xOTk5L3hsaW5rIiB3aWR0aD0iMTYwMCIgaGVpZ2h0PSI4MzgiIHZpZXdCb3g9IjAgMCAxNjAwIDgzOCIgcm9sZT0iaW1nIiBmb250LWZhbWlseT0iJ0hpcmFnaW5vIEtha3UgR290aGljIFByb04nLCAnSGlyYWdpbm8gU2FucycsICdZdSBHb3RoaWMnLCBNZWlyeW8sICdOb3RvIFNhbnMgSlAnLCBzYW5zLXNlcmlmIj4KICA8dGl0bGU+UmVzcG9uZGluZyB0byBhIHN1cHBseS1jaGFpbiBpbmNpZGVudDogYmVmb3JlIHZzLiB3aXRoIHRocmVhdCBkZXRlY3Rpb248L3RpdGxlPgogIDxkZWZzPgogICAgPCEtLSB0aGljayBibG9jayBhcnJvdywgNjQgd2lkZSB4IDQ0IHRhbGwsIHBvaW50aW5nIHJpZ2h0OyBmaWxsIHNldCBwZXIgdXNlIC0tPgogICAgPHBvbHlnb24gaWQ9ImJsb2NrLWFycm93IiBwb2ludHM9IjAsLTExIDM4LC0xMSAzOCwtMjIgNjQsMCAzOCwyMiAzOCwxMSAwLDExIi8+CiAgICA8IS0tIGNsaXBib2FyZCBpY29uICg5MCB4IDExNiwgdG9wLWxlZnQgYXQgMCwwKTsgZnJhbWUgY29sb3IgPSBjdXJyZW50Q29sb3I7IGNoZWNrIG1hcmtzIGRyYXduIHNlcGFyYXRlbHkgLS0+CiAgICA8ZyBpZD0iY2xpcGJvYXJkIiBmaWxsPSJub25lIiBzdHJva2U9ImN1cnJlbnRDb2xvciIgc3Ryb2tlLXdpZHRoPSI1IiBzdHJva2UtbGluZWNhcD0icm91bmQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiPgogICAgICA8cmVjdCB4PSIwIiB5PSI4IiB3aWR0aD0iOTAiIGhlaWdodD0iMTA4IiByeD0iOCIgZmlsbD0iI2ZmZmZmZiIvPgogICAgICA8cmVjdCB4PSIyNyIgeT0iMCIgd2lkdGg9IjM2IiBoZWlnaHQ9IjE4IiByeD0iNSIgZmlsbD0iY3VycmVudENvbG9yIiBzdHJva2U9Im5vbmUiLz4KICAgICAgPHBhdGggZD0iTTQ3IDQzIEg3NyBNNDcgNjcgSDc3IE00NyA5MSBINzciIHN0cm9rZS13aWR0aD0iNCIvPgogICAgPC9nPgogICAgPHBhdGggaWQ9ImNsaXBib2FyZC1jaGVja3MiIGQ9Ik0xNyA0MyBMMjUgNTEgTDM5IDM1IE0xNyA2NyBMMjUgNzUgTDM5IDU5IE0xNyA5MSBMMjUgOTkgTDM5IDgzIiBmaWxsPSJub25lIiBzdHJva2Utd2lkdGg9IjQuNSIgc3Ryb2tlLWxpbmVjYXA9InJvdW5kIiBzdHJva2UtbGluZWpvaW49InJvdW5kIi8+CiAgPC9kZWZzPgoKICA8cmVjdCB3aWR0aD0iMTYwMCIgaGVpZ2h0PSI4MzgiIGZpbGw9IiNmZmZmZmYiLz4KCiAgPCEtLSB0aXRsZSAtLT4KICA8dGV4dCB4PSI4MDAiIHk9IjcyIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjQyIiBmb250LXdlaWdodD0iYm9sZCIgZmlsbD0iIzI0MjkyZiI+UmVzcG9uZGluZyB0byBhIHN1cHBseS1jaGFpbiBpbmNpZGVudDwvdGV4dD4KCiAgPCEtLSA9PT09PT09PT09PT09PT09PT09PT0gcm93IDE6IGJlZm9yZSA9PT09PT09PT09PT09PT09PT09PT0gLS0+CiAgPHJlY3QgeD0iNDAiIHk9IjExOCIgd2lkdGg9IjE1MjAiIGhlaWdodD0iMzEzIiByeD0iMTgiIGZpbGw9IiNmNmY0ZjQiLz4KICA8cmVjdCB4PSI2MiIgeT0iMjcwIiB3aWR0aD0iMTUwIiBoZWlnaHQ9IjUwIiByeD0iMjUiIGZpbGw9IiM5YjZiNmIiLz4KICA8dGV4dCB4PSIxMzciIHk9IjMwNCIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIyNiIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiNmZmZmZmYiPkJlZm9yZTwvdGV4dD4KCiAgPCEtLSBzdGVwIDE6IGNoZWNrIGJsb2dzIC8gWCAoc21hcnRwaG9uZSBmZWVkLCBmaW5nZXIgdGFwcGluZyB0aGUgc2NyZWVuKSAtLT4KICA8dGV4dCB4PSI0MzAiIHk9IjE3NCIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIzNiIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiM1ZjVmNWYiPkNoZWNrIGJsb2dzICZhbXA7IFg8L3RleHQ+CiAgPGcgZmlsbD0ibm9uZSIgc3Ryb2tlPSIjOGE3YTdhIiBzdHJva2Utd2lkdGg9IjYiIHN0cm9rZS1saW5lY2FwPSJyb3VuZCIgc3Ryb2tlLWxpbmVqb2luPSJyb3VuZCI+CiAgICA8cmVjdCB4PSIzODQiIHk9IjIxNCIgd2lkdGg9IjkyIiBoZWlnaHQ9IjE2MSIgcng9IjE2IiBmaWxsPSIjZmZmZmZmIi8+CiAgICA8cGF0aCBkPSJNNDE2IDIzMCBINDQzIiBzdHJva2Utd2lkdGg9IjUiLz4KICAgIDxjaXJjbGUgY3g9IjQwNiIgY3k9IjI2MiIgcj0iOSIgZmlsbD0iI2M5YjhiOCIgc3Ryb2tlPSJub25lIi8+CiAgICA8cGF0aCBkPSJNNDIzIDI1NyBINDU3IE00MjMgMjcwIEg0NDggTTQwMyAyOTUgSDQ1NyBNNDAzIDMxMSBINDQ4IE00MDMgMzI3IEg0NTciIHN0cm9rZT0iI2M5YjhiOCIgc3Ryb2tlLXdpZHRoPSI1Ii8+CiAgICA8cGF0aCBkPSJNNDE2IDM1OSBINDQzIiBzdHJva2U9IiNjOWI4YjgiIHN0cm9rZS13aWR0aD0iNSIvPgogIDwvZz4KICA8ZyB0cmFuc2Zvcm09InRyYW5zbGF0ZSg0NjAgMjY0KSByb3RhdGUoLTMwKSBzY2FsZSgxLjEpIiBmaWxsPSJub25lIiBzdHJva2UtbGluZWNhcD0icm91bmQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiPgogICAgPHBhdGggZD0iTS0yMC44IC00IEEyNCAyNCAwIDAgMSAyMC44IC00IE0tMTQuNCAtMSBBMTcgMTcgMCAwIDEgMTQuNCAtMSIgc3Ryb2tlPSIjZDM3MDZjIiBzdHJva2Utd2lkdGg9IjMuNiIvPgogICAgPHBhdGggZD0iTS04IDggQTggOCAwIDAgMSA4IDggTDggMzYgQTQgNCAwIDAgMSAxNiAzNiBBNCA0IDAgMCAxIDI0IDM2IEE2IDYgMCAwIDEgMzAgNDIgTDMwIDYwIEExMCAxMCAwIDAgMSAyMCA3MCBMLTYgNzAgQTEwIDEwIDAgMCAxIC0xNiA2MCBMLTE2IDQ2IFEtMTYgNDAgLTggNDAgWiIgZmlsbD0iI2ZmZmZmZiIgc3Ryb2tlPSIjOGE3YTdhIiBzdHJva2Utd2lkdGg9IjQuNSIvPgogIDwvZz4KICA8ZWxsaXBzZSBjeD0iNTEwIiBjeT0iMzgxIiByeD0iMTEyIiByeT0iMjYiIGZpbGw9IiNmZmZmZmYiIHN0cm9rZT0iI2QzNzA2YyIgc3Ryb2tlLXdpZHRoPSIzIi8+CiAgPHRleHQgeD0iNTEwIiB5PSIzODgiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMjAiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjZDM3MDZjIj5NaWdodCBtaXNzIGl04oCmPC90ZXh0PgoKICA8dXNlIHhsaW5rOmhyZWY9IiNibG9jay1hcnJvdyIgeD0iNjI4IiB5PSIyOTUiIGZpbGw9IiNiOGE5YTkiLz4KCiAgPCEtLSBzdGVwIDI6IHNlYXJjaCB0aGUgbG9ncyB5b3Vyc2VsZiAoc3RhY2sgb2YgbG9nIHBhZ2VzICsgbWFnbmlmaWVyKSAtLT4KICA8dGV4dCB4PSI4OTAiIHk9IjE3NCIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIzNiIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiM1ZjVmNWYiPlNlYXJjaCBsb2dzIHlvdXJzZWxmPC90ZXh0PgogIDxnIGZpbGw9Im5vbmUiIHN0cm9rZT0iIzlhODY4NiIgc3Ryb2tlLXdpZHRoPSI2IiBzdHJva2UtbGluZWNhcD0icm91bmQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiPgogICAgPHJlY3QgeD0iODM2IiB5PSIyMTQiIHdpZHRoPSIxMjEiIGhlaWdodD0iMTQ4IiByeD0iOCIgZmlsbD0iI2Y0ZWRlZCIgc3Ryb2tlPSIjYjM5YzljIi8+CiAgICA8cmVjdCB4PSI4MjMiIHk9IjIyNyIgd2lkdGg9IjEyMSIgaGVpZ2h0PSIxNDgiIHJ4PSI4IiBmaWxsPSIjZmZmZmZmIi8+CiAgICA8cGF0aCBkPSJNODQyIDI1NCBIOTI1IE04NDIgMjc0IEg5MDkgTTg0MiAyOTQgSDkyOCBNODQyIDMxNCBIOTAxIE04NDIgMzM1IEg5MjMgTTg0MiAzNTUgSDkxMiIgc3Ryb2tlPSIjYjM5YzljIiBzdHJva2Utd2lkdGg9IjUiLz4KICA8L2c+CiAgPGNpcmNsZSBjeD0iOTUwIiBjeT0iMjY3IiByPSIzNSIgZmlsbD0iI2ZmZmZmZiIgZmlsbC1vcGFjaXR5PSIwLjUiIHN0cm9rZT0iI2QzNzA2YyIgc3Ryb2tlLXdpZHRoPSI4Ii8+CiAgPHBhdGggZD0iTTk3NSAyOTIgTDEwMDYgMzIzIiBzdHJva2U9IiNkMzcwNmMiIHN0cm9rZS13aWR0aD0iMTIiIHN0cm9rZS1saW5lY2FwPSJyb3VuZCIvPgogIDxlbGxpcHNlIGN4PSI5NzAiIGN5PSIzODEiIHJ4PSIxMDAiIHJ5PSIyNiIgZmlsbD0iI2ZmZmZmZiIgc3Ryb2tlPSIjZDM3MDZjIiBzdHJva2Utd2lkdGg9IjMiLz4KICA8dGV4dCB4PSI5NzAiIHk9IjM4OCIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIyMCIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiNkMzcwNmMiPlN1Y2ggYSBoYXNzbGXigKY8L3RleHQ+CgogIDx1c2UgeGxpbms6aHJlZj0iI2Jsb2NrLWFycm93IiB4PSIxMDg4IiB5PSIyOTUiIGZpbGw9IiNiOGE5YTkiLz4KCiAgPCEtLSBzdGVwIDM6IHBvc3QtaW5jaWRlbnQgcmVzcG9uc2UgKGNsaXBib2FyZCkgLS0+CiAgPHRleHQgeD0iMTM1MCIgeT0iMTc0IiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjM2IiBmb250LXdlaWdodD0iYm9sZCIgZmlsbD0iIzVmNWY1ZiI+UmVzcG9uZDwvdGV4dD4KICA8dXNlIHhsaW5rOmhyZWY9IiNjbGlwYm9hcmQiIHRyYW5zZm9ybT0idHJhbnNsYXRlKDEyOTAgMjE0KSBzY2FsZSgxLjM0NCkiIGNvbG9yPSIjOGE3YTdhIi8+CiAgPHVzZSB4bGluazpocmVmPSIjY2xpcGJvYXJkLWNoZWNrcyIgdHJhbnNmb3JtPSJ0cmFuc2xhdGUoMTI5MCAyMTQpIHNjYWxlKDEuMzQ0KSIgc3Ryb2tlPSIjYTA5MDkwIi8+CiAgPHRleHQgeD0iMTM1MCIgeT0iNDAyIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjIyIiBmaWxsPSIjN2E3YTdhIj4oaWYgYWZmZWN0ZWQpPC90ZXh0PgoKICA8IS0tID09PT09PT09PT09PT09PT09PT09PSByb3cgMjogd2l0aCB0aHJlYXQgZGV0ZWN0aW9uID09PT09PT09PT09PT09PT09PT09PSAtLT4KICA8cmVjdCB4PSI0MCIgeT0iNDcxIiB3aWR0aD0iMTUyMCIgaGVpZ2h0PSIzMjciIHJ4PSIxOCIgZmlsbD0iI2VlZjRmYyIvPgogIDxyZWN0IHg9IjYyIiB5PSI2MjkiIHdpZHRoPSIyNjAiIGhlaWdodD0iNTAiIHJ4PSIyNSIgZmlsbD0iIzJmNmZkNiIvPgogIDx0ZXh0IHg9IjE5MiIgeT0iNjYzIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjI2IiBmb250LXdlaWdodD0iYm9sZCIgZmlsbD0iI2ZmZmZmZiI+VGhyZWF0IGRldGVjdGlvbjwvdGV4dD4KCiAgPCEtLSBzdGVwOiBSdW5uZXIgZG9lcyBpdCBhdXRvbWF0aWNhbGx5IChzaGllbGQgd2l0aCByYWRhciBzd2VlcCwgYmVsbCBhdHRhY2hlZCkg4oCUIHJlcGxhY2VzIHN0ZXBzIDEgYW5kIDIgLS0+CiAgPHRleHQgeD0iNjYwIiB5PSI1MjciIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMzYiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjNWY1ZjVmIj5SdW5uZXIgaGFuZGxlcyBpdCBmb3IgeW91PC90ZXh0PgogIDxnIHRyYW5zZm9ybT0idHJhbnNsYXRlKDY2MCA2NTQpIHNjYWxlKDEuNCkiPgogICAgPHBhdGggZD0iTTAgLTYyIEMyMiAtNTAgNDIgLTQ0IDU2IC00NCBDNTYgLTIgNDAgMzQgMCA2MiBDLTQwIDM0IC01NiAtMiAtNTYgLTQ0IEMtNDIgLTQ0IC0yMiAtNTAgMCAtNjIgWiIgZmlsbD0iI2VhZjNmZiIgc3Ryb2tlPSIjMmY2ZmQ2IiBzdHJva2Utd2lkdGg9IjQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiLz4KICAgIDxjaXJjbGUgY3g9IjAiIGN5PSItNiIgcj0iMzIiIGZpbGw9IiNmZmZmZmYiIHN0cm9rZT0iIzJmNmZkNiIgc3Ryb2tlLXdpZHRoPSIyLjUiLz4KICAgIDxjaXJjbGUgY3g9IjAiIGN5PSItNiIgcj0iMTgiIGZpbGw9Im5vbmUiIHN0cm9rZT0iIzlmYzBlYSIgc3Ryb2tlLXdpZHRoPSIxLjUiLz4KICAgIDxwYXRoIGQ9Ik0tMzIgLTYgSDMyIE0wIC0zOCBWMjYiIHN0cm9rZT0iIzlmYzBlYSIgc3Ryb2tlLXdpZHRoPSIxLjUiLz4KICAgIDxwYXRoIGQ9Ik0wIC02IEwwIC0zOCBBMzIgMzIgMCAwIDEgMjcuNyAtMjIgWiIgZmlsbD0iIzJmNmZkNiIgZmlsbC1vcGFjaXR5PSIwLjMiLz4KICAgIDxwYXRoIGQ9Ik0wIC02IEwyNy43IC0yMiIgc3Ryb2tlPSIjMmY2ZmQ2IiBzdHJva2Utd2lkdGg9IjIuNSIgc3Ryb2tlLWxpbmVjYXA9InJvdW5kIi8+CiAgICA8Y2lyY2xlIGN4PSIxMiIgY3k9Ii0yNCIgcj0iNC41IiBmaWxsPSIjMmZhMzZiIi8+CiAgPC9nPgogIDxnIHRyYW5zZm9ybT0idHJhbnNsYXRlKDc0MiA2MDcpIHNjYWxlKDEuMDUpIj4KICAgIDxwYXRoIGQ9Ik0tMjQgMTYgQy0yNCAtMTQgLTE0IC0yOCAwIC0zMCBDMTQgLTI4IDI0IC0xNCAyNCAxNiBMMzAgMjQgSC0zMCBaIiBmaWxsPSIjZmZmZmZmIiBzdHJva2U9IiMyZjZmZDYiIHN0cm9rZS13aWR0aD0iNC41IiBzdHJva2UtbGluZWpvaW49InJvdW5kIi8+CiAgICA8Y2lyY2xlIGN4PSIwIiBjeT0iMzIiIHI9IjYiIGZpbGw9IiMyZjZmZDYiLz4KICAgIDxjaXJjbGUgY3g9IjAiIGN5PSItMzQiIHI9IjQiIGZpbGw9IiMyZjZmZDYiLz4KICAgIDxjaXJjbGUgY3g9IjI2IiBjeT0iLTI0IiByPSIxMyIgZmlsbD0iIzJmYTM2YiIgc3Ryb2tlPSIjZmZmZmZmIiBzdHJva2Utd2lkdGg9IjMiLz4KICAgIDx0ZXh0IHg9IjI2IiB5PSItMTciIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTgiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjZmZmZmZmIj4hPC90ZXh0PgogIDwvZz4KICA8ZWxsaXBzZSBjeD0iNzUwIiBjeT0iNzQ3IiByeD0iMTcwIiByeT0iMjciIGZpbGw9IiNmZmZmZmYiIHN0cm9rZT0iIzJjOGE1OCIgc3Ryb2tlLXdpZHRoPSIzIi8+CiAgPHRleHQgeD0iNzUwIiB5PSI3NTQiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMjAiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjMmM4YTU4Ij5Zb3UgZ2V0IG5vdGlmaWVkIGlmIGFmZmVjdGVkPC90ZXh0PgoKICA8dXNlIHhsaW5rOmhyZWY9IiNibG9jay1hcnJvdyIgeD0iMTA4OCIgeT0iNjU0IiBmaWxsPSIjMmY2ZmQ2Ii8+CgogIDwhLS0gcG9zdC1pbmNpZGVudCByZXNwb25zZSAoYWZ0ZXIpOiBzYW1lIGljb24sIHNhbWUgY29sdW1uIGFzIGFib3ZlIC0tPgogIDx0ZXh0IHg9IjEzNTAiIHk9IjUyNyIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIzNiIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiM1ZjVmNWYiPlJlc3BvbmQ8L3RleHQ+CiAgPHVzZSB4bGluazpocmVmPSIjY2xpcGJvYXJkIiB0cmFuc2Zvcm09InRyYW5zbGF0ZSgxMjkwIDU3Nikgc2NhbGUoMS4zNDQpIiBjb2xvcj0iIzJmNmZkNiIvPgogIDx1c2UgeGxpbms6aHJlZj0iI2NsaXBib2FyZC1jaGVja3MiIHRyYW5zZm9ybT0idHJhbnNsYXRlKDEyOTAgNTc2KSBzY2FsZSgxLjM0NCkiIHN0cm9rZT0iIzJmYTM2YiIvPgo8L3N2Zz4K" width="1600" height="838" class="img_aV4l"></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="when-you-exceed-the-free-tier">When You Exceed the Free Tier<a href="https://shisho.dev/docs/r/202609-takumi-runner-cicd-sensor-free-tier#when-you-exceed-the-free-tier" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>The free tier accepts trace logs for up to 3,000 minutes of total job run time per organization per month. Once the 3,000-minute limit is reached, trace logs are no longer accepted after that point, but your CI/CD jobs still run as usual.</p>
<p>To manage trace logs in Takumi Runner beyond 3,000 minutes, you need a Takumi subscription and Runner enabled.</p>
<p>For the pricing details of the cicd-sensor integration and Takumi Hosted Runner, see <a href="https://shisho.dev/docs/t/runner/billing">Pricing &amp; Billing</a>.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202609-takumi-runner-cicd-sensor-free-tier#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>The steps to start using the free tier are as follows.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="creating-an-organization">Creating an Organization<a href="https://shisho.dev/docs/r/202609-takumi-runner-cicd-sensor-free-tier#creating-an-organization" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
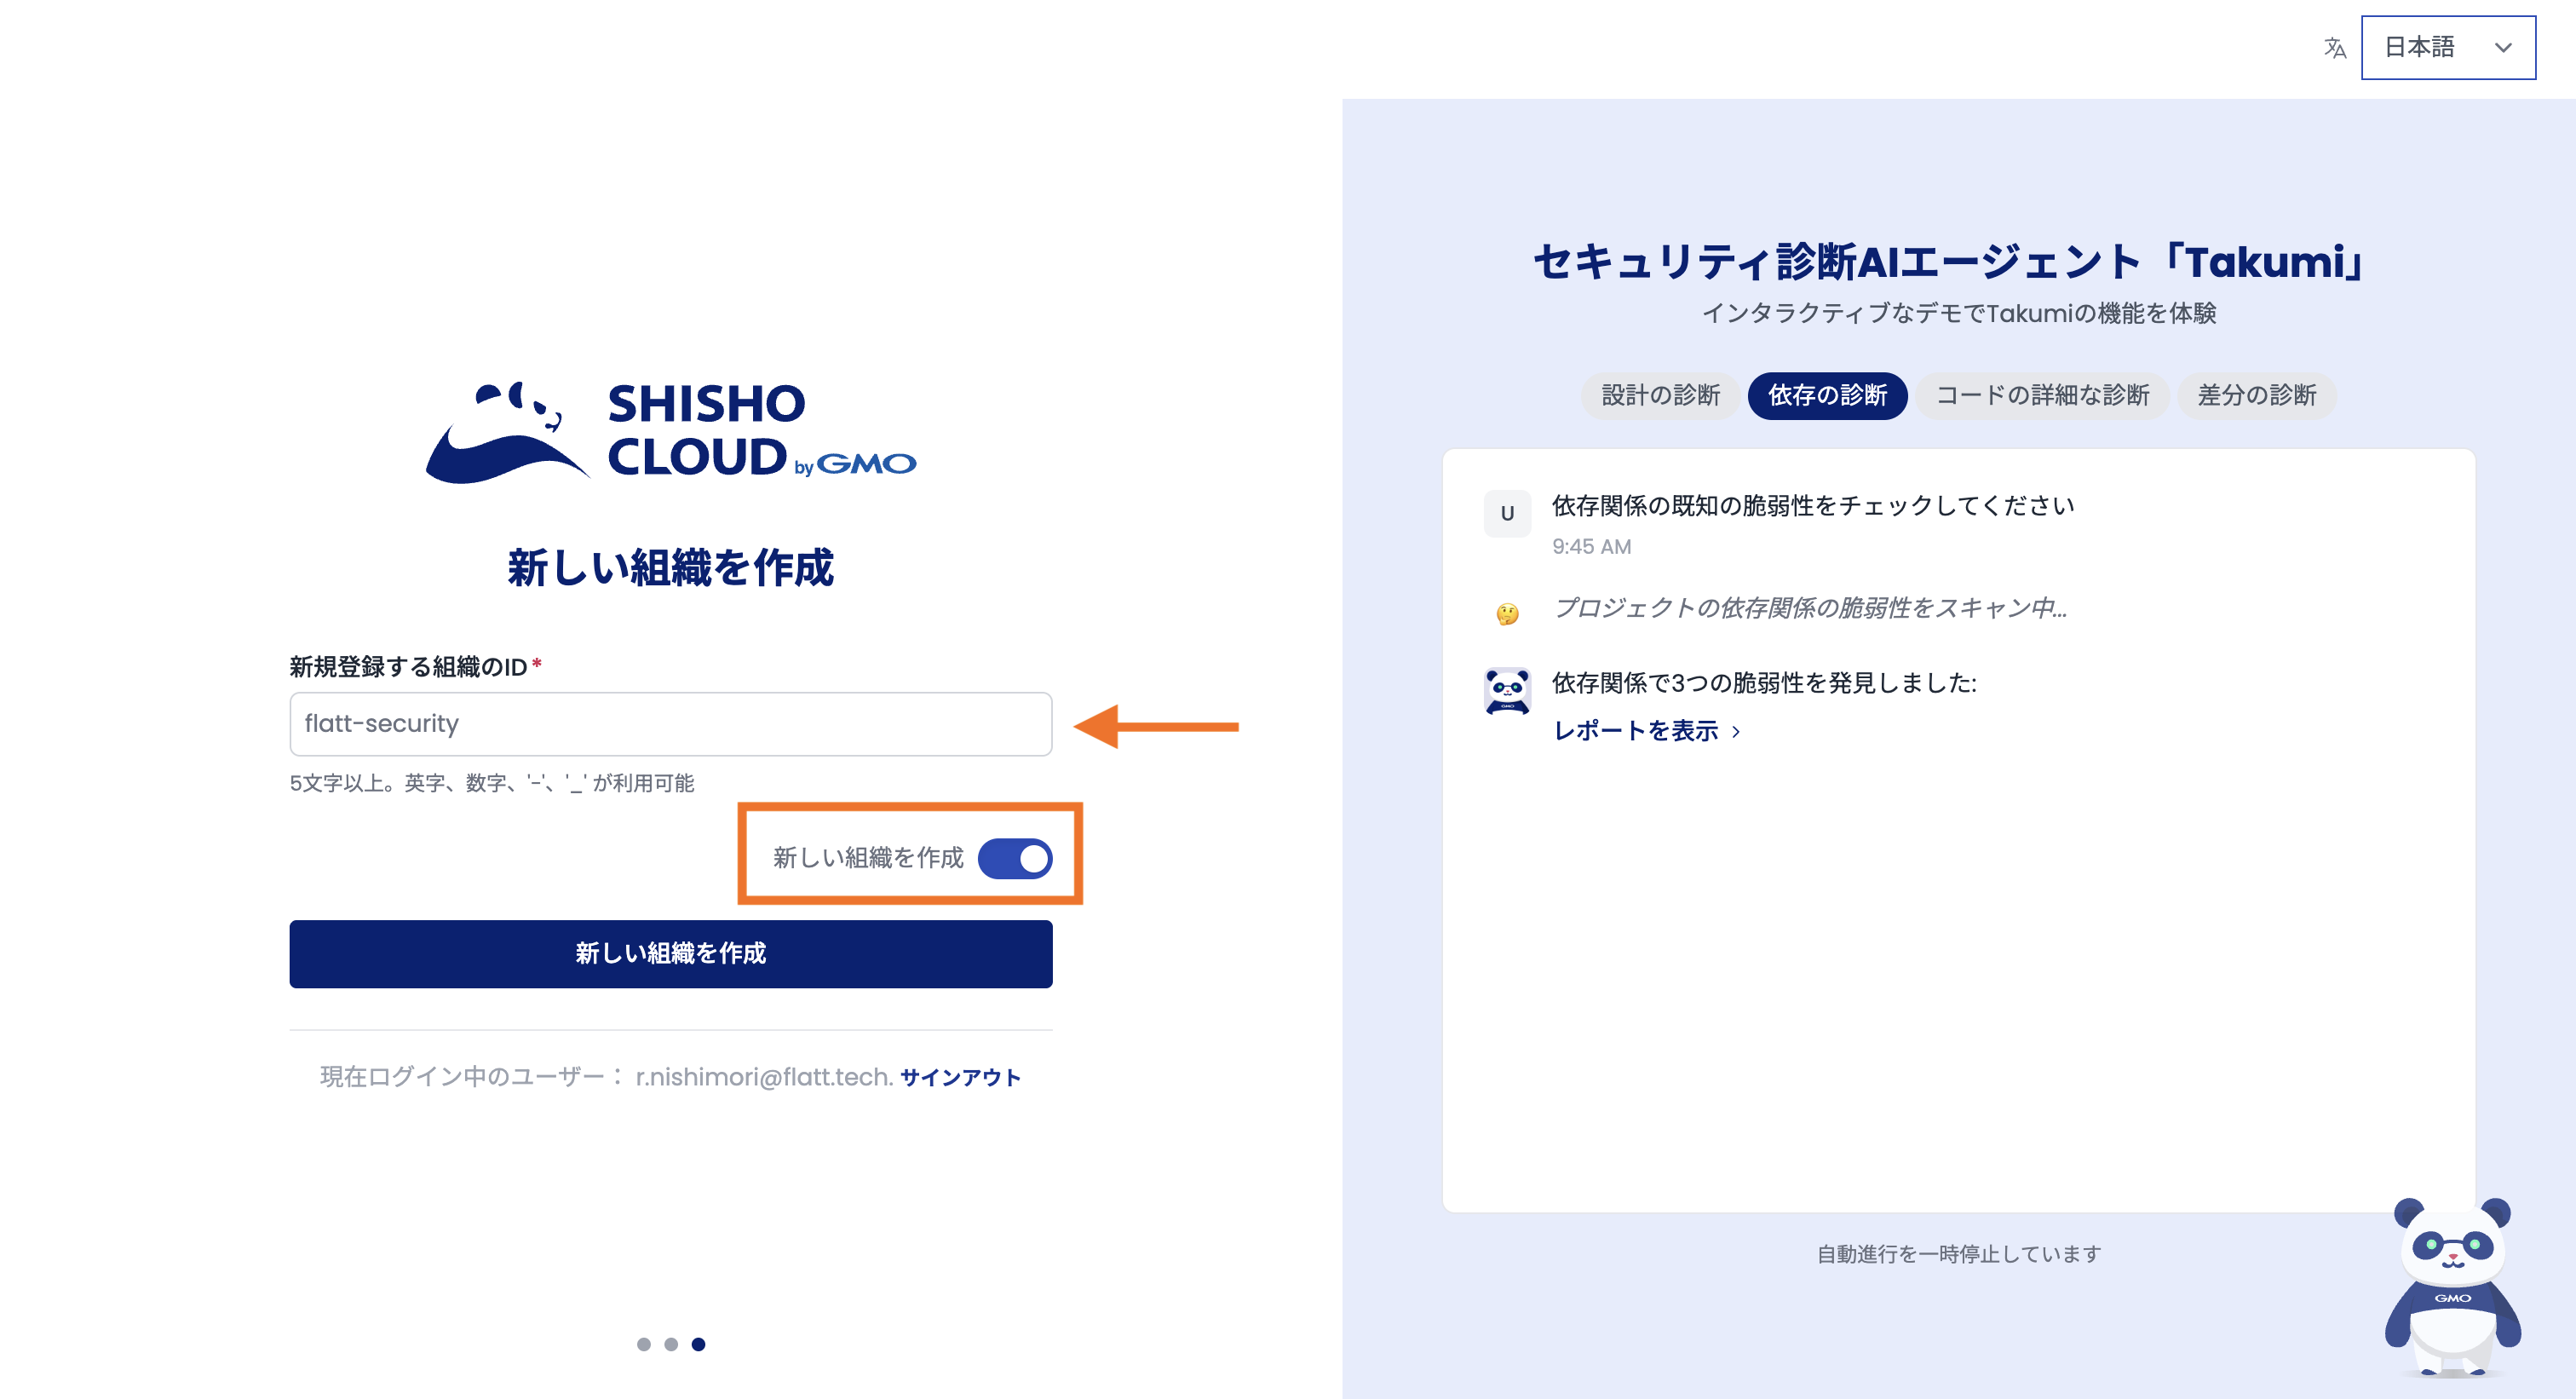
<p>Go to <a href="https://cloud.shisho.dev/hello/takumi" target="_blank" rel="noopener noreferrer">https://cloud.shisho.dev/hello/takumi</a>.</p>
<p><img decoding="async" loading="lazy" alt="Organization registration screen" src="https://shisho.dev/docs/assets/images/create-organization-5cad9e0b8d19343e8e8b67087f4eb9ee.png" width="3024" height="1642" class="img_aV4l"></p>
<ol>
<li>Turn on <strong>Create a new organization</strong> and enter the ID of the organization to register</li>
<li>Press <strong>Create a new organization</strong></li>
</ol>
<p>Once the organization is created, next set up the cicd-sensor integration.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="setting-up-the-cicd-sensor-integration">Setting Up the cicd-sensor Integration<a href="https://shisho.dev/docs/r/202609-takumi-runner-cicd-sensor-free-tier#setting-up-the-cicd-sensor-integration" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>Here we walk through the setup for CI/CD jobs on GitHub-hosted runners. If you use another environment, see the <a href="https://shisho.dev/docs/t/runner/features/cicdsensor-integration">user guide</a>.</p>
<p><strong>Credentials</strong></p>
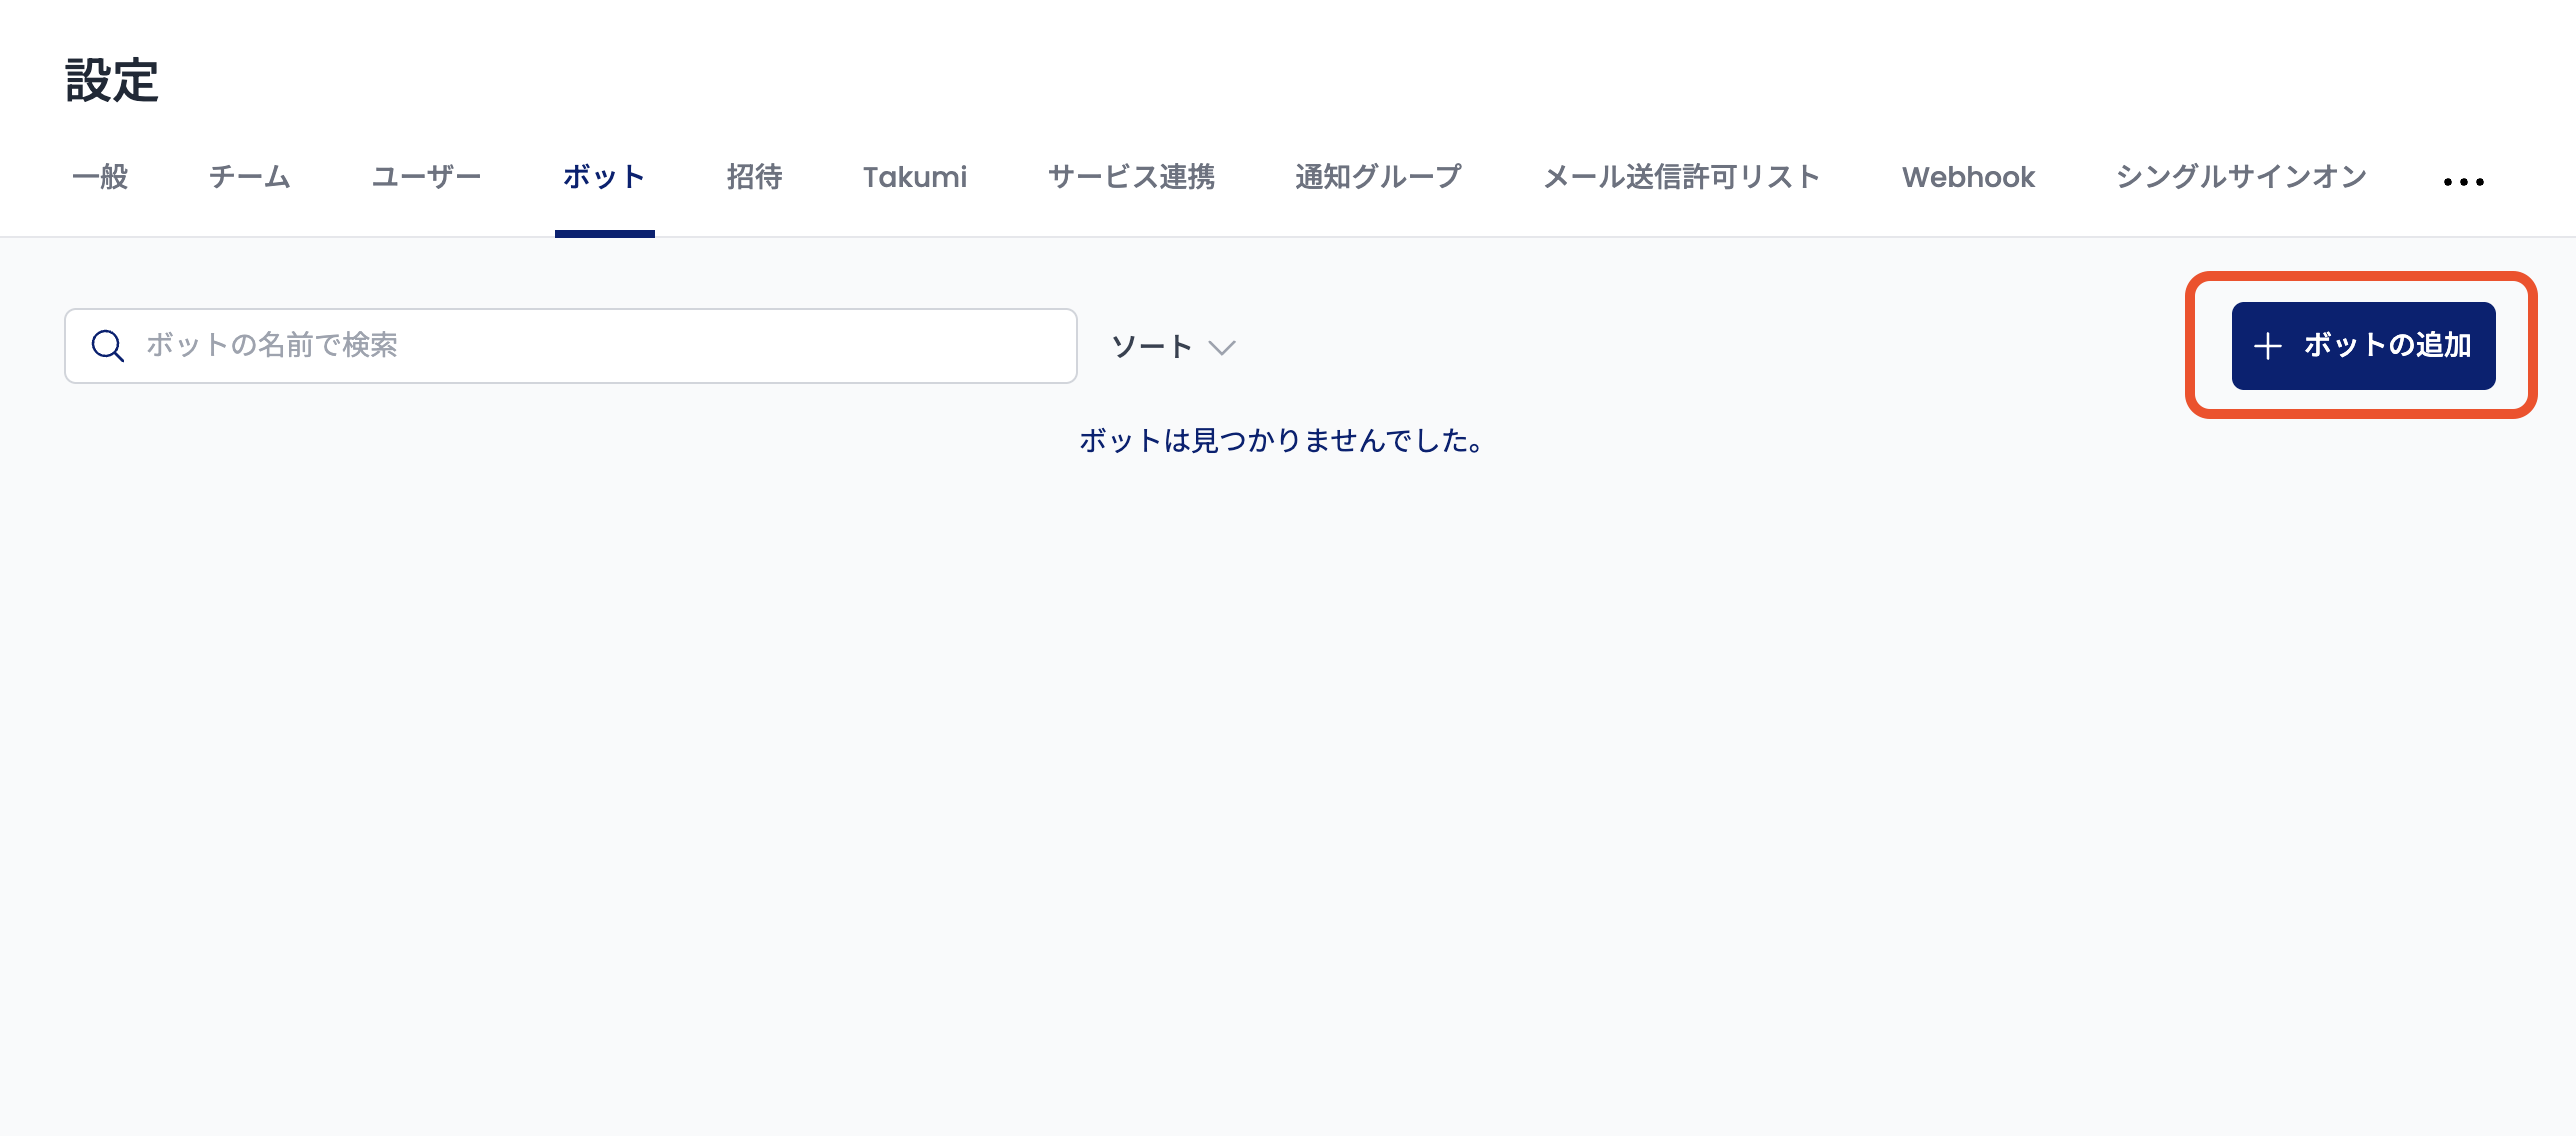
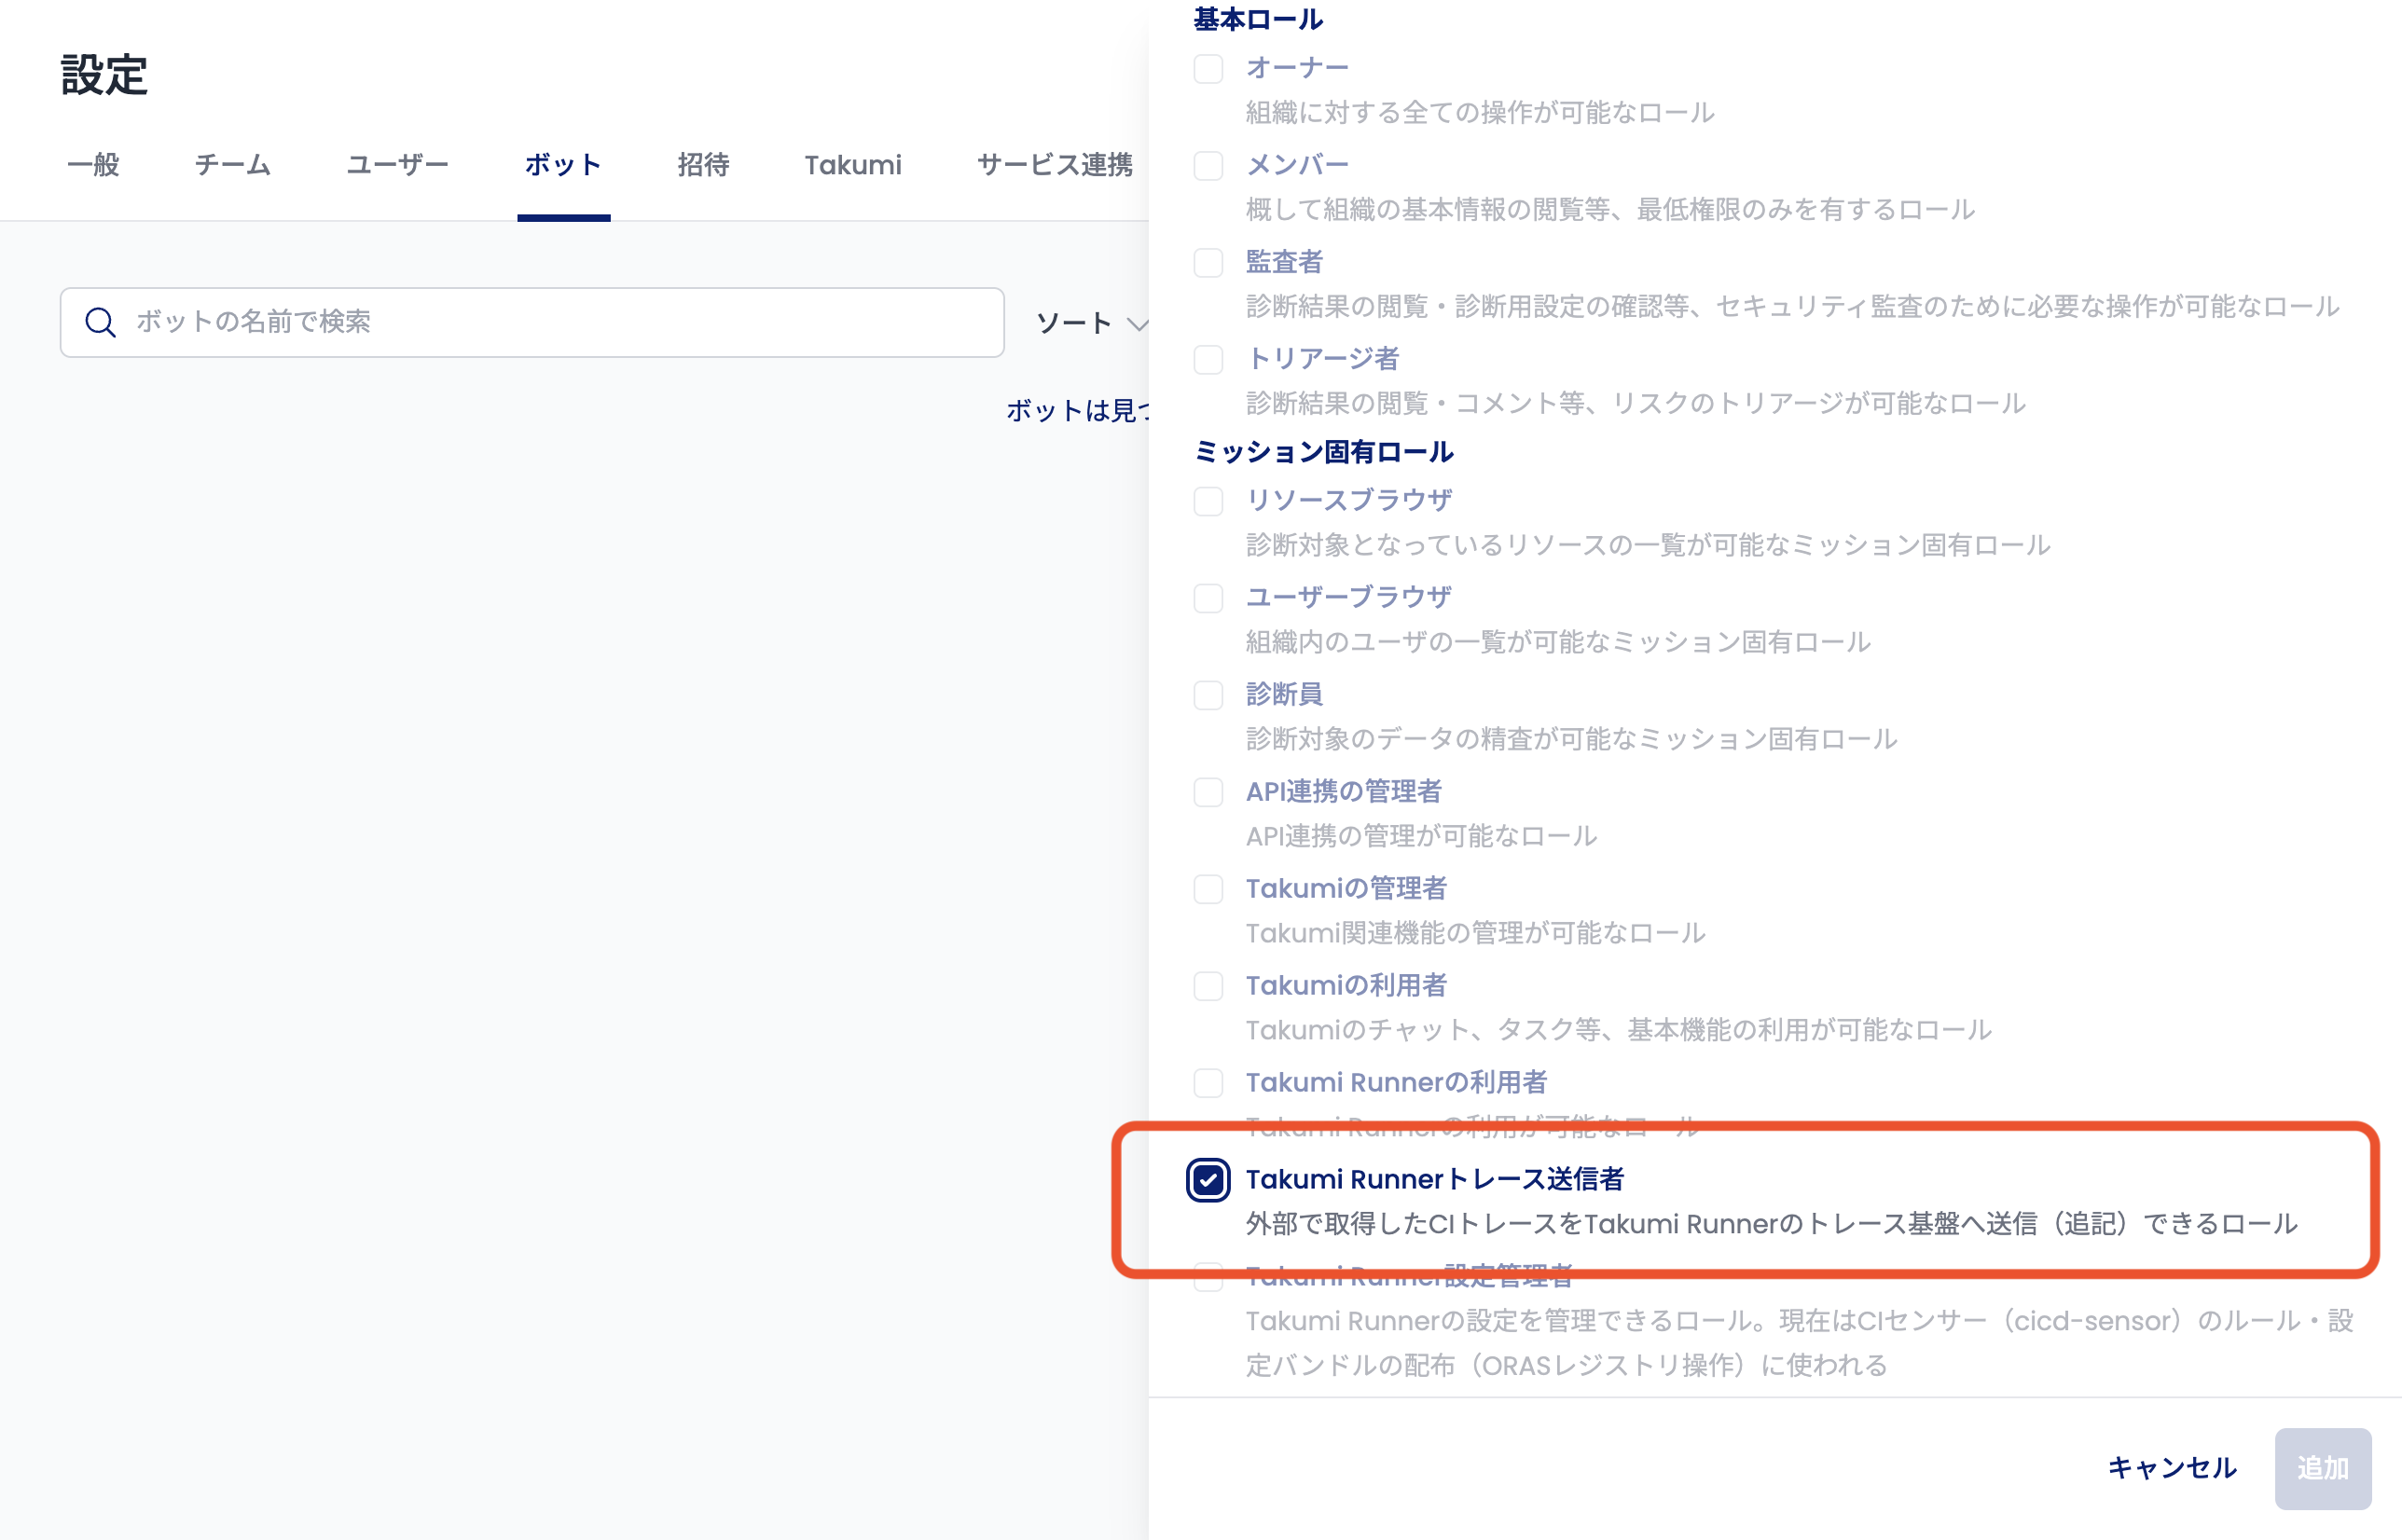
<p>First, create a bot that handles the credentials. In the Takumi console, open <strong>Settings</strong> &gt; <strong>Bots</strong> &gt; <strong>Add bot</strong> and select <strong>Takumi Runner Trace Sender</strong> to open the bot creation screen.</p>
<p><img decoding="async" loading="lazy" alt="Add bot" src="https://shisho.dev/docs/assets/images/cicdsensor-create-bot-9b05b79fb798babcc3c8fac9756656bf.png" width="2576" height="1136" class="img_aV4l"></p>
<p><img decoding="async" loading="lazy" alt="Select Takumi Runner Trace Sender role" src="https://shisho.dev/docs/assets/images/cicdsensor-select-role-ec461a6ab5d4707a7dde136596f4f82a.png" width="2576" height="1652" class="img_aV4l"></p>
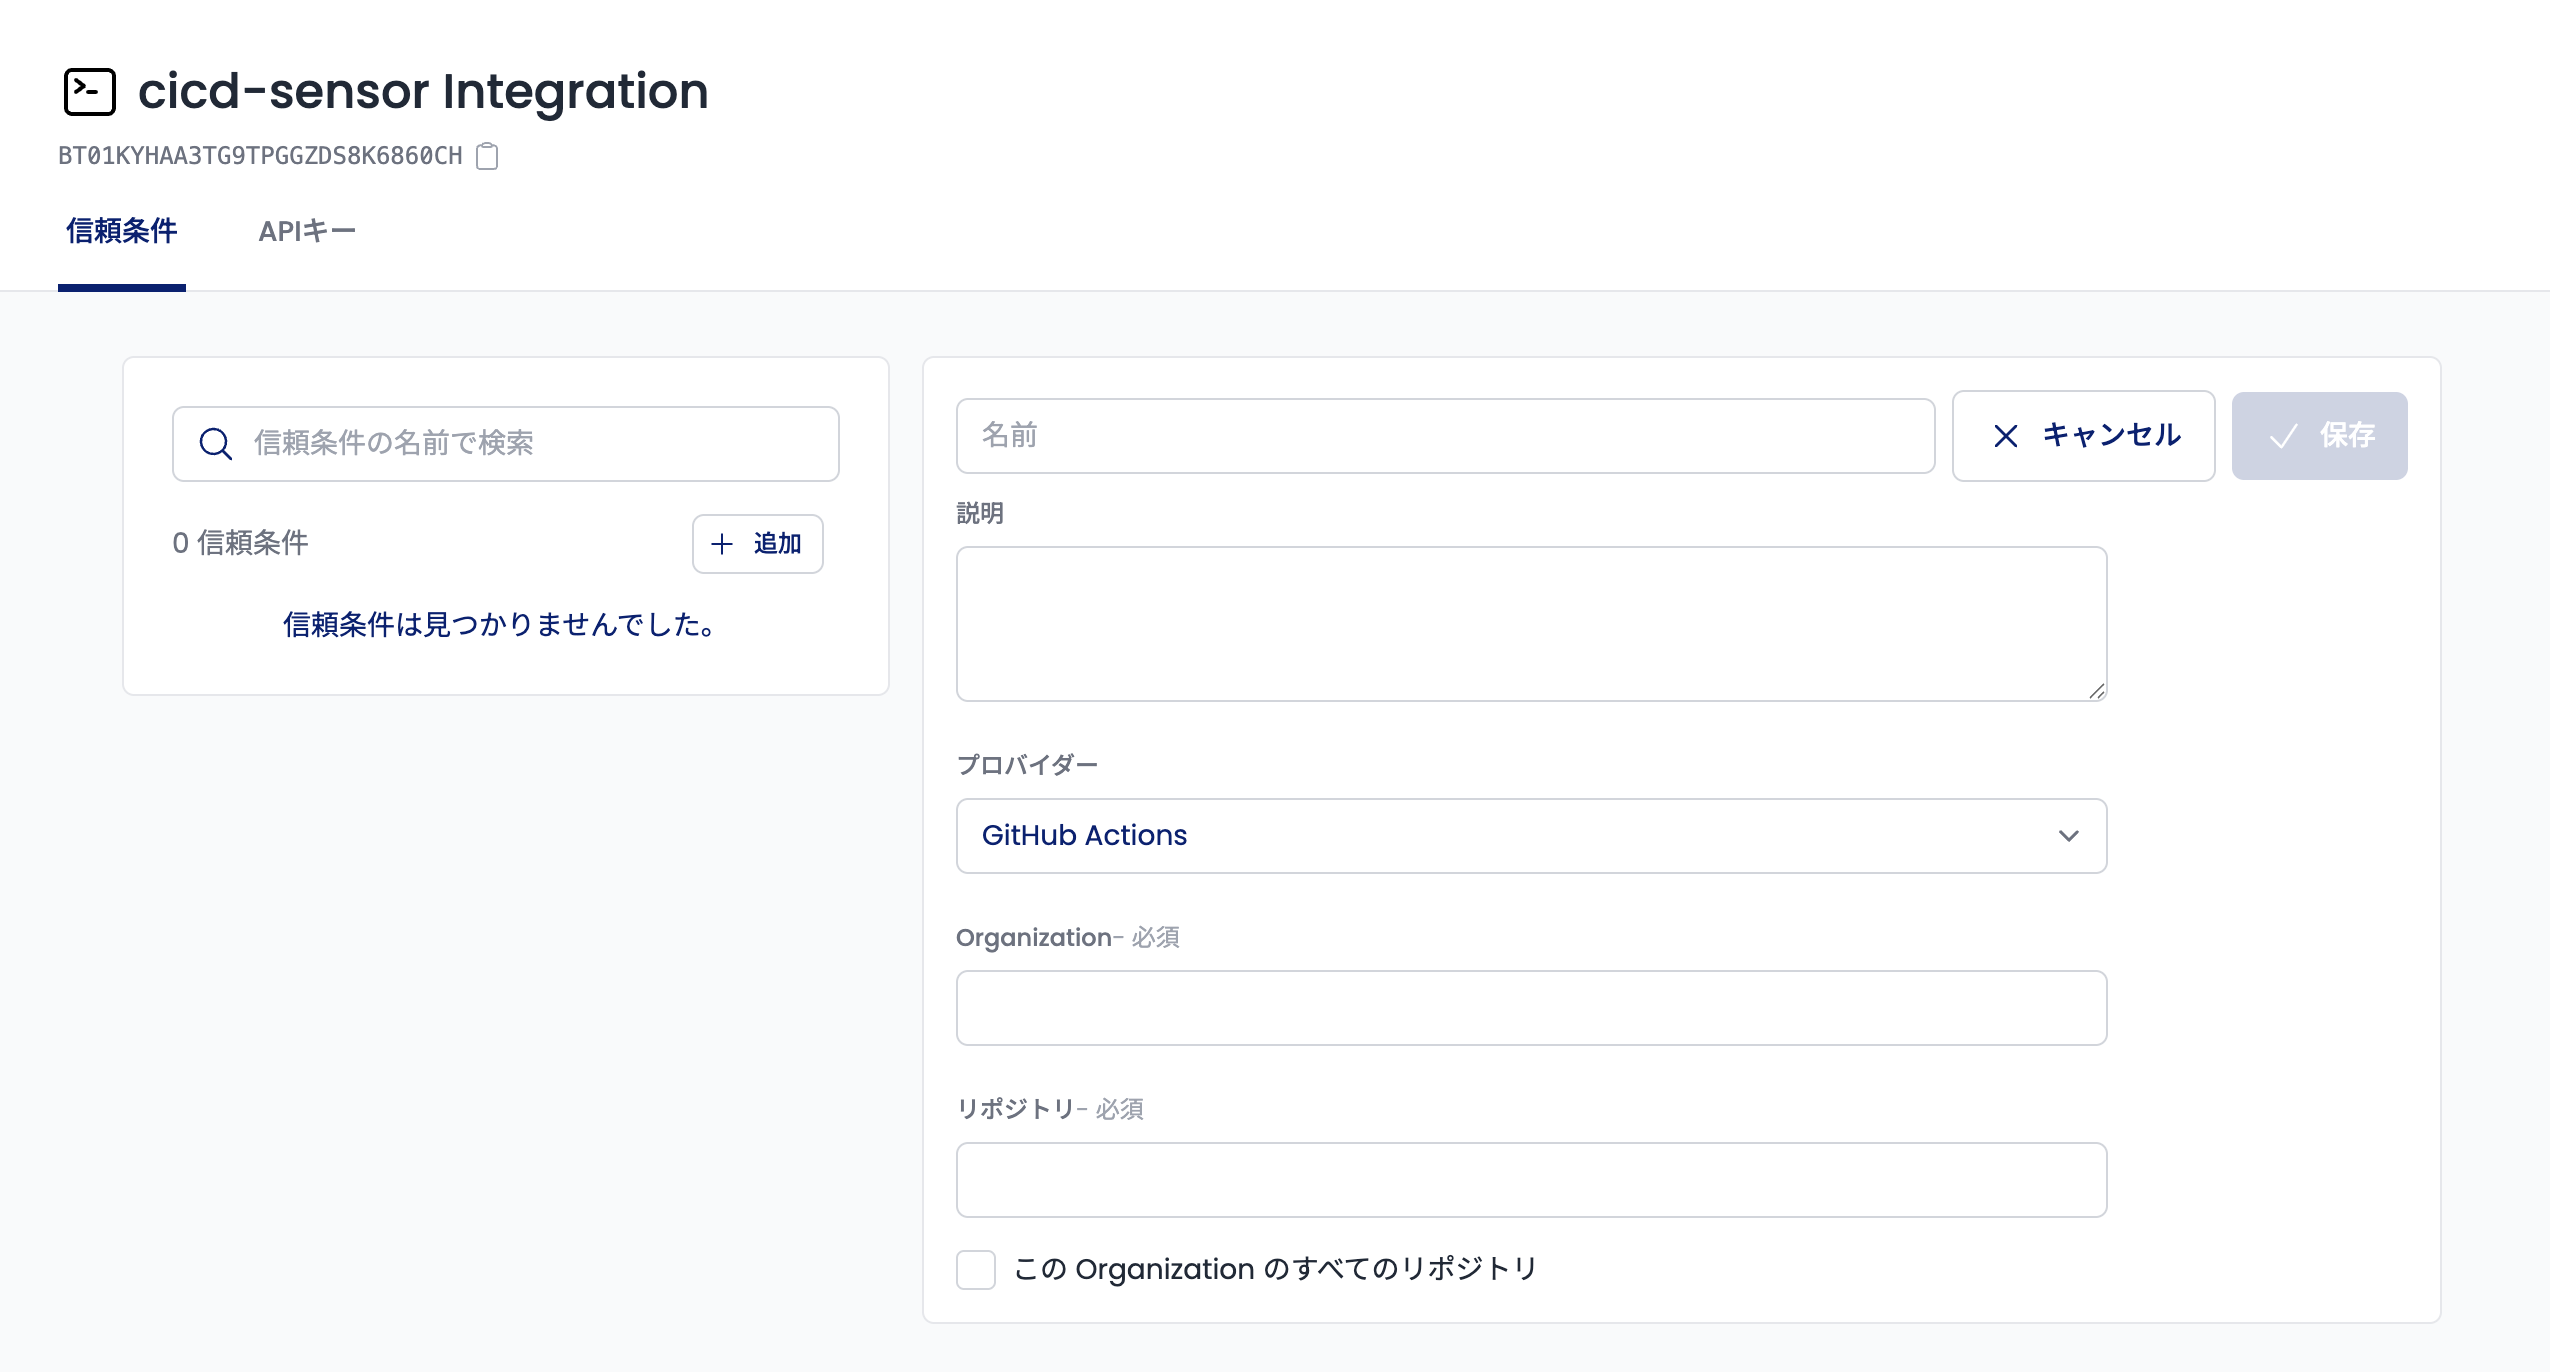
<p>On the bot creation screen, set up a <strong>trust condition</strong>. Enter the <strong>name</strong>, <strong>organization</strong>, and <strong>repository</strong>.</p>
<p><img decoding="async" loading="lazy" alt="Create trust condition" src="https://shisho.dev/docs/assets/images/cicdsensor-trust-condition-2699e94d26df65a1954c2dfe13a0c45a.png" width="2550" height="1372" class="img_aV4l"></p>
<p>Press save to finish creating the bot. Next, create a GitHub workflow.</p>
<p><strong>Creating a GitHub job</strong></p>
<p>Here we create a job that runs <code>echo Hello</code>.</p>
<div class="language-yaml codeBlockContainer_tXdS theme-code-block" style="--prism-color:#393A34;--prism-background-color:#f6f8fa"><div class="codeBlockContent_zXtR"><pre tabindex="0" class="prism-code language-yaml codeBlock_qqWd thin-scrollbar" style="color:#393A34;background-color:#f6f8fa"><code class="codeBlockLines_CmGJ"><span class="token-line" style="color:#393A34"><span class="token key atrule" style="color:#00a4db">jobs</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">  </span><span class="token key atrule" style="color:#00a4db">build</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">    </span><span class="token key atrule" style="color:#00a4db">runs-on</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> ubuntu</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">latest</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">    </span><span class="token key atrule" style="color:#00a4db">environment</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> cicd</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">sensor</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">    </span><span class="token key atrule" style="color:#00a4db">permissions</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">      </span><span class="token key atrule" style="color:#00a4db">contents</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> read</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">      </span><span class="token key atrule" style="color:#00a4db">id-token</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> write</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">    </span><span class="token key atrule" style="color:#00a4db">steps</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">      </span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain"> </span><span class="token key atrule" style="color:#00a4db">id</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> auth</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">        </span><span class="token key atrule" style="color:#00a4db">uses</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> flatt</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">security/shisho</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">cloud</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">action@v1</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">        </span><span class="token key atrule" style="color:#00a4db">with</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">          </span><span class="token key atrule" style="color:#00a4db">bot-id</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> &lt;Bot ID</span><span class="token punctuation" style="color:#393A34">&gt;</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">          </span><span class="token key atrule" style="color:#00a4db">export-token</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> </span><span class="token boolean important" style="color:#36acaa">true</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">          </span><span class="token key atrule" style="color:#00a4db">expires-in-minutes</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> </span><span class="token number" style="color:#36acaa">360</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">      </span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain"> </span><span class="token key atrule" style="color:#00a4db">uses</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> cicd</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">sensor/cicd</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">sensor</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">action@6511eb44c91d71b2b93d71193b1bf2cb18352f66 </span><span class="token comment" style="color:#999988;font-style:italic"># v0.0.38</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">        </span><span class="token key atrule" style="color:#00a4db">with</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">          </span><span class="token key atrule" style="color:#00a4db">manager-url</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> https</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain">//manager.cicdsensor.cloud.shisho.dev</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">          </span><span class="token key atrule" style="color:#00a4db">manager-token</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> $</span><span class="token punctuation" style="color:#393A34">{</span><span class="token punctuation" style="color:#393A34">{</span><span class="token plain"> steps.auth.outputs.token </span><span class="token punctuation" style="color:#393A34">}</span><span class="token punctuation" style="color:#393A34">}</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">      </span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain"> </span><span class="token key atrule" style="color:#00a4db">run</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> echo Hello</span><br></span></code></pre><div class="buttonGroup_yRlK"><button type="button" aria-label="Copy code to clipboard" title="Copy" class="clean-btn"><span class="copyButtonIcons_yBV4" aria-hidden="true"><svg viewBox="0 0 24 24" class="copyButtonIcon_Ctry"><path fill="currentColor" d="M19,21H8V7H19M19,5H8A2,2 0 0,0 6,7V21A2,2 0 0,0 8,23H19A2,2 0 0,0 21,21V7A2,2 0 0,0 19,5M16,1H4A2,2 0 0,0 2,3V17H4V3H16V1Z"></path></svg><svg viewBox="0 0 24 24" class="copyButtonSuccessIcon_FUe1"><path fill="currentColor" d="M21,7L9,19L3.5,13.5L4.91,12.09L9,16.17L19.59,5.59L21,7Z"></path></svg></span></button></div></div></div>
<p>The <code>uses: flatt-security/shisho-cloud-action@v1</code> step obtains the credentials. The <code>uses: cicd-sensor/cicd-sensor-action</code> step runs cicd-sensor.</p>
<p>The connection to Takumi Runner is configured with <code>manager-url: https://manager.cicdsensor.cloud.shisho.dev</code>.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="checking-the-trace-logs">Checking the Trace Logs<a href="https://shisho.dev/docs/r/202609-takumi-runner-cicd-sensor-free-tier#checking-the-trace-logs" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
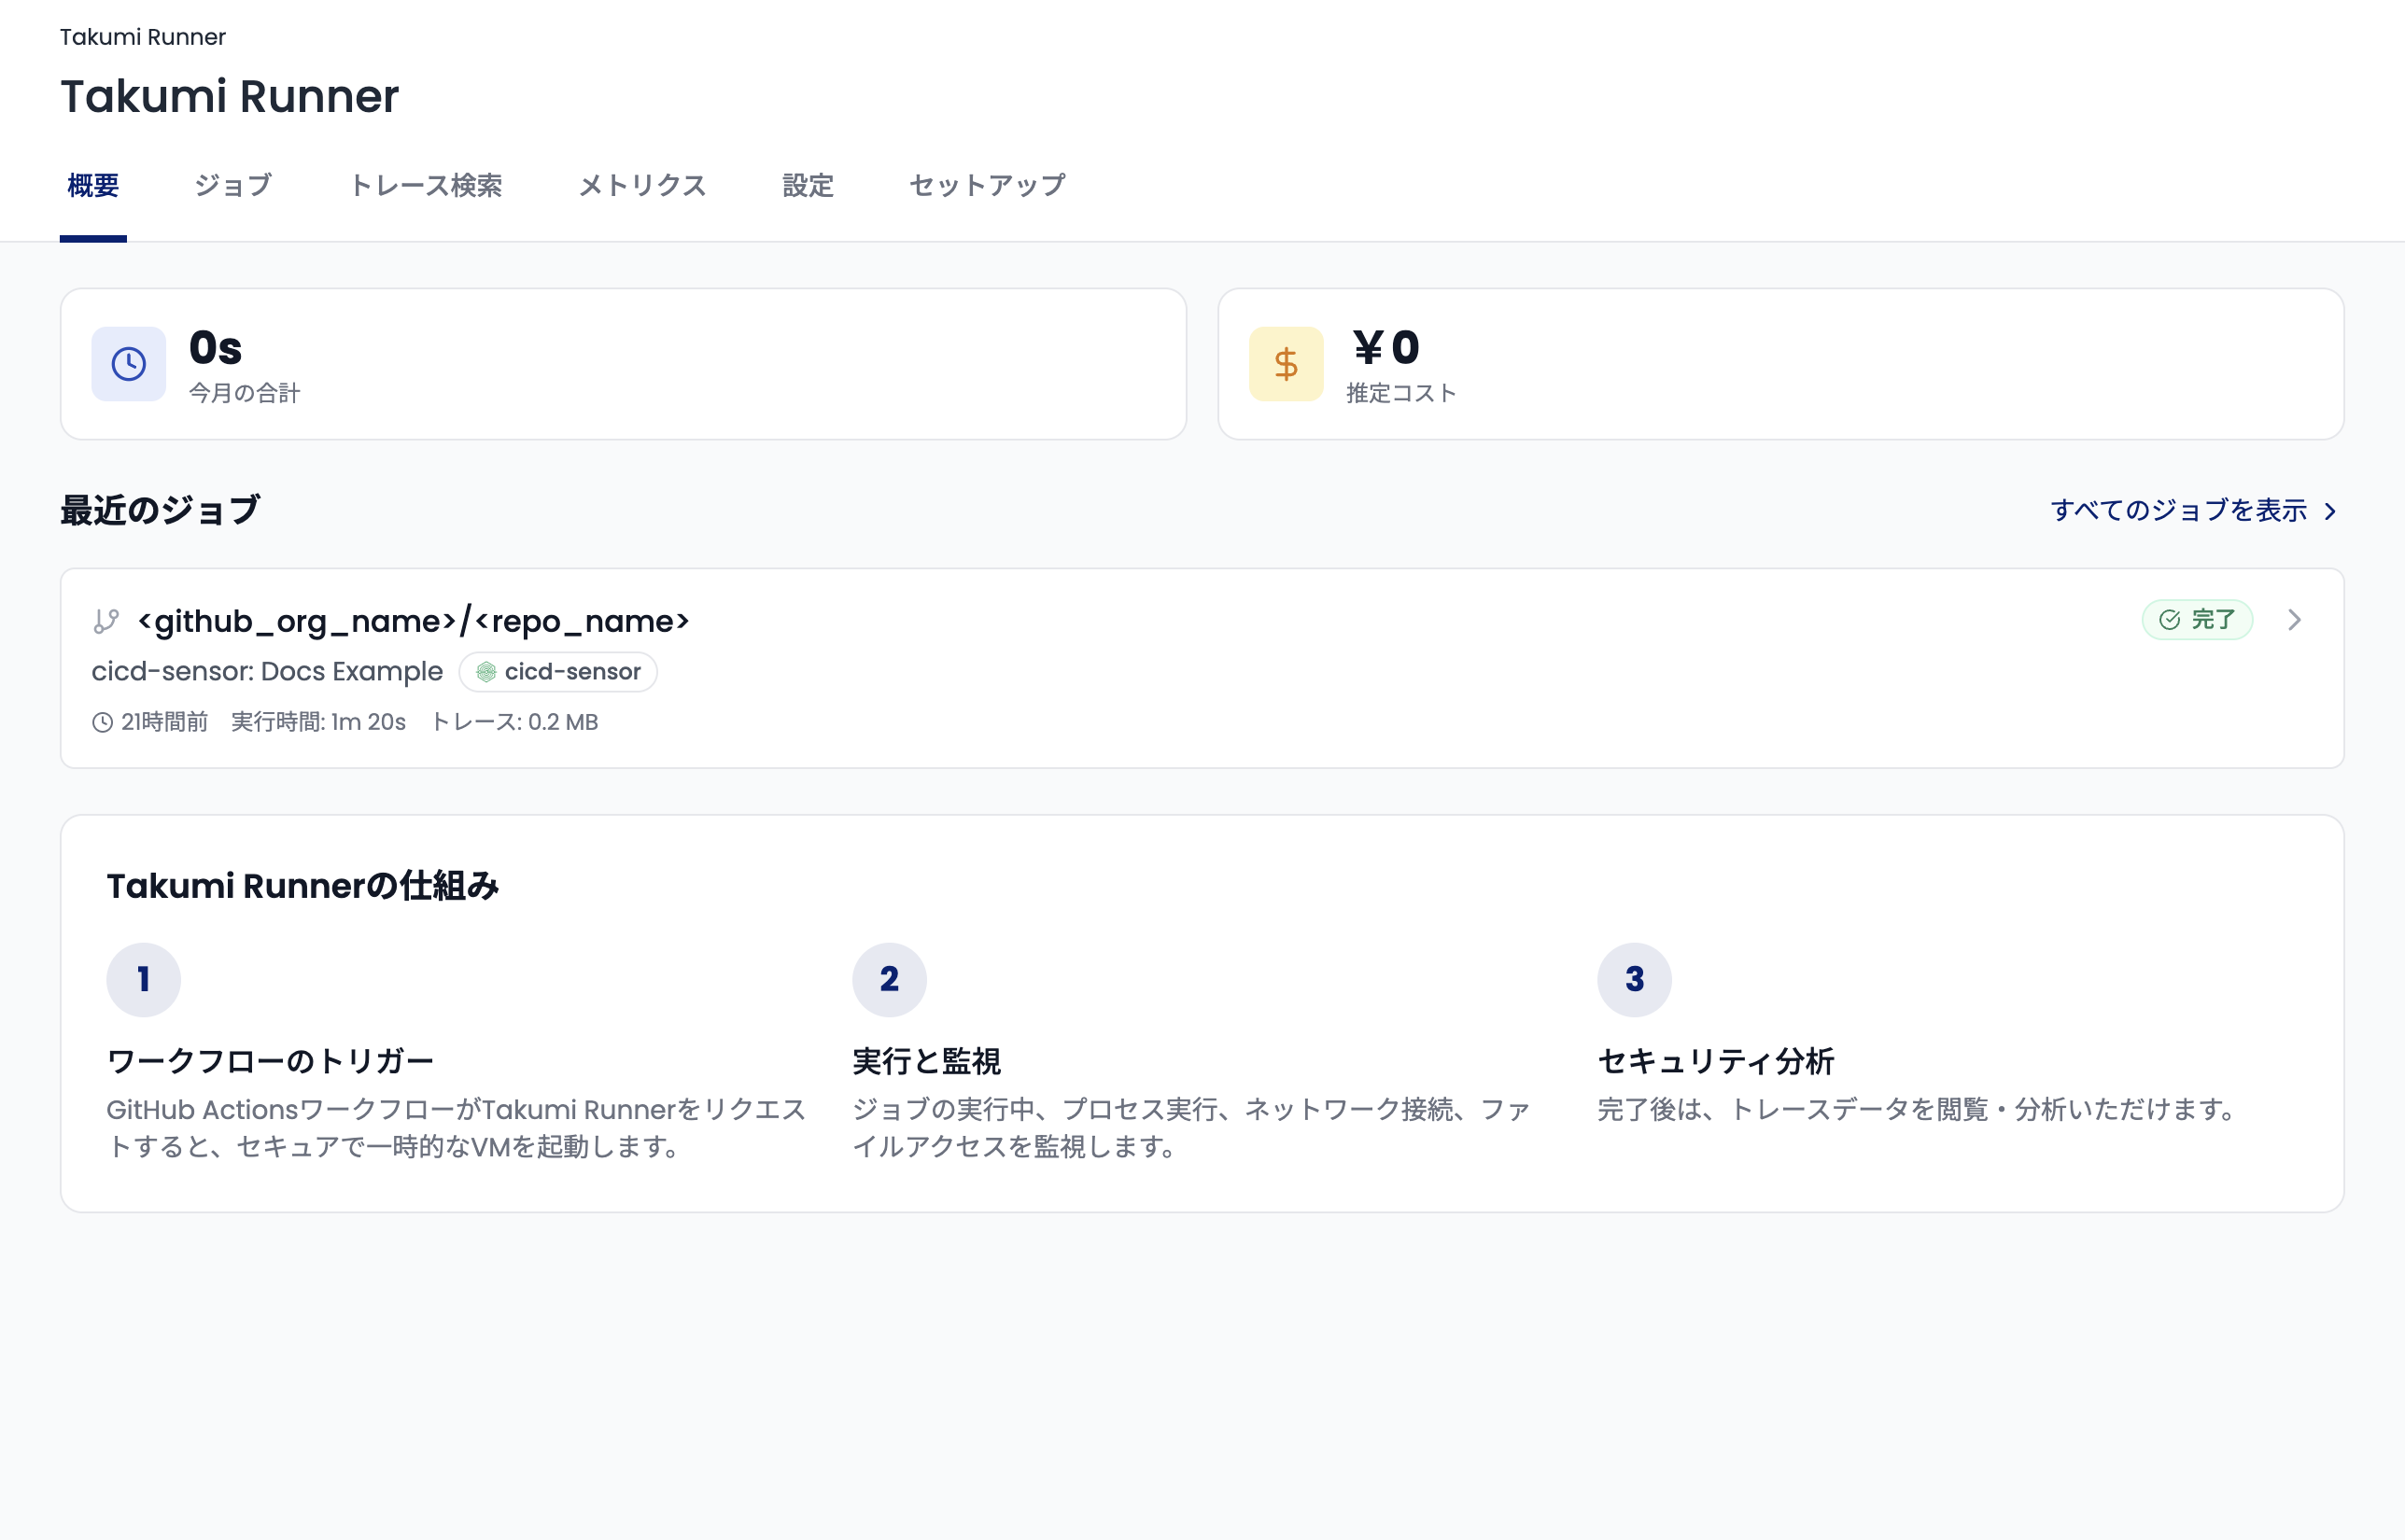
<p>Run the job above and the run becomes visible in the Takumi Runner console. Open <strong>Runner</strong> on the left side of the screen, and completed jobs appear under <strong>Recent Jobs</strong>.</p>
<p><img decoding="async" loading="lazy" alt="Takumi Runner overview screen" src="https://shisho.dev/docs/assets/images/overview-ffe824c5b196311ced139cd1de656499.png" width="2576" height="1650" class="img_aV4l"></p>
<p>Click a job to see its trace logs. From here, you can use the <a href="https://shisho.dev/docs/r/202609-takumi-runner-cicd-sensor-free-tier#features">various features</a> for working with trace logs introduced above.</p>
<p>For more details on the cicd-sensor integration, see the <a href="https://shisho.dev/docs/t/runner/features/cicdsensor-integration">user guide</a>.</p>]]></content>
        <author>
            <name>Rio Nishimori</name>
            <uri>https://github.com/rio828</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Seeking Alpha Testers for Takumi ASM]]></title>
        <id>https://shisho.dev/docs/r/202608-takumi-asm-alpha-testers</id>
        <link href="https://shisho.dev/docs/r/202608-takumi-asm-alpha-testers"/>
        <updated>2026-08-31T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[Join the free alpha test of Takumi's upcoming ASM capability and discover internet-facing assets associated with your domains.]]></summary>
        <content type="html"><![CDATA[<p>We are seeking alpha testers for the upcoming <strong>Attack Surface Management (ASM)</strong> capability in Takumi. The alpha test is free and focuses on discovering internet-facing assets associated with your domains from publicly available information.</p>
<p><img decoding="async" loading="lazy" alt="Takumi ASM alpha tester recruitment" src="https://shisho.dev/docs/assets/images/eyecatch-6265588c17853aabd783952b90e2f59c.png" width="2400" height="1260" class="img_aV4l"></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="what-the-alpha-test-does">What the Alpha Test Does<a href="https://shisho.dev/docs/r/202608-takumi-asm-alpha-testers#what-the-alpha-test-does" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>The initial alpha focuses on asset discovery. Takumi uses publicly available information and performs only minimal crawling of the assets it finds. It does not attempt logins, perform malicious actions, or run invasive tests against your applications.</p>
<p>For each ASM run, approximately two browser accesses per asset is the general guideline for the traffic sent. The execution frequency during the alpha test will vary depending on development and testing needs. To minimize the impact on target assets, ASM runs associated with any single organization will be limited to a maximum of five per hour.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="what-participants-receive">What Participants Receive<a href="https://shisho.dev/docs/r/202608-takumi-asm-alpha-testers#what-participants-receive" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>After the alpha test concludes, we plan to provide each participating organization, where possible, with a data-based list of the assets discovered for it. These results can help you identify shadow assets that were not previously known within your organization, update your inventory of internet-facing assets, and inform the scope and priorities of future vulnerability assessments and penetration tests.</p>
<p>Results will not initially be available in the Takumi user interface, and the alpha test does not guarantee comprehensive asset discovery.</p>
<p>Your participation and feedback will help improve how Takumi associates assets with their owners and prioritizes the assets that warrant closer review.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="future-plans">Future Plans<a href="https://shisho.dev/docs/r/202608-takumi-asm-alpha-testers#future-plans" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>We plan to extend ASM so that it can select discovered attack-surface assets for review with Takumi's penetration testing capability and, where appropriate, automatically assess those targets. The alpha test itself does not perform these penetration tests.</p>
<p>ASM is planned as a paid Takumi capability in the future.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="how-to-participate">How to Participate<a href="https://shisho.dev/docs/r/202608-takumi-asm-alpha-testers#how-to-participate" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>To join the free alpha test, contact your GMO Flatt Security sales representative or email <a href="mailto:shisho-support@flatt.tech" target="_blank" rel="noopener noreferrer">shisho-support@flatt.tech</a>.</p>
<p>You can use the following email template when applying:</p>
<div class="language-text codeBlockContainer_tXdS theme-code-block" style="--prism-color:#393A34;--prism-background-color:#f6f8fa"><div class="codeBlockContent_zXtR"><pre tabindex="0" class="prism-code language-text codeBlock_qqWd thin-scrollbar" style="color:#393A34;background-color:#f6f8fa"><code class="codeBlockLines_CmGJ"><span class="token-line" style="color:#393A34"><span class="token plain">Subject: Application for the Takumi ASM Alpha Test</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain" style="display:inline-block"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">I would like to apply to participate in the alpha test of Takumi's ASM capability.</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">Please use the following domains as starting points for asset discovery:</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain" style="display:inline-block"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">- aaa.example (known subdomain: xxx.aaa.example)</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">- bbb.example</span><br></span></code></pre><div class="buttonGroup_yRlK"><button type="button" aria-label="Copy code to clipboard" title="Copy" class="clean-btn"><span class="copyButtonIcons_yBV4" aria-hidden="true"><svg viewBox="0 0 24 24" class="copyButtonIcon_Ctry"><path fill="currentColor" d="M19,21H8V7H19M19,5H8A2,2 0 0,0 6,7V21A2,2 0 0,0 8,23H19A2,2 0 0,0 21,21V7A2,2 0 0,0 19,5M16,1H4A2,2 0 0,0 2,3V17H4V3H16V1Z"></path></svg><svg viewBox="0 0 24 24" class="copyButtonSuccessIcon_FUe1"><path fill="currentColor" d="M21,7L9,19L3.5,13.5L4.91,12.09L9,16.17L19.59,5.59L21,7Z"></path></svg></span></button></div></div></div>
<p>Please include a list of domains that your organization knows it owns. We will use these domains as starting points for asset discovery. You may share only what you are comfortable providing, but please include at least one domain. If you would be open to providing further assistance with product improvement, we would also appreciate a list of subdomains associated with those domains. This information will help us evaluate and improve discovery accuracy.</p>]]></content>
        <author>
            <name>Takashi Yoneuchi</name>
            <uri>https://github.com/lmt-swallow</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi Runner Now Supports Threat Detection]]></title>
        <id>https://shisho.dev/docs/r/202608-takumi-runner-threat-detection</id>
        <link href="https://shisho.dev/docs/r/202608-takumi-runner-threat-detection"/>
        <updated>2026-08-19T02:00:00.000Z</updated>
        <summary type="html"><![CDATA[When a supply-chain incident occurs, Takumi Runner proactively investigates the collected traces and notifies affected organizations.]]></summary>
        <content type="html"><![CDATA[<p>Takumi Runner now provides <strong>threat detection</strong>, which proactively detects threats in CI/CD pipelines. When a supply-chain incident occurs — like the ones Takumi Guard has reported on in the past — we promptly investigate the trace data collected through Takumi Runner or <a href="https://shisho.dev/docs/r/202608-takumi-runner-cicd-sensor-integration">cicd-sensor</a>, and immediately notify you when a threat is detected.</p>
<p><img decoding="async" loading="lazy" alt="Responding to a supply-chain incident: before vs. with threat detection" src="data:image/svg+xml;base64,PHN2ZyB4bWxucz0iaHR0cDovL3d3dy53My5vcmcvMjAwMC9zdmciIHhtbG5zOnhsaW5rPSJodHRwOi8vd3d3LnczLm9yZy8xOTk5L3hsaW5rIiB3aWR0aD0iMTYwMCIgaGVpZ2h0PSI4MzgiIHZpZXdCb3g9IjAgMCAxNjAwIDgzOCIgcm9sZT0iaW1nIiBmb250LWZhbWlseT0iJ0hpcmFnaW5vIEtha3UgR290aGljIFByb04nLCAnSGlyYWdpbm8gU2FucycsICdZdSBHb3RoaWMnLCBNZWlyeW8sICdOb3RvIFNhbnMgSlAnLCBzYW5zLXNlcmlmIj4KICA8dGl0bGU+UmVzcG9uZGluZyB0byBhIHN1cHBseS1jaGFpbiBpbmNpZGVudDogYmVmb3JlIHZzLiB3aXRoIHRocmVhdCBkZXRlY3Rpb248L3RpdGxlPgogIDxkZWZzPgogICAgPCEtLSB0aGljayBibG9jayBhcnJvdywgNjQgd2lkZSB4IDQ0IHRhbGwsIHBvaW50aW5nIHJpZ2h0OyBmaWxsIHNldCBwZXIgdXNlIC0tPgogICAgPHBvbHlnb24gaWQ9ImJsb2NrLWFycm93IiBwb2ludHM9IjAsLTExIDM4LC0xMSAzOCwtMjIgNjQsMCAzOCwyMiAzOCwxMSAwLDExIi8+CiAgICA8IS0tIGNsaXBib2FyZCBpY29uICg5MCB4IDExNiwgdG9wLWxlZnQgYXQgMCwwKTsgZnJhbWUgY29sb3IgPSBjdXJyZW50Q29sb3I7IGNoZWNrIG1hcmtzIGRyYXduIHNlcGFyYXRlbHkgLS0+CiAgICA8ZyBpZD0iY2xpcGJvYXJkIiBmaWxsPSJub25lIiBzdHJva2U9ImN1cnJlbnRDb2xvciIgc3Ryb2tlLXdpZHRoPSI1IiBzdHJva2UtbGluZWNhcD0icm91bmQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiPgogICAgICA8cmVjdCB4PSIwIiB5PSI4IiB3aWR0aD0iOTAiIGhlaWdodD0iMTA4IiByeD0iOCIgZmlsbD0iI2ZmZmZmZiIvPgogICAgICA8cmVjdCB4PSIyNyIgeT0iMCIgd2lkdGg9IjM2IiBoZWlnaHQ9IjE4IiByeD0iNSIgZmlsbD0iY3VycmVudENvbG9yIiBzdHJva2U9Im5vbmUiLz4KICAgICAgPHBhdGggZD0iTTQ3IDQzIEg3NyBNNDcgNjcgSDc3IE00NyA5MSBINzciIHN0cm9rZS13aWR0aD0iNCIvPgogICAgPC9nPgogICAgPHBhdGggaWQ9ImNsaXBib2FyZC1jaGVja3MiIGQ9Ik0xNyA0MyBMMjUgNTEgTDM5IDM1IE0xNyA2NyBMMjUgNzUgTDM5IDU5IE0xNyA5MSBMMjUgOTkgTDM5IDgzIiBmaWxsPSJub25lIiBzdHJva2Utd2lkdGg9IjQuNSIgc3Ryb2tlLWxpbmVjYXA9InJvdW5kIiBzdHJva2UtbGluZWpvaW49InJvdW5kIi8+CiAgPC9kZWZzPgoKICA8cmVjdCB3aWR0aD0iMTYwMCIgaGVpZ2h0PSI4MzgiIGZpbGw9IiNmZmZmZmYiLz4KCiAgPCEtLSB0aXRsZSAtLT4KICA8dGV4dCB4PSI4MDAiIHk9IjcyIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjQyIiBmb250LXdlaWdodD0iYm9sZCIgZmlsbD0iIzI0MjkyZiI+UmVzcG9uZGluZyB0byBhIHN1cHBseS1jaGFpbiBpbmNpZGVudDwvdGV4dD4KCiAgPCEtLSA9PT09PT09PT09PT09PT09PT09PT0gcm93IDE6IGJlZm9yZSA9PT09PT09PT09PT09PT09PT09PT0gLS0+CiAgPHJlY3QgeD0iNDAiIHk9IjExOCIgd2lkdGg9IjE1MjAiIGhlaWdodD0iMzEzIiByeD0iMTgiIGZpbGw9IiNmNmY0ZjQiLz4KICA8cmVjdCB4PSI2MiIgeT0iMjcwIiB3aWR0aD0iMTUwIiBoZWlnaHQ9IjUwIiByeD0iMjUiIGZpbGw9IiM5YjZiNmIiLz4KICA8dGV4dCB4PSIxMzciIHk9IjMwNCIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIyNiIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiNmZmZmZmYiPkJlZm9yZTwvdGV4dD4KCiAgPCEtLSBzdGVwIDE6IGNoZWNrIGJsb2dzIC8gWCAoc21hcnRwaG9uZSBmZWVkLCBmaW5nZXIgdGFwcGluZyB0aGUgc2NyZWVuKSAtLT4KICA8dGV4dCB4PSI0MzAiIHk9IjE3NCIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIzNiIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiM1ZjVmNWYiPkNoZWNrIGJsb2dzICZhbXA7IFg8L3RleHQ+CiAgPGcgZmlsbD0ibm9uZSIgc3Ryb2tlPSIjOGE3YTdhIiBzdHJva2Utd2lkdGg9IjYiIHN0cm9rZS1saW5lY2FwPSJyb3VuZCIgc3Ryb2tlLWxpbmVqb2luPSJyb3VuZCI+CiAgICA8cmVjdCB4PSIzODQiIHk9IjIxNCIgd2lkdGg9IjkyIiBoZWlnaHQ9IjE2MSIgcng9IjE2IiBmaWxsPSIjZmZmZmZmIi8+CiAgICA8cGF0aCBkPSJNNDE2IDIzMCBINDQzIiBzdHJva2Utd2lkdGg9IjUiLz4KICAgIDxjaXJjbGUgY3g9IjQwNiIgY3k9IjI2MiIgcj0iOSIgZmlsbD0iI2M5YjhiOCIgc3Ryb2tlPSJub25lIi8+CiAgICA8cGF0aCBkPSJNNDIzIDI1NyBINDU3IE00MjMgMjcwIEg0NDggTTQwMyAyOTUgSDQ1NyBNNDAzIDMxMSBINDQ4IE00MDMgMzI3IEg0NTciIHN0cm9rZT0iI2M5YjhiOCIgc3Ryb2tlLXdpZHRoPSI1Ii8+CiAgICA8cGF0aCBkPSJNNDE2IDM1OSBINDQzIiBzdHJva2U9IiNjOWI4YjgiIHN0cm9rZS13aWR0aD0iNSIvPgogIDwvZz4KICA8ZyB0cmFuc2Zvcm09InRyYW5zbGF0ZSg0NjAgMjY0KSByb3RhdGUoLTMwKSBzY2FsZSgxLjEpIiBmaWxsPSJub25lIiBzdHJva2UtbGluZWNhcD0icm91bmQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiPgogICAgPHBhdGggZD0iTS0yMC44IC00IEEyNCAyNCAwIDAgMSAyMC44IC00IE0tMTQuNCAtMSBBMTcgMTcgMCAwIDEgMTQuNCAtMSIgc3Ryb2tlPSIjZDM3MDZjIiBzdHJva2Utd2lkdGg9IjMuNiIvPgogICAgPHBhdGggZD0iTS04IDggQTggOCAwIDAgMSA4IDggTDggMzYgQTQgNCAwIDAgMSAxNiAzNiBBNCA0IDAgMCAxIDI0IDM2IEE2IDYgMCAwIDEgMzAgNDIgTDMwIDYwIEExMCAxMCAwIDAgMSAyMCA3MCBMLTYgNzAgQTEwIDEwIDAgMCAxIC0xNiA2MCBMLTE2IDQ2IFEtMTYgNDAgLTggNDAgWiIgZmlsbD0iI2ZmZmZmZiIgc3Ryb2tlPSIjOGE3YTdhIiBzdHJva2Utd2lkdGg9IjQuNSIvPgogIDwvZz4KICA8ZWxsaXBzZSBjeD0iNTEwIiBjeT0iMzgxIiByeD0iMTEyIiByeT0iMjYiIGZpbGw9IiNmZmZmZmYiIHN0cm9rZT0iI2QzNzA2YyIgc3Ryb2tlLXdpZHRoPSIzIi8+CiAgPHRleHQgeD0iNTEwIiB5PSIzODgiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMjAiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjZDM3MDZjIj5NaWdodCBtaXNzIGl04oCmPC90ZXh0PgoKICA8dXNlIHhsaW5rOmhyZWY9IiNibG9jay1hcnJvdyIgeD0iNjI4IiB5PSIyOTUiIGZpbGw9IiNiOGE5YTkiLz4KCiAgPCEtLSBzdGVwIDI6IHNlYXJjaCB0aGUgbG9ncyB5b3Vyc2VsZiAoc3RhY2sgb2YgbG9nIHBhZ2VzICsgbWFnbmlmaWVyKSAtLT4KICA8dGV4dCB4PSI4OTAiIHk9IjE3NCIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIzNiIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiM1ZjVmNWYiPlNlYXJjaCBsb2dzIHlvdXJzZWxmPC90ZXh0PgogIDxnIGZpbGw9Im5vbmUiIHN0cm9rZT0iIzlhODY4NiIgc3Ryb2tlLXdpZHRoPSI2IiBzdHJva2UtbGluZWNhcD0icm91bmQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiPgogICAgPHJlY3QgeD0iODM2IiB5PSIyMTQiIHdpZHRoPSIxMjEiIGhlaWdodD0iMTQ4IiByeD0iOCIgZmlsbD0iI2Y0ZWRlZCIgc3Ryb2tlPSIjYjM5YzljIi8+CiAgICA8cmVjdCB4PSI4MjMiIHk9IjIyNyIgd2lkdGg9IjEyMSIgaGVpZ2h0PSIxNDgiIHJ4PSI4IiBmaWxsPSIjZmZmZmZmIi8+CiAgICA8cGF0aCBkPSJNODQyIDI1NCBIOTI1IE04NDIgMjc0IEg5MDkgTTg0MiAyOTQgSDkyOCBNODQyIDMxNCBIOTAxIE04NDIgMzM1IEg5MjMgTTg0MiAzNTUgSDkxMiIgc3Ryb2tlPSIjYjM5YzljIiBzdHJva2Utd2lkdGg9IjUiLz4KICA8L2c+CiAgPGNpcmNsZSBjeD0iOTUwIiBjeT0iMjY3IiByPSIzNSIgZmlsbD0iI2ZmZmZmZiIgZmlsbC1vcGFjaXR5PSIwLjUiIHN0cm9rZT0iI2QzNzA2YyIgc3Ryb2tlLXdpZHRoPSI4Ii8+CiAgPHBhdGggZD0iTTk3NSAyOTIgTDEwMDYgMzIzIiBzdHJva2U9IiNkMzcwNmMiIHN0cm9rZS13aWR0aD0iMTIiIHN0cm9rZS1saW5lY2FwPSJyb3VuZCIvPgogIDxlbGxpcHNlIGN4PSI5NzAiIGN5PSIzODEiIHJ4PSIxMDAiIHJ5PSIyNiIgZmlsbD0iI2ZmZmZmZiIgc3Ryb2tlPSIjZDM3MDZjIiBzdHJva2Utd2lkdGg9IjMiLz4KICA8dGV4dCB4PSI5NzAiIHk9IjM4OCIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIyMCIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiNkMzcwNmMiPlN1Y2ggYSBoYXNzbGXigKY8L3RleHQ+CgogIDx1c2UgeGxpbms6aHJlZj0iI2Jsb2NrLWFycm93IiB4PSIxMDg4IiB5PSIyOTUiIGZpbGw9IiNiOGE5YTkiLz4KCiAgPCEtLSBzdGVwIDM6IHBvc3QtaW5jaWRlbnQgcmVzcG9uc2UgKGNsaXBib2FyZCkgLS0+CiAgPHRleHQgeD0iMTM1MCIgeT0iMTc0IiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjM2IiBmb250LXdlaWdodD0iYm9sZCIgZmlsbD0iIzVmNWY1ZiI+UmVzcG9uZDwvdGV4dD4KICA8dXNlIHhsaW5rOmhyZWY9IiNjbGlwYm9hcmQiIHRyYW5zZm9ybT0idHJhbnNsYXRlKDEyOTAgMjE0KSBzY2FsZSgxLjM0NCkiIGNvbG9yPSIjOGE3YTdhIi8+CiAgPHVzZSB4bGluazpocmVmPSIjY2xpcGJvYXJkLWNoZWNrcyIgdHJhbnNmb3JtPSJ0cmFuc2xhdGUoMTI5MCAyMTQpIHNjYWxlKDEuMzQ0KSIgc3Ryb2tlPSIjYTA5MDkwIi8+CiAgPHRleHQgeD0iMTM1MCIgeT0iNDAyIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjIyIiBmaWxsPSIjN2E3YTdhIj4oaWYgYWZmZWN0ZWQpPC90ZXh0PgoKICA8IS0tID09PT09PT09PT09PT09PT09PT09PSByb3cgMjogd2l0aCB0aHJlYXQgZGV0ZWN0aW9uID09PT09PT09PT09PT09PT09PT09PSAtLT4KICA8cmVjdCB4PSI0MCIgeT0iNDcxIiB3aWR0aD0iMTUyMCIgaGVpZ2h0PSIzMjciIHJ4PSIxOCIgZmlsbD0iI2VlZjRmYyIvPgogIDxyZWN0IHg9IjYyIiB5PSI2MjkiIHdpZHRoPSIyNjAiIGhlaWdodD0iNTAiIHJ4PSIyNSIgZmlsbD0iIzJmNmZkNiIvPgogIDx0ZXh0IHg9IjE5MiIgeT0iNjYzIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjI2IiBmb250LXdlaWdodD0iYm9sZCIgZmlsbD0iI2ZmZmZmZiI+VGhyZWF0IGRldGVjdGlvbjwvdGV4dD4KCiAgPCEtLSBzdGVwOiBSdW5uZXIgZG9lcyBpdCBhdXRvbWF0aWNhbGx5IChzaGllbGQgd2l0aCByYWRhciBzd2VlcCwgYmVsbCBhdHRhY2hlZCkg4oCUIHJlcGxhY2VzIHN0ZXBzIDEgYW5kIDIgLS0+CiAgPHRleHQgeD0iNjYwIiB5PSI1MjciIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMzYiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjNWY1ZjVmIj5SdW5uZXIgaGFuZGxlcyBpdCBmb3IgeW91PC90ZXh0PgogIDxnIHRyYW5zZm9ybT0idHJhbnNsYXRlKDY2MCA2NTQpIHNjYWxlKDEuNCkiPgogICAgPHBhdGggZD0iTTAgLTYyIEMyMiAtNTAgNDIgLTQ0IDU2IC00NCBDNTYgLTIgNDAgMzQgMCA2MiBDLTQwIDM0IC01NiAtMiAtNTYgLTQ0IEMtNDIgLTQ0IC0yMiAtNTAgMCAtNjIgWiIgZmlsbD0iI2VhZjNmZiIgc3Ryb2tlPSIjMmY2ZmQ2IiBzdHJva2Utd2lkdGg9IjQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiLz4KICAgIDxjaXJjbGUgY3g9IjAiIGN5PSItNiIgcj0iMzIiIGZpbGw9IiNmZmZmZmYiIHN0cm9rZT0iIzJmNmZkNiIgc3Ryb2tlLXdpZHRoPSIyLjUiLz4KICAgIDxjaXJjbGUgY3g9IjAiIGN5PSItNiIgcj0iMTgiIGZpbGw9Im5vbmUiIHN0cm9rZT0iIzlmYzBlYSIgc3Ryb2tlLXdpZHRoPSIxLjUiLz4KICAgIDxwYXRoIGQ9Ik0tMzIgLTYgSDMyIE0wIC0zOCBWMjYiIHN0cm9rZT0iIzlmYzBlYSIgc3Ryb2tlLXdpZHRoPSIxLjUiLz4KICAgIDxwYXRoIGQ9Ik0wIC02IEwwIC0zOCBBMzIgMzIgMCAwIDEgMjcuNyAtMjIgWiIgZmlsbD0iIzJmNmZkNiIgZmlsbC1vcGFjaXR5PSIwLjMiLz4KICAgIDxwYXRoIGQ9Ik0wIC02IEwyNy43IC0yMiIgc3Ryb2tlPSIjMmY2ZmQ2IiBzdHJva2Utd2lkdGg9IjIuNSIgc3Ryb2tlLWxpbmVjYXA9InJvdW5kIi8+CiAgICA8Y2lyY2xlIGN4PSIxMiIgY3k9Ii0yNCIgcj0iNC41IiBmaWxsPSIjMmZhMzZiIi8+CiAgPC9nPgogIDxnIHRyYW5zZm9ybT0idHJhbnNsYXRlKDc0MiA2MDcpIHNjYWxlKDEuMDUpIj4KICAgIDxwYXRoIGQ9Ik0tMjQgMTYgQy0yNCAtMTQgLTE0IC0yOCAwIC0zMCBDMTQgLTI4IDI0IC0xNCAyNCAxNiBMMzAgMjQgSC0zMCBaIiBmaWxsPSIjZmZmZmZmIiBzdHJva2U9IiMyZjZmZDYiIHN0cm9rZS13aWR0aD0iNC41IiBzdHJva2UtbGluZWpvaW49InJvdW5kIi8+CiAgICA8Y2lyY2xlIGN4PSIwIiBjeT0iMzIiIHI9IjYiIGZpbGw9IiMyZjZmZDYiLz4KICAgIDxjaXJjbGUgY3g9IjAiIGN5PSItMzQiIHI9IjQiIGZpbGw9IiMyZjZmZDYiLz4KICAgIDxjaXJjbGUgY3g9IjI2IiBjeT0iLTI0IiByPSIxMyIgZmlsbD0iIzJmYTM2YiIgc3Ryb2tlPSIjZmZmZmZmIiBzdHJva2Utd2lkdGg9IjMiLz4KICAgIDx0ZXh0IHg9IjI2IiB5PSItMTciIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTgiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjZmZmZmZmIj4hPC90ZXh0PgogIDwvZz4KICA8ZWxsaXBzZSBjeD0iNzUwIiBjeT0iNzQ3IiByeD0iMTcwIiByeT0iMjciIGZpbGw9IiNmZmZmZmYiIHN0cm9rZT0iIzJjOGE1OCIgc3Ryb2tlLXdpZHRoPSIzIi8+CiAgPHRleHQgeD0iNzUwIiB5PSI3NTQiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMjAiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjMmM4YTU4Ij5Zb3UgZ2V0IG5vdGlmaWVkIGlmIGFmZmVjdGVkPC90ZXh0PgoKICA8dXNlIHhsaW5rOmhyZWY9IiNibG9jay1hcnJvdyIgeD0iMTA4OCIgeT0iNjU0IiBmaWxsPSIjMmY2ZmQ2Ii8+CgogIDwhLS0gcG9zdC1pbmNpZGVudCByZXNwb25zZSAoYWZ0ZXIpOiBzYW1lIGljb24sIHNhbWUgY29sdW1uIGFzIGFib3ZlIC0tPgogIDx0ZXh0IHg9IjEzNTAiIHk9IjUyNyIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIzNiIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiM1ZjVmNWYiPlJlc3BvbmQ8L3RleHQ+CiAgPHVzZSB4bGluazpocmVmPSIjY2xpcGJvYXJkIiB0cmFuc2Zvcm09InRyYW5zbGF0ZSgxMjkwIDU3Nikgc2NhbGUoMS4zNDQpIiBjb2xvcj0iIzJmNmZkNiIvPgogIDx1c2UgeGxpbms6aHJlZj0iI2NsaXBib2FyZC1jaGVja3MiIHRyYW5zZm9ybT0idHJhbnNsYXRlKDEyOTAgNTc2KSBzY2FsZSgxLjM0NCkiIHN0cm9rZT0iIzJmYTM2YiIvPgo8L3N2Zz4K" width="1600" height="838" class="img_aV4l"></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="benefits">Benefits<a href="https://shisho.dev/docs/r/202608-takumi-runner-threat-detection#benefits" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Until now, you had to review and investigate the trace logs collected by Takumi Runner yourself. Investigating them effectively requires a certain amount of expertise, and the response needs to be fast.</p>
<p>With this feature, when a supply-chain incident occurs, an impact investigation that leverages our know-how and systems is carried out promptly, and you are notified if you are affected.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202608-takumi-runner-threat-detection#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
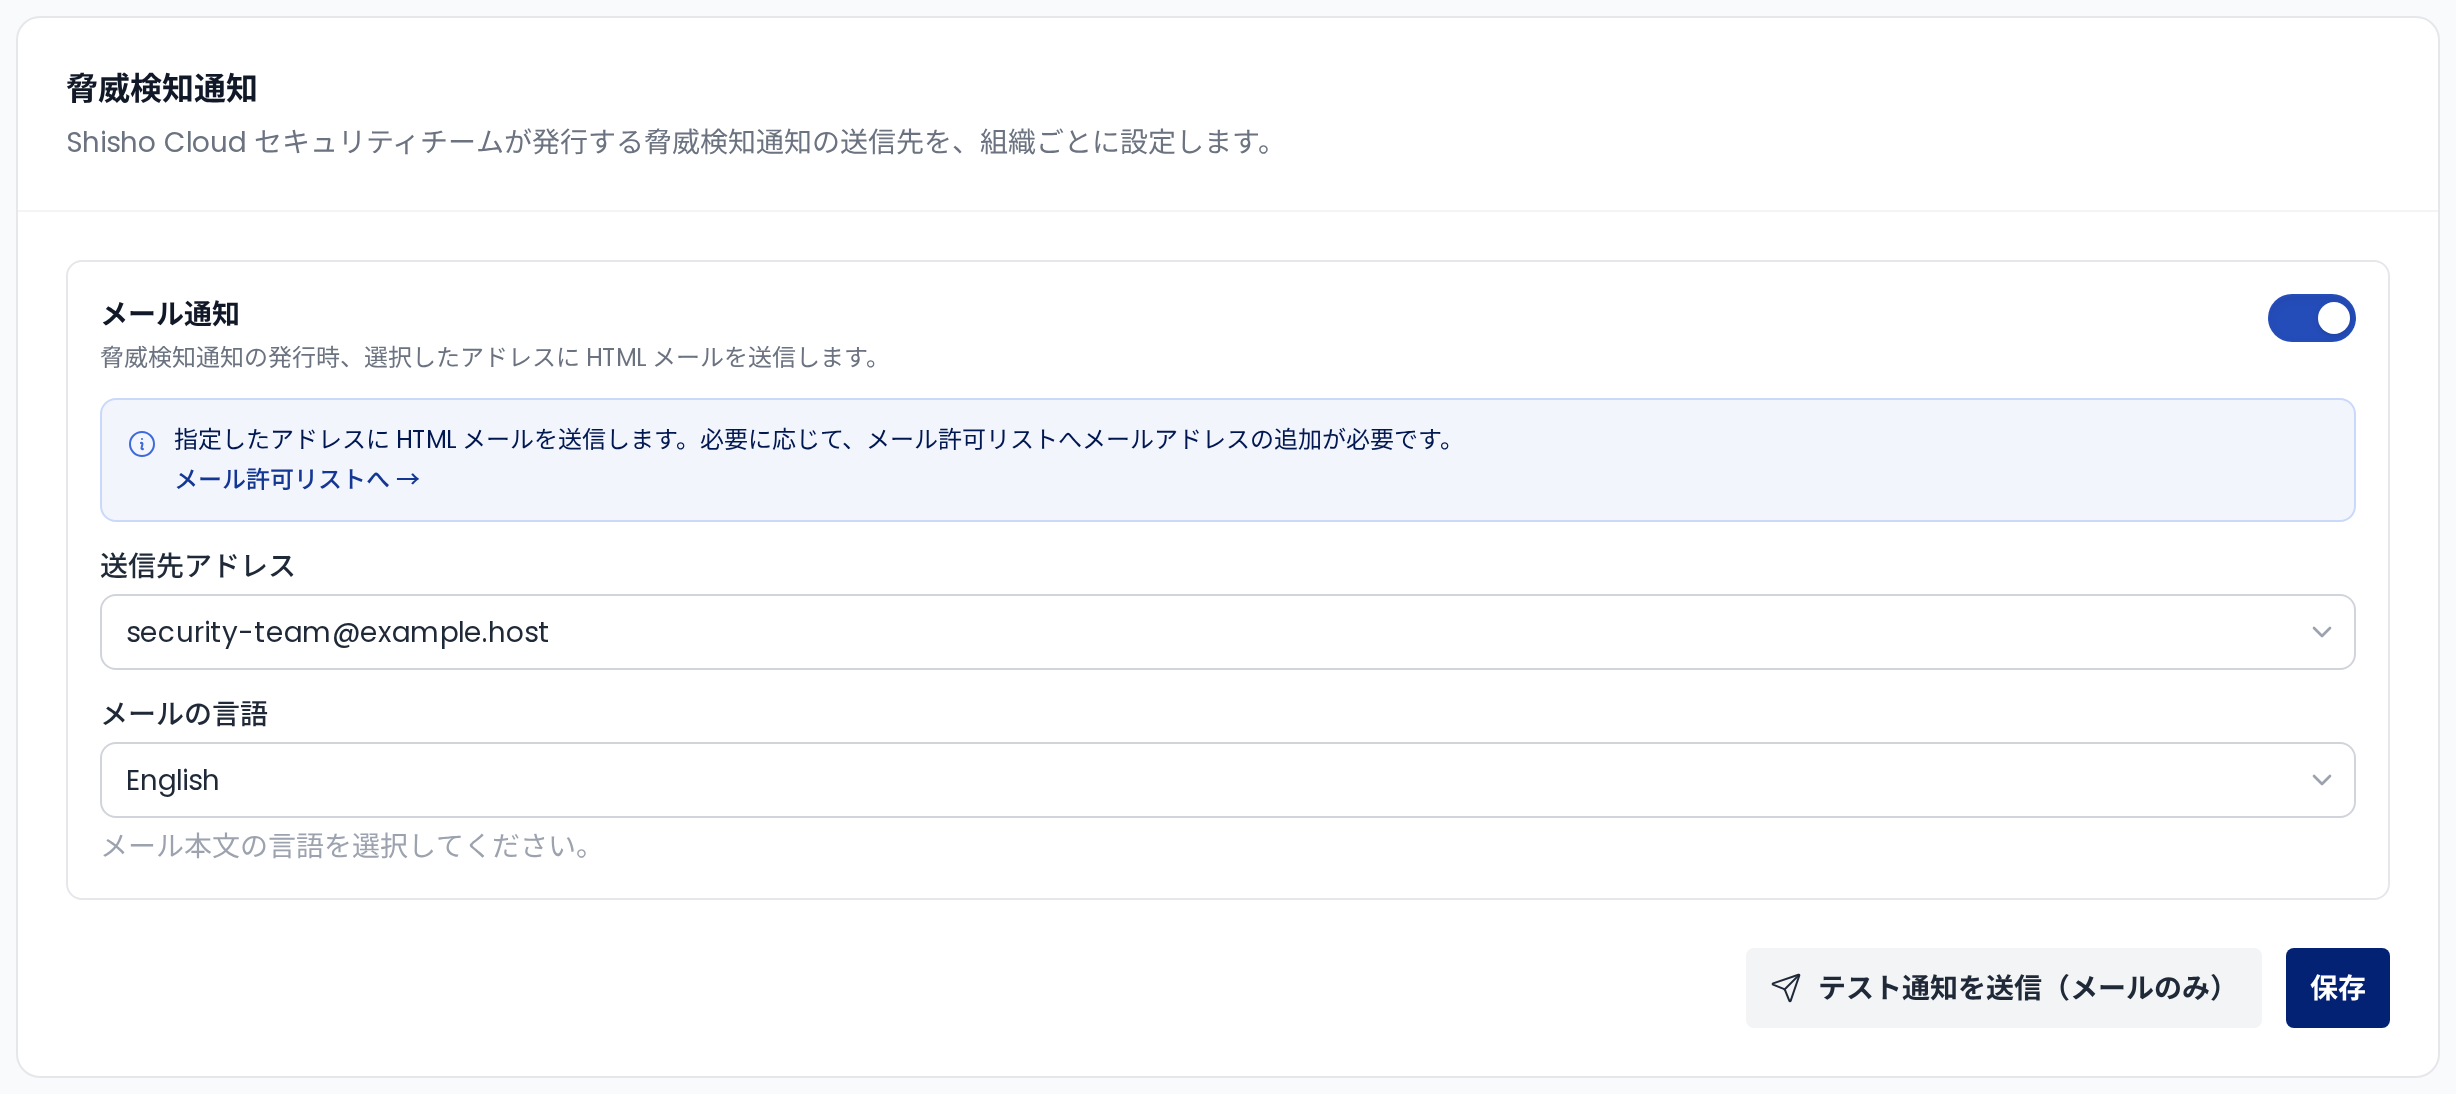
<p>To receive notifications, you need to enable <strong>threat notifications</strong> in the settings.</p>
<p>In the Shisho Cloud console, open <strong>Runner</strong> &gt; <strong>Settings</strong> and configure the destination under <strong>Threat Notifications</strong>.</p>
<p><img decoding="async" loading="lazy" alt="Threat notification settings" src="https://shisho.dev/docs/assets/images/notification-setup-email-8e0b1d2c5c0c5535ec6e6bd7871b4d2b.png" width="2456" height="1094" class="img_aV4l"></p>
<p>Turn on the <strong>Email notifications</strong> toggle and choose the destination address from <strong>Target address</strong>. Press "Save" and the setup is complete: notifications will be sent when a threat is detected in a future incident.</p>
<p>You can also send a test from this screen to confirm in advance that notifications arrive correctly.</p>
<div class="theme-admonition theme-admonition-info admonition_ODxW alert alert--info"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 14 16"><path fill-rule="evenodd" d="M7 2.3c3.14 0 5.7 2.56 5.7 5.7s-2.56 5.7-5.7 5.7A5.71 5.71 0 0 1 1.3 8c0-3.14 2.56-5.7 5.7-5.7zM7 1C3.14 1 0 4.14 0 8s3.14 7 7 7 7-3.14 7-7-3.14-7-7-7zm1 3H6v5h2V4zm0 6H6v2h2v-2z"></path></svg></span>info</div><div class="admonitionContent_Kqb4"><p>As of this writing, notifications are supported via email only. Webhook support is planned.</p></div></div>
<p>For details, see the <a href="https://shisho.dev/docs/t/runner/features/threat-detection">Threat Detection user guide</a>.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="pricing">Pricing<a href="https://shisho.dev/docs/r/202608-takumi-runner-threat-detection#pricing" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Threat detection is included in the Takumi Runner base plan. It is not metered.</p>
<p>For details on Takumi Runner plans, see <a href="https://shisho.dev/docs/t/runner/billing">Pricing &amp; Billing</a>.</p>
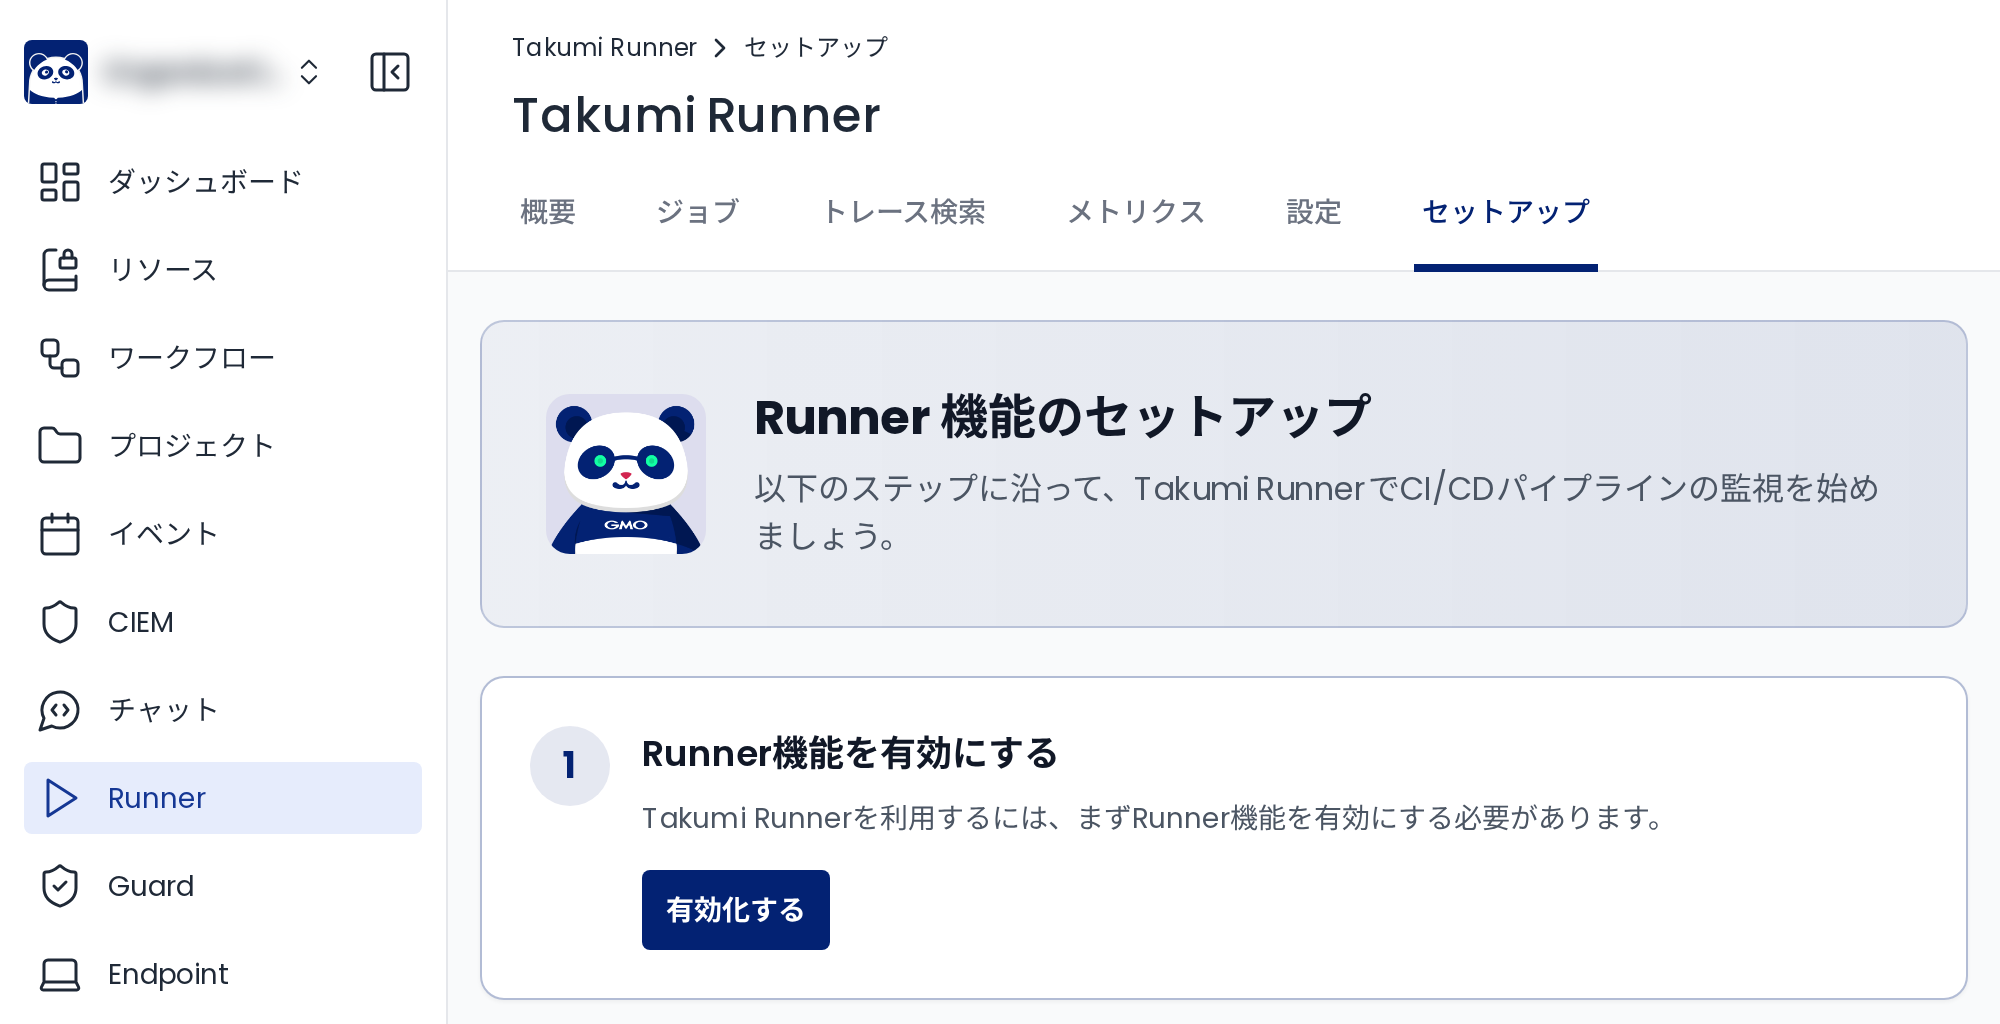
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started-with-takumi-runner">Getting Started with Takumi Runner<a href="https://shisho.dev/docs/r/202608-takumi-runner-threat-detection#getting-started-with-takumi-runner" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>To use Takumi Runner, you need a Takumi subscription and Runner enabled.</p>
<ol>
<li>Go to <a href="https://cloud.shisho.dev/hello/takumi" target="_blank" rel="noopener noreferrer">https://cloud.shisho.dev/hello/takumi</a> and sign in</li>
<li>Register your organization and subscribe to Takumi</li>
<li>Open <strong>Runner</strong> &gt; <strong>Settings</strong> from the sidebar on the left</li>
<li>Click the "Enable" button to enable Runner</li>
</ol>
<p><img decoding="async" loading="lazy" alt="Runner setup screen" src="https://shisho.dev/docs/assets/images/ui-runner-settings-e3e300eb20582fa02ccf7a0928c39553.png" width="2000" height="1024" class="img_aV4l"></p>
<p>Once Runner is enabled, follow the <a href="https://shisho.dev/docs/t/runner/quickstart">Takumi Runner user guide</a> to complete the setup.</p>]]></content>
        <author>
            <name>Rio Nishimori</name>
            <uri>https://github.com/rio828</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi Runner Now Integrates with cicd-sensor]]></title>
        <id>https://shisho.dev/docs/r/202608-takumi-runner-cicd-sensor-integration</id>
        <link href="https://shisho.dev/docs/r/202608-takumi-runner-cicd-sensor-integration"/>
        <updated>2026-08-19T01:00:00.000Z</updated>
        <summary type="html"><![CDATA[You can now send traces from CI/CD jobs running on GitHub-hosted runners, GitLab CI/CD, and other environments to Takumi and manage them in Takumi.]]></summary>
        <content type="html"><![CDATA[<p>Takumi Runner now integrates with <a href="https://github.com/cicd-sensor/cicd-sensor" target="_blank" rel="noopener noreferrer">cicd-sensor</a>, an open-source eBPF runtime security sensor. You can now <strong>collect trace logs from CI/CD jobs that run outside Takumi Hosted Runner</strong>, such as on GitHub-hosted runners and GitLab CI/CD, and manage them in Takumi Runner.</p>
<p><img decoding="async" loading="lazy" alt="Comparison of the Takumi Runner and cicd-sensor setups" src="data:image/svg+xml;base64,PHN2ZyB4bWxucz0iaHR0cDovL3d3dy53My5vcmcvMjAwMC9zdmciIHdpZHRoPSIxMjY2IiBoZWlnaHQ9IjM5NSIgdmlld0JveD0iMCAwIDEyNjYgMzk1IiBmb250LWZhbWlseT0iJ0hpcmFnaW5vIEtha3UgR290aGljIFByb04nLCAnSGlyYWdpbm8gU2FucycsICdZdSBHb3RoaWMnLCBNZWlyeW8sICdOb3RvIFNhbnMgSlAnLCBzYW5zLXNlcmlmIj4KICA8ZGVmcz4KICAgIDxtYXJrZXIgaWQ9ImFycm93IiB2aWV3Qm94PSIwIDAgMTAgMTAiIHJlZlg9IjkiIHJlZlk9IjUiIG1hcmtlcldpZHRoPSI3IiBtYXJrZXJIZWlnaHQ9IjciIG9yaWVudD0iYXV0by1zdGFydC1yZXZlcnNlIj4KICAgICAgPHBhdGggZD0iTSAwIDAgTCAxMCA1IEwgMCAxMCB6IiBmaWxsPSIjMjQyOTJmIi8+CiAgICA8L21hcmtlcj4KICA8L2RlZnM+CiAgPHJlY3Qgd2lkdGg9IjEyNjYiIGhlaWdodD0iMzk1IiBmaWxsPSIjZmZmZmZmIi8+CgogIDwhLS0gY29sdW1uLWdyb3VwIGhlYWRlcnMgLS0+CiAgPHRleHQgeD0iMzA0IiB5PSI0OCIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIyNiIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiMyNDI5MmYiPkdpdEh1YjwvdGV4dD4KICA8dGV4dCB4PSI5NjIiIHk9IjQ4IiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjI2IiBmb250LXdlaWdodD0iYm9sZCIgZmlsbD0iIzI0MjkyZiI+VGFrdW1pIFJ1bm5lcjwvdGV4dD4KCiAgPCEtLSByb3cgMSBsYWJlbCAtLT4KICA8dGV4dCB4PSIzMCIgeT0iNzEiIGZvbnQtc2l6ZT0iMTQiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjNTc2MDZhIj5Vc2luZyBUYWt1bWkgSG9zdGVkIFJ1bm5lcjwvdGV4dD4KCiAgPCEtLSByb3cgMTogd29ya2Zsb3cgWUFNTCAoZG9jdW1lbnQpIC0tPgogIDxwYXRoIGQ9Ik0gMTIwIDEwOCBMIDE5MyAxMDggTCAyMDUgMTIwIEwgMjA1IDE2MyBMIDEyMCAxNjMgWiIgZmlsbD0iI2ZmZmZmZiIgc3Ryb2tlPSIjNmU3NzgxIiBzdHJva2Utd2lkdGg9IjEuNSIgc3Ryb2tlLWxpbmVqb2luPSJyb3VuZCIvPgogIDxwYXRoIGQ9Ik0gMTkzIDEwOCBMIDE5MyAxMjAgTCAyMDUgMTIwIFoiIGZpbGw9IiNlMWU3ZWQiIHN0cm9rZT0iIzZlNzc4MSIgc3Ryb2tlLXdpZHRoPSIxLjIiIHN0cm9rZS1saW5lam9pbj0icm91bmQiLz4KICA8bGluZSB4MT0iMTMyIiB5MT0iMTI2IiB4Mj0iMTc2IiB5Mj0iMTI2IiBzdHJva2U9IiNkMGQ3ZGUiIHN0cm9rZS13aWR0aD0iMiIvPgogIDxsaW5lIHgxPSIxMzIiIHkxPSIxMzYiIHgyPSIxNjAiIHkyPSIxMzYiIHN0cm9rZT0iI2QwZDdkZSIgc3Ryb2tlLXdpZHRoPSIyIi8+CiAgPHRleHQgeD0iMTYyIiB5PSIxODMiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTYiIGZpbGw9IiMyNDI5MmYiPldvcmtmbG93IFlBTUw8L3RleHQ+CiAgPGxpbmUgeDE9IjIwNSIgeTE9IjEzNSIgeDI9IjczMSIgeTI9IjEzNSIgc3Ryb2tlPSIjMjQyOTJmIiBzdHJva2Utd2lkdGg9IjIiIG1hcmtlci1lbmQ9InVybCgjYXJyb3cpIi8+CiAgPHRleHQgeD0iNDY4IiB5PSIxMjIiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTMiIGZpbGw9IiMyNDI5MmYiPlJ1bjwvdGV4dD4KCiAgPCEtLSByb3cgMTogVGFrdW1pIEhvc3RlZCBSdW5uZXIgLS0+CiAgPHJlY3QgeD0iNzM1IiB5PSI4MCIgd2lkdGg9IjE3MCIgaGVpZ2h0PSIxMTAiIHJ4PSIxMCIgZmlsbD0iI2Y2ZjhmYSIgc3Ryb2tlPSIjNmU3NzgxIiBzdHJva2Utd2lkdGg9IjEuNSIvPgogIDx0ZXh0IHg9IjgyMCIgeT0iMTMwIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjE2IiBmaWxsPSIjMjQyOTJmIj5UYWt1bWk8L3RleHQ+CiAgPHRleHQgeD0iODIwIiB5PSIxNTIiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTYiIGZpbGw9IiMyNDI5MmYiPkhvc3RlZCBSdW5uZXI8L3RleHQ+CiAgPGxpbmUgeDE9IjkwNSIgeTE9IjEzNSIgeDI9IjEwMjQiIHkyPSIxMzUiIHN0cm9rZT0iIzI0MjkyZiIgc3Ryb2tlLXdpZHRoPSIyIiBtYXJrZXItZW5kPSJ1cmwoI2Fycm93KSIvPgogIDx0ZXh0IHg9Ijk2NSIgeT0iMTIyIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjEzIiBmaWxsPSIjMjQyOTJmIj5UcmFjZSBsb2dzPC90ZXh0PgoKICA8IS0tIHJvdyAxOiBUYWt1bWkgUnVubmVyIChjbG91ZCkgLS0+CiAgPGVsbGlwc2UgY3g9IjExMDQiIGN5PSIxNjkiIHJ4PSI3NiIgcnk9IjE5IiBmaWxsPSIjZGJlYWZlIi8+CiAgPGNpcmNsZSBjeD0iMTA1NyIgY3k9IjE0NSIgcj0iMjkiIGZpbGw9IiNkYmVhZmUiLz4KICA8Y2lyY2xlIGN4PSIxMTA0IiBjeT0iMTI3IiByPSIzNCIgZmlsbD0iI2RiZWFmZSIvPgogIDxjaXJjbGUgY3g9IjExNDYiIGN5PSIxNDYiIHI9IjI0IiBmaWxsPSIjZGJlYWZlIi8+CiAgPHRleHQgeD0iMTA5OSIgeT0iMTU1IiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjE2IiBmaWxsPSIjMjQyOTJmIj5UYWt1bWkgUnVubmVyPC90ZXh0PgoKICA8IS0tIHJvdyAyIGxhYmVsIC0tPgogIDx0ZXh0IHg9IjMwIiB5PSIyNDEiIGZvbnQtc2l6ZT0iMTQiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjNTc2MDZhIj5Vc2luZyBjaWNkLXNlbnNvcjwvdGV4dD4KCiAgPCEtLSByb3cgMjogd29ya2Zsb3cgWUFNTCAoZG9jdW1lbnQpIC0tPgogIDxwYXRoIGQ9Ik0gMTIwIDI3OCBMIDE5MyAyNzggTCAyMDUgMjkwIEwgMjA1IDMzMyBMIDEyMCAzMzMgWiIgZmlsbD0iI2ZmZmZmZiIgc3Ryb2tlPSIjNmU3NzgxIiBzdHJva2Utd2lkdGg9IjEuNSIgc3Ryb2tlLWxpbmVqb2luPSJyb3VuZCIvPgogIDxwYXRoIGQ9Ik0gMTkzIDI3OCBMIDE5MyAyOTAgTCAyMDUgMjkwIFoiIGZpbGw9IiNlMWU3ZWQiIHN0cm9rZT0iIzZlNzc4MSIgc3Ryb2tlLXdpZHRoPSIxLjIiIHN0cm9rZS1saW5lam9pbj0icm91bmQiLz4KICA8bGluZSB4MT0iMTMyIiB5MT0iMjk2IiB4Mj0iMTc2IiB5Mj0iMjk2IiBzdHJva2U9IiNkMGQ3ZGUiIHN0cm9rZS13aWR0aD0iMiIvPgogIDxsaW5lIHgxPSIxMzIiIHkxPSIzMDYiIHgyPSIxNjAiIHkyPSIzMDYiIHN0cm9rZT0iI2QwZDdkZSIgc3Ryb2tlLXdpZHRoPSIyIi8+CiAgPHRleHQgeD0iMTYyIiB5PSIzNTMiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTYiIGZpbGw9IiMyNDI5MmYiPldvcmtmbG93IFlBTUw8L3RleHQ+CiAgPGxpbmUgeDE9IjIwNSIgeTE9IjMwNSIgeDI9IjMyNiIgeTI9IjMwNSIgc3Ryb2tlPSIjMjQyOTJmIiBzdHJva2Utd2lkdGg9IjIiIG1hcmtlci1lbmQ9InVybCgjYXJyb3cpIi8+CiAgPHRleHQgeD0iMjY2IiB5PSIyOTIiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTMiIGZpbGw9IiMyNDI5MmYiPlJ1bjwvdGV4dD4KCiAgPCEtLSByb3cgMjogR2l0SHViLWhvc3RlZCBydW5uZXIgKyBjaWNkLXNlbnNvciAocGlsbCkgLS0+CiAgPHJlY3QgeD0iMzMwIiB5PSIyNTAiIHdpZHRoPSIyMzIiIGhlaWdodD0iMTEwIiByeD0iMTAiIGZpbGw9IiNmNmY4ZmEiIHN0cm9rZT0iIzZlNzc4MSIgc3Ryb2tlLXdpZHRoPSIxLjUiLz4KICA8dGV4dCB4PSI0NDYiIHk9IjI4NSIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIxNiIgZmlsbD0iIzI0MjkyZiI+R2l0SHViLWhvc3RlZCBydW5uZXI8L3RleHQ+CiAgPHJlY3QgeD0iMzYxIiB5PSIzMTAiIHdpZHRoPSIxNzAiIGhlaWdodD0iMzQiIHJ4PSIxNyIgZmlsbD0iI2ViZjdmMCIgc3Ryb2tlPSIjMmRhNDRlIiBzdHJva2Utd2lkdGg9IjEuMiIvPgogIDx0ZXh0IHg9IjQ0NiIgeT0iMzMyIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjEzIiBmaWxsPSIjMjQyOTJmIj5jaWNkLXNlbnNvcjwvdGV4dD4KICA8bGluZSB4MT0iNTMxIiB5MT0iMzI3IiB4Mj0iMTAyNCIgeTI9IjMyNyIgc3Ryb2tlPSIjMjQyOTJmIiBzdHJva2Utd2lkdGg9IjIiIG1hcmtlci1lbmQ9InVybCgjYXJyb3cpIi8+CiAgPHRleHQgeD0iNzkyIiB5PSIzMTQiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTMiIGZpbGw9IiMyNDI5MmYiPlRyYWNlIGxvZ3M8L3RleHQ+CgogIDwhLS0gcm93IDI6IFRha3VtaSBSdW5uZXIgKGNsb3VkKSAtLT4KICA8ZWxsaXBzZSBjeD0iMTEwNCIgY3k9IjMzOSIgcng9Ijc2IiByeT0iMTkiIGZpbGw9IiNkYmVhZmUiLz4KICA8Y2lyY2xlIGN4PSIxMDU3IiBjeT0iMzE1IiByPSIyOSIgZmlsbD0iI2RiZWFmZSIvPgogIDxjaXJjbGUgY3g9IjExMDQiIGN5PSIyOTciIHI9IjM0IiBmaWxsPSIjZGJlYWZlIi8+CiAgPGNpcmNsZSBjeD0iMTE0NiIgY3k9IjMxNiIgcj0iMjQiIGZpbGw9IiNkYmVhZmUiLz4KICA8dGV4dCB4PSIxMDk5IiB5PSIzMjUiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTYiIGZpbGw9IiMyNDI5MmYiPlRha3VtaSBSdW5uZXI8L3RleHQ+Cjwvc3ZnPgo=" width="1266" height="395" class="img_aV4l"></p>
<p>cicd-sensor trace logs also work with the <a href="https://shisho.dev/docs/r/202608-takumi-runner-threat-detection">threat detection</a> feature released today.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="background">Background<a href="https://shisho.dev/docs/r/202608-takumi-runner-cicd-sensor-integration#background" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Takumi Hosted Runner collects eBPF traces — process executions, network connections, DNS queries, and file accesses — by running jobs on Takumi Runner's dedicated runners. On the other hand, moving jobs to Takumi Hosted Runner is sometimes difficult, whether due to execution environment constraints or the effort of migrating.</p>
<p>For those cases, we now provide a way to use cicd-sensor, which requires no migration of the execution environment. Add cicd-sensor to a CI/CD pipeline and specify Takumi Runner's Manager endpoint and credentials, and the trace logs will be sent to Takumi Runner.</p>
<p>As the architecture figure above shows, Takumi Hosted Runner collects trace logs by running CI/CD jobs on dedicated runners that we operate. The cicd-sensor integration instead adds cicd-sensor to the environment you already use — GitHub-hosted runners, self-hosted runners you operate yourself, and so on — and sends the logs traced there to Takumi Runner.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="benefits">Benefits<a href="https://shisho.dev/docs/r/202608-takumi-runner-cicd-sensor-integration#benefits" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Trace logs collected through cicd-sensor are managed the same way as Takumi Hosted Runner trace logs, so trace log visualization, search, and threat detection are all available for them.</p>
<p><strong>Trace log visualization</strong></p>
<p>You can review the <a href="https://shisho.dev/docs/t/runner/features/trace-visualization">visualized trace data</a> in the Takumi Runner console.</p>
<p><img decoding="async" loading="lazy" alt="Network tab" src="https://shisho.dev/docs/assets/images/job-network-a7b06401b6609f08394c040b6d95f57b.png" width="1280" height="720" class="img_aV4l"></p>
<p><strong>Trace log search</strong></p>
<p>Takumi Runner lets you <a href="https://shisho.dev/docs/t/runner/features/trace-search">search the contents of the collected trace logs</a>. You can check whether the CI/CD jobs that ran during a supply-chain incident were affected.</p>
<p><img decoding="async" loading="lazy" alt="Search results" src="https://shisho.dev/docs/assets/images/trace-search-results-f60887104370d8c0fc20b3d2ac58a145.png" width="2664" height="1652" class="img_aV4l"></p>
<p><strong>Threat detection</strong></p>
<p><a href="https://shisho.dev/docs/r/202608-takumi-runner-threat-detection">Threat detection</a> proactively investigates the impact of a supply-chain incident based on the trace logs and notifies you if you are affected. Since it removes the need to investigate yourself, it addresses gaps in expertise and the risk of missing an incident.</p>
<p><img decoding="async" loading="lazy" alt="Responding to a supply-chain incident: before vs. with threat detection" src="data:image/svg+xml;base64,PHN2ZyB4bWxucz0iaHR0cDovL3d3dy53My5vcmcvMjAwMC9zdmciIHhtbG5zOnhsaW5rPSJodHRwOi8vd3d3LnczLm9yZy8xOTk5L3hsaW5rIiB3aWR0aD0iMTYwMCIgaGVpZ2h0PSI4MzgiIHZpZXdCb3g9IjAgMCAxNjAwIDgzOCIgcm9sZT0iaW1nIiBmb250LWZhbWlseT0iJ0hpcmFnaW5vIEtha3UgR290aGljIFByb04nLCAnSGlyYWdpbm8gU2FucycsICdZdSBHb3RoaWMnLCBNZWlyeW8sICdOb3RvIFNhbnMgSlAnLCBzYW5zLXNlcmlmIj4KICA8dGl0bGU+UmVzcG9uZGluZyB0byBhIHN1cHBseS1jaGFpbiBpbmNpZGVudDogYmVmb3JlIHZzLiB3aXRoIHRocmVhdCBkZXRlY3Rpb248L3RpdGxlPgogIDxkZWZzPgogICAgPCEtLSB0aGljayBibG9jayBhcnJvdywgNjQgd2lkZSB4IDQ0IHRhbGwsIHBvaW50aW5nIHJpZ2h0OyBmaWxsIHNldCBwZXIgdXNlIC0tPgogICAgPHBvbHlnb24gaWQ9ImJsb2NrLWFycm93IiBwb2ludHM9IjAsLTExIDM4LC0xMSAzOCwtMjIgNjQsMCAzOCwyMiAzOCwxMSAwLDExIi8+CiAgICA8IS0tIGNsaXBib2FyZCBpY29uICg5MCB4IDExNiwgdG9wLWxlZnQgYXQgMCwwKTsgZnJhbWUgY29sb3IgPSBjdXJyZW50Q29sb3I7IGNoZWNrIG1hcmtzIGRyYXduIHNlcGFyYXRlbHkgLS0+CiAgICA8ZyBpZD0iY2xpcGJvYXJkIiBmaWxsPSJub25lIiBzdHJva2U9ImN1cnJlbnRDb2xvciIgc3Ryb2tlLXdpZHRoPSI1IiBzdHJva2UtbGluZWNhcD0icm91bmQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiPgogICAgICA8cmVjdCB4PSIwIiB5PSI4IiB3aWR0aD0iOTAiIGhlaWdodD0iMTA4IiByeD0iOCIgZmlsbD0iI2ZmZmZmZiIvPgogICAgICA8cmVjdCB4PSIyNyIgeT0iMCIgd2lkdGg9IjM2IiBoZWlnaHQ9IjE4IiByeD0iNSIgZmlsbD0iY3VycmVudENvbG9yIiBzdHJva2U9Im5vbmUiLz4KICAgICAgPHBhdGggZD0iTTQ3IDQzIEg3NyBNNDcgNjcgSDc3IE00NyA5MSBINzciIHN0cm9rZS13aWR0aD0iNCIvPgogICAgPC9nPgogICAgPHBhdGggaWQ9ImNsaXBib2FyZC1jaGVja3MiIGQ9Ik0xNyA0MyBMMjUgNTEgTDM5IDM1IE0xNyA2NyBMMjUgNzUgTDM5IDU5IE0xNyA5MSBMMjUgOTkgTDM5IDgzIiBmaWxsPSJub25lIiBzdHJva2Utd2lkdGg9IjQuNSIgc3Ryb2tlLWxpbmVjYXA9InJvdW5kIiBzdHJva2UtbGluZWpvaW49InJvdW5kIi8+CiAgPC9kZWZzPgoKICA8cmVjdCB3aWR0aD0iMTYwMCIgaGVpZ2h0PSI4MzgiIGZpbGw9IiNmZmZmZmYiLz4KCiAgPCEtLSB0aXRsZSAtLT4KICA8dGV4dCB4PSI4MDAiIHk9IjcyIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjQyIiBmb250LXdlaWdodD0iYm9sZCIgZmlsbD0iIzI0MjkyZiI+UmVzcG9uZGluZyB0byBhIHN1cHBseS1jaGFpbiBpbmNpZGVudDwvdGV4dD4KCiAgPCEtLSA9PT09PT09PT09PT09PT09PT09PT0gcm93IDE6IGJlZm9yZSA9PT09PT09PT09PT09PT09PT09PT0gLS0+CiAgPHJlY3QgeD0iNDAiIHk9IjExOCIgd2lkdGg9IjE1MjAiIGhlaWdodD0iMzEzIiByeD0iMTgiIGZpbGw9IiNmNmY0ZjQiLz4KICA8cmVjdCB4PSI2MiIgeT0iMjcwIiB3aWR0aD0iMTUwIiBoZWlnaHQ9IjUwIiByeD0iMjUiIGZpbGw9IiM5YjZiNmIiLz4KICA8dGV4dCB4PSIxMzciIHk9IjMwNCIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIyNiIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiNmZmZmZmYiPkJlZm9yZTwvdGV4dD4KCiAgPCEtLSBzdGVwIDE6IGNoZWNrIGJsb2dzIC8gWCAoc21hcnRwaG9uZSBmZWVkLCBmaW5nZXIgdGFwcGluZyB0aGUgc2NyZWVuKSAtLT4KICA8dGV4dCB4PSI0MzAiIHk9IjE3NCIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIzNiIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiM1ZjVmNWYiPkNoZWNrIGJsb2dzICZhbXA7IFg8L3RleHQ+CiAgPGcgZmlsbD0ibm9uZSIgc3Ryb2tlPSIjOGE3YTdhIiBzdHJva2Utd2lkdGg9IjYiIHN0cm9rZS1saW5lY2FwPSJyb3VuZCIgc3Ryb2tlLWxpbmVqb2luPSJyb3VuZCI+CiAgICA8cmVjdCB4PSIzODQiIHk9IjIxNCIgd2lkdGg9IjkyIiBoZWlnaHQ9IjE2MSIgcng9IjE2IiBmaWxsPSIjZmZmZmZmIi8+CiAgICA8cGF0aCBkPSJNNDE2IDIzMCBINDQzIiBzdHJva2Utd2lkdGg9IjUiLz4KICAgIDxjaXJjbGUgY3g9IjQwNiIgY3k9IjI2MiIgcj0iOSIgZmlsbD0iI2M5YjhiOCIgc3Ryb2tlPSJub25lIi8+CiAgICA8cGF0aCBkPSJNNDIzIDI1NyBINDU3IE00MjMgMjcwIEg0NDggTTQwMyAyOTUgSDQ1NyBNNDAzIDMxMSBINDQ4IE00MDMgMzI3IEg0NTciIHN0cm9rZT0iI2M5YjhiOCIgc3Ryb2tlLXdpZHRoPSI1Ii8+CiAgICA8cGF0aCBkPSJNNDE2IDM1OSBINDQzIiBzdHJva2U9IiNjOWI4YjgiIHN0cm9rZS13aWR0aD0iNSIvPgogIDwvZz4KICA8ZyB0cmFuc2Zvcm09InRyYW5zbGF0ZSg0NjAgMjY0KSByb3RhdGUoLTMwKSBzY2FsZSgxLjEpIiBmaWxsPSJub25lIiBzdHJva2UtbGluZWNhcD0icm91bmQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiPgogICAgPHBhdGggZD0iTS0yMC44IC00IEEyNCAyNCAwIDAgMSAyMC44IC00IE0tMTQuNCAtMSBBMTcgMTcgMCAwIDEgMTQuNCAtMSIgc3Ryb2tlPSIjZDM3MDZjIiBzdHJva2Utd2lkdGg9IjMuNiIvPgogICAgPHBhdGggZD0iTS04IDggQTggOCAwIDAgMSA4IDggTDggMzYgQTQgNCAwIDAgMSAxNiAzNiBBNCA0IDAgMCAxIDI0IDM2IEE2IDYgMCAwIDEgMzAgNDIgTDMwIDYwIEExMCAxMCAwIDAgMSAyMCA3MCBMLTYgNzAgQTEwIDEwIDAgMCAxIC0xNiA2MCBMLTE2IDQ2IFEtMTYgNDAgLTggNDAgWiIgZmlsbD0iI2ZmZmZmZiIgc3Ryb2tlPSIjOGE3YTdhIiBzdHJva2Utd2lkdGg9IjQuNSIvPgogIDwvZz4KICA8ZWxsaXBzZSBjeD0iNTEwIiBjeT0iMzgxIiByeD0iMTEyIiByeT0iMjYiIGZpbGw9IiNmZmZmZmYiIHN0cm9rZT0iI2QzNzA2YyIgc3Ryb2tlLXdpZHRoPSIzIi8+CiAgPHRleHQgeD0iNTEwIiB5PSIzODgiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMjAiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjZDM3MDZjIj5NaWdodCBtaXNzIGl04oCmPC90ZXh0PgoKICA8dXNlIHhsaW5rOmhyZWY9IiNibG9jay1hcnJvdyIgeD0iNjI4IiB5PSIyOTUiIGZpbGw9IiNiOGE5YTkiLz4KCiAgPCEtLSBzdGVwIDI6IHNlYXJjaCB0aGUgbG9ncyB5b3Vyc2VsZiAoc3RhY2sgb2YgbG9nIHBhZ2VzICsgbWFnbmlmaWVyKSAtLT4KICA8dGV4dCB4PSI4OTAiIHk9IjE3NCIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIzNiIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiM1ZjVmNWYiPlNlYXJjaCBsb2dzIHlvdXJzZWxmPC90ZXh0PgogIDxnIGZpbGw9Im5vbmUiIHN0cm9rZT0iIzlhODY4NiIgc3Ryb2tlLXdpZHRoPSI2IiBzdHJva2UtbGluZWNhcD0icm91bmQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiPgogICAgPHJlY3QgeD0iODM2IiB5PSIyMTQiIHdpZHRoPSIxMjEiIGhlaWdodD0iMTQ4IiByeD0iOCIgZmlsbD0iI2Y0ZWRlZCIgc3Ryb2tlPSIjYjM5YzljIi8+CiAgICA8cmVjdCB4PSI4MjMiIHk9IjIyNyIgd2lkdGg9IjEyMSIgaGVpZ2h0PSIxNDgiIHJ4PSI4IiBmaWxsPSIjZmZmZmZmIi8+CiAgICA8cGF0aCBkPSJNODQyIDI1NCBIOTI1IE04NDIgMjc0IEg5MDkgTTg0MiAyOTQgSDkyOCBNODQyIDMxNCBIOTAxIE04NDIgMzM1IEg5MjMgTTg0MiAzNTUgSDkxMiIgc3Ryb2tlPSIjYjM5YzljIiBzdHJva2Utd2lkdGg9IjUiLz4KICA8L2c+CiAgPGNpcmNsZSBjeD0iOTUwIiBjeT0iMjY3IiByPSIzNSIgZmlsbD0iI2ZmZmZmZiIgZmlsbC1vcGFjaXR5PSIwLjUiIHN0cm9rZT0iI2QzNzA2YyIgc3Ryb2tlLXdpZHRoPSI4Ii8+CiAgPHBhdGggZD0iTTk3NSAyOTIgTDEwMDYgMzIzIiBzdHJva2U9IiNkMzcwNmMiIHN0cm9rZS13aWR0aD0iMTIiIHN0cm9rZS1saW5lY2FwPSJyb3VuZCIvPgogIDxlbGxpcHNlIGN4PSI5NzAiIGN5PSIzODEiIHJ4PSIxMDAiIHJ5PSIyNiIgZmlsbD0iI2ZmZmZmZiIgc3Ryb2tlPSIjZDM3MDZjIiBzdHJva2Utd2lkdGg9IjMiLz4KICA8dGV4dCB4PSI5NzAiIHk9IjM4OCIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIyMCIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiNkMzcwNmMiPlN1Y2ggYSBoYXNzbGXigKY8L3RleHQ+CgogIDx1c2UgeGxpbms6aHJlZj0iI2Jsb2NrLWFycm93IiB4PSIxMDg4IiB5PSIyOTUiIGZpbGw9IiNiOGE5YTkiLz4KCiAgPCEtLSBzdGVwIDM6IHBvc3QtaW5jaWRlbnQgcmVzcG9uc2UgKGNsaXBib2FyZCkgLS0+CiAgPHRleHQgeD0iMTM1MCIgeT0iMTc0IiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjM2IiBmb250LXdlaWdodD0iYm9sZCIgZmlsbD0iIzVmNWY1ZiI+UmVzcG9uZDwvdGV4dD4KICA8dXNlIHhsaW5rOmhyZWY9IiNjbGlwYm9hcmQiIHRyYW5zZm9ybT0idHJhbnNsYXRlKDEyOTAgMjE0KSBzY2FsZSgxLjM0NCkiIGNvbG9yPSIjOGE3YTdhIi8+CiAgPHVzZSB4bGluazpocmVmPSIjY2xpcGJvYXJkLWNoZWNrcyIgdHJhbnNmb3JtPSJ0cmFuc2xhdGUoMTI5MCAyMTQpIHNjYWxlKDEuMzQ0KSIgc3Ryb2tlPSIjYTA5MDkwIi8+CiAgPHRleHQgeD0iMTM1MCIgeT0iNDAyIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjIyIiBmaWxsPSIjN2E3YTdhIj4oaWYgYWZmZWN0ZWQpPC90ZXh0PgoKICA8IS0tID09PT09PT09PT09PT09PT09PT09PSByb3cgMjogd2l0aCB0aHJlYXQgZGV0ZWN0aW9uID09PT09PT09PT09PT09PT09PT09PSAtLT4KICA8cmVjdCB4PSI0MCIgeT0iNDcxIiB3aWR0aD0iMTUyMCIgaGVpZ2h0PSIzMjciIHJ4PSIxOCIgZmlsbD0iI2VlZjRmYyIvPgogIDxyZWN0IHg9IjYyIiB5PSI2MjkiIHdpZHRoPSIyNjAiIGhlaWdodD0iNTAiIHJ4PSIyNSIgZmlsbD0iIzJmNmZkNiIvPgogIDx0ZXh0IHg9IjE5MiIgeT0iNjYzIiB0ZXh0LWFuY2hvcj0ibWlkZGxlIiBmb250LXNpemU9IjI2IiBmb250LXdlaWdodD0iYm9sZCIgZmlsbD0iI2ZmZmZmZiI+VGhyZWF0IGRldGVjdGlvbjwvdGV4dD4KCiAgPCEtLSBzdGVwOiBSdW5uZXIgZG9lcyBpdCBhdXRvbWF0aWNhbGx5IChzaGllbGQgd2l0aCByYWRhciBzd2VlcCwgYmVsbCBhdHRhY2hlZCkg4oCUIHJlcGxhY2VzIHN0ZXBzIDEgYW5kIDIgLS0+CiAgPHRleHQgeD0iNjYwIiB5PSI1MjciIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMzYiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjNWY1ZjVmIj5SdW5uZXIgaGFuZGxlcyBpdCBmb3IgeW91PC90ZXh0PgogIDxnIHRyYW5zZm9ybT0idHJhbnNsYXRlKDY2MCA2NTQpIHNjYWxlKDEuNCkiPgogICAgPHBhdGggZD0iTTAgLTYyIEMyMiAtNTAgNDIgLTQ0IDU2IC00NCBDNTYgLTIgNDAgMzQgMCA2MiBDLTQwIDM0IC01NiAtMiAtNTYgLTQ0IEMtNDIgLTQ0IC0yMiAtNTAgMCAtNjIgWiIgZmlsbD0iI2VhZjNmZiIgc3Ryb2tlPSIjMmY2ZmQ2IiBzdHJva2Utd2lkdGg9IjQiIHN0cm9rZS1saW5lam9pbj0icm91bmQiLz4KICAgIDxjaXJjbGUgY3g9IjAiIGN5PSItNiIgcj0iMzIiIGZpbGw9IiNmZmZmZmYiIHN0cm9rZT0iIzJmNmZkNiIgc3Ryb2tlLXdpZHRoPSIyLjUiLz4KICAgIDxjaXJjbGUgY3g9IjAiIGN5PSItNiIgcj0iMTgiIGZpbGw9Im5vbmUiIHN0cm9rZT0iIzlmYzBlYSIgc3Ryb2tlLXdpZHRoPSIxLjUiLz4KICAgIDxwYXRoIGQ9Ik0tMzIgLTYgSDMyIE0wIC0zOCBWMjYiIHN0cm9rZT0iIzlmYzBlYSIgc3Ryb2tlLXdpZHRoPSIxLjUiLz4KICAgIDxwYXRoIGQ9Ik0wIC02IEwwIC0zOCBBMzIgMzIgMCAwIDEgMjcuNyAtMjIgWiIgZmlsbD0iIzJmNmZkNiIgZmlsbC1vcGFjaXR5PSIwLjMiLz4KICAgIDxwYXRoIGQ9Ik0wIC02IEwyNy43IC0yMiIgc3Ryb2tlPSIjMmY2ZmQ2IiBzdHJva2Utd2lkdGg9IjIuNSIgc3Ryb2tlLWxpbmVjYXA9InJvdW5kIi8+CiAgICA8Y2lyY2xlIGN4PSIxMiIgY3k9Ii0yNCIgcj0iNC41IiBmaWxsPSIjMmZhMzZiIi8+CiAgPC9nPgogIDxnIHRyYW5zZm9ybT0idHJhbnNsYXRlKDc0MiA2MDcpIHNjYWxlKDEuMDUpIj4KICAgIDxwYXRoIGQ9Ik0tMjQgMTYgQy0yNCAtMTQgLTE0IC0yOCAwIC0zMCBDMTQgLTI4IDI0IC0xNCAyNCAxNiBMMzAgMjQgSC0zMCBaIiBmaWxsPSIjZmZmZmZmIiBzdHJva2U9IiMyZjZmZDYiIHN0cm9rZS13aWR0aD0iNC41IiBzdHJva2UtbGluZWpvaW49InJvdW5kIi8+CiAgICA8Y2lyY2xlIGN4PSIwIiBjeT0iMzIiIHI9IjYiIGZpbGw9IiMyZjZmZDYiLz4KICAgIDxjaXJjbGUgY3g9IjAiIGN5PSItMzQiIHI9IjQiIGZpbGw9IiMyZjZmZDYiLz4KICAgIDxjaXJjbGUgY3g9IjI2IiBjeT0iLTI0IiByPSIxMyIgZmlsbD0iIzJmYTM2YiIgc3Ryb2tlPSIjZmZmZmZmIiBzdHJva2Utd2lkdGg9IjMiLz4KICAgIDx0ZXh0IHg9IjI2IiB5PSItMTciIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMTgiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjZmZmZmZmIj4hPC90ZXh0PgogIDwvZz4KICA8ZWxsaXBzZSBjeD0iNzUwIiBjeT0iNzQ3IiByeD0iMTcwIiByeT0iMjciIGZpbGw9IiNmZmZmZmYiIHN0cm9rZT0iIzJjOGE1OCIgc3Ryb2tlLXdpZHRoPSIzIi8+CiAgPHRleHQgeD0iNzUwIiB5PSI3NTQiIHRleHQtYW5jaG9yPSJtaWRkbGUiIGZvbnQtc2l6ZT0iMjAiIGZvbnQtd2VpZ2h0PSJib2xkIiBmaWxsPSIjMmM4YTU4Ij5Zb3UgZ2V0IG5vdGlmaWVkIGlmIGFmZmVjdGVkPC90ZXh0PgoKICA8dXNlIHhsaW5rOmhyZWY9IiNibG9jay1hcnJvdyIgeD0iMTA4OCIgeT0iNjU0IiBmaWxsPSIjMmY2ZmQ2Ii8+CgogIDwhLS0gcG9zdC1pbmNpZGVudCByZXNwb25zZSAoYWZ0ZXIpOiBzYW1lIGljb24sIHNhbWUgY29sdW1uIGFzIGFib3ZlIC0tPgogIDx0ZXh0IHg9IjEzNTAiIHk9IjUyNyIgdGV4dC1hbmNob3I9Im1pZGRsZSIgZm9udC1zaXplPSIzNiIgZm9udC13ZWlnaHQ9ImJvbGQiIGZpbGw9IiM1ZjVmNWYiPlJlc3BvbmQ8L3RleHQ+CiAgPHVzZSB4bGluazpocmVmPSIjY2xpcGJvYXJkIiB0cmFuc2Zvcm09InRyYW5zbGF0ZSgxMjkwIDU3Nikgc2NhbGUoMS4zNDQpIiBjb2xvcj0iIzJmNmZkNiIvPgogIDx1c2UgeGxpbms6aHJlZj0iI2NsaXBib2FyZC1jaGVja3MiIHRyYW5zZm9ybT0idHJhbnNsYXRlKDEyOTAgNTc2KSBzY2FsZSgxLjM0NCkiIHN0cm9rZT0iIzJmYTM2YiIvPgo8L3N2Zz4K" width="1600" height="838" class="img_aV4l"></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="supported-cicd-pipelines">Supported CI/CD pipelines<a href="https://shisho.dev/docs/r/202608-takumi-runner-cicd-sensor-integration#supported-cicd-pipelines" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>The cicd-sensor integration does not depend on the execution environment, so as a rule it supports the CI/CD pipelines that cicd-sensor supports. At the time of writing, GitHub Actions and GitLab CI/CD are supported. For GitLab CI/CD, self-hosted GitLab Runners (Docker executor) are covered.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202608-takumi-runner-cicd-sensor-integration#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>The cicd-sensor integration takes three steps:</p>
<ol>
<li>Add cicd-sensor to the CI/CD job</li>
<li>Set Takumi Runner's Manager as cicd-sensor's <code>manager-url</code></li>
<li>Set the credentials as cicd-sensor's <code>manager-token</code></li>
</ol>
<h3 class="anchor anchorWithStickyNavbar_k394" id="github-hosted-runners">GitHub-hosted runners<a href="https://shisho.dev/docs/r/202608-takumi-runner-cicd-sensor-integration#github-hosted-runners" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>Add the cicd-sensor step at the beginning of the job and specify the Manager endpoint in the <code>manager-url</code> parameter.</p>
<div class="language-yaml codeBlockContainer_tXdS theme-code-block" style="--prism-color:#393A34;--prism-background-color:#f6f8fa"><div class="codeBlockContent_zXtR"><pre tabindex="0" class="prism-code language-yaml codeBlock_qqWd thin-scrollbar" style="color:#393A34;background-color:#f6f8fa"><code class="codeBlockLines_CmGJ"><span class="token-line" style="color:#393A34"><span class="token key atrule" style="color:#00a4db">jobs</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">  </span><span class="token key atrule" style="color:#00a4db">build</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">    </span><span class="token key atrule" style="color:#00a4db">runs-on</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> ubuntu</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">latest</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">    </span><span class="token key atrule" style="color:#00a4db">steps</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">      </span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain"> </span><span class="token key atrule" style="color:#00a4db">uses</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> cicd</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">sensor/cicd</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">sensor</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">action@6511eb44c91d71b2b93d71193b1bf2cb18352f66 </span><span class="token comment" style="color:#999988;font-style:italic"># v0.0.38</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">        </span><span class="token key atrule" style="color:#00a4db">with</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">          </span><span class="token key atrule" style="color:#00a4db">manager-url</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> https</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain">//manager.cicdsensor.cloud.shisho.dev</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">          </span><span class="token key atrule" style="color:#00a4db">manager-token</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> $</span><span class="token punctuation" style="color:#393A34">{</span><span class="token punctuation" style="color:#393A34">{</span><span class="token plain"> secrets.SHISHO_CICD_SENSOR_TOKEN </span><span class="token punctuation" style="color:#393A34">}</span><span class="token punctuation" style="color:#393A34">}</span><br></span></code></pre><div class="buttonGroup_yRlK"><button type="button" aria-label="Copy code to clipboard" title="Copy" class="clean-btn"><span class="copyButtonIcons_yBV4" aria-hidden="true"><svg viewBox="0 0 24 24" class="copyButtonIcon_Ctry"><path fill="currentColor" d="M19,21H8V7H19M19,5H8A2,2 0 0,0 6,7V21A2,2 0 0,0 8,23H19A2,2 0 0,0 21,21V7A2,2 0 0,0 19,5M16,1H4A2,2 0 0,0 2,3V17H4V3H16V1Z"></path></svg><svg viewBox="0 0 24 24" class="copyButtonSuccessIcon_FUe1"><path fill="currentColor" d="M21,7L9,19L3.5,13.5L4.91,12.09L9,16.17L19.59,5.59L21,7Z"></path></svg></span></button></div></div></div>
<p>Authentication (<code>manager-token</code>) is performed through a Shisho Cloud bot. For how to set up authentication, including creating the bot, see the <a href="https://shisho.dev/docs/t/runner/features/cicdsensor-integration">user guide</a>.</p>
<p>Once the job execution completes, the job and its traces are reflected in the Takumi Runner console.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="github-self-hosted-runners-and-gitlab-cicd">GitHub self-hosted runners and GitLab CI/CD<a href="https://shisho.dev/docs/r/202608-takumi-runner-cicd-sensor-integration#github-self-hosted-runners-and-gitlab-cicd" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>In these environments, cicd-sensor runs on the runner's host, so installing cicd-sensor and configuring the Manager endpoint happen on the host rather than in the pipeline. For how to set this up, see the <a href="https://cicd-sensor.github.io/user-guide/self-hosted-install.html" target="_blank" rel="noopener noreferrer">cicd-sensor documentation</a>.</p>
<p>Takumi Runner's Manager endpoint is <code>https://manager.cicdsensor.cloud.shisho.dev</code>.</p>
<p>For the credentials, issue an API key in the Takumi console and specify it as the <code>manager-token</code>. For details on creating a bot and API keys, see the <a href="https://shisho.dev/docs/t/runner/features/cicdsensor-integration">user guide</a>.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="pricing">Pricing<a href="https://shisho.dev/docs/r/202608-takumi-runner-cicd-sensor-integration#pricing" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>The cicd-sensor integration requires the Takumi Runner base plan.</p>
<p>Within the base plan, we accept trace logs for up to a total of 3,000 minutes of job run time per month. From September 1, 2026, accepting logs for job runs beyond 3,000 minutes incurs a per-minute fee.</p>
<div class="theme-admonition theme-admonition-info admonition_ODxW alert alert--info"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 14 16"><path fill-rule="evenodd" d="M7 2.3c3.14 0 5.7 2.56 5.7 5.7s-2.56 5.7-5.7 5.7A5.71 5.71 0 0 1 1.3 8c0-3.14 2.56-5.7 5.7-5.7zM7 1C3.14 1 0 4.14 0 8s3.14 7 7 7 7-3.14 7-7-3.14-7-7-7zm1 3H6v5h2V4zm0 6H6v2h2v-2z"></path></svg></span>info</div><div class="admonitionContent_Kqb4"><p>Until August 31, 2026, we accept trace logs with no 3,000-minute cap.</p></div></div>
<p>For details on the cicd-sensor integration pricing, see <a href="https://shisho.dev/docs/t/runner/billing/pricing">Pricing</a>.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started-with-takumi-runner">Getting Started with Takumi Runner<a href="https://shisho.dev/docs/r/202608-takumi-runner-cicd-sensor-integration#getting-started-with-takumi-runner" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>To use Takumi Runner, including the cicd-sensor integration, you need a Takumi subscription and Runner enabled.</p>
<ol>
<li>Go to <a href="https://cloud.shisho.dev/hello/takumi" target="_blank" rel="noopener noreferrer">https://cloud.shisho.dev/hello/takumi</a> and sign in</li>
<li>Register your organization and subscribe to Takumi</li>
<li>Open <strong>Runner</strong> &gt; <strong>Settings</strong> from the sidebar on the left</li>
<li>Click the "Enable" button to enable Runner</li>
</ol>
<p><img decoding="async" loading="lazy" alt="Runner setup screen" src="https://shisho.dev/docs/assets/images/ui-runner-settings-e3e300eb20582fa02ccf7a0928c39553.png" width="2000" height="1024" class="img_aV4l"></p>
<p>Once Runner is enabled, follow the <a href="https://shisho.dev/docs/t/runner/features/cicdsensor-integration">cicd-sensor integration user guide</a> to complete the setup.</p>]]></content>
        <author>
            <name>Rio Nishimori</name>
            <uri>https://github.com/rio828</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi Graybox Assessment Now Available]]></title>
        <id>https://shisho.dev/docs/r/202608-takumi-graybox</id>
        <link href="https://shisho.dev/docs/r/202608-takumi-graybox"/>
        <updated>2026-08-18T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[Takumi reads your source code to find vulnerabilities, then confirms which of them reproduce against the running application]]></summary>
        <content type="html"><![CDATA[<p>Takumi now supports graybox assessment.</p>
<p>Specify both your source code and the URL of the application running that code. Takumi analyzes the code to enumerate candidate vulnerabilities and attacks the running application, then <strong>reports only the ones it manages to reproduce as findings</strong>.</p>
<p><img decoding="async" loading="lazy" alt="Graybox assessment feature" src="https://shisho.dev/docs/assets/images/eyecatch-64b37d8a3c1f20ad82401762cb992177.png" width="2400" height="1260" class="img_aV4l"></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="overview">Overview<a href="https://shisho.dev/docs/r/202608-takumi-graybox#overview" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Whitebox assessment reads the source code directly, so it can find vulnerabilities that an external investigation — that is, a blackbox approach — could never reach. What the code cannot tell you is whether a candidate it surfaces actually reproduces in the environment you run. Blackbox assessment reports only vulnerabilities that do reproduce in that environment, but it struggles with vulnerabilities that are hard to find without reading the code, and with those hidden in functionality that is not publicly exposed.</p>
<p>Graybox assessment takes the strengths of both. <strong>Static analysis enumerates candidate vulnerabilities comprehensively, and every candidate is then verified for reproducibility against the running application, so the assessment delivers coverage and accuracy at the same time.</strong></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="reports-backed-by-reproduction">Reports Backed by Reproduction<a href="https://shisho.dev/docs/r/202608-takumi-graybox#reports-backed-by-reproduction" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Every finding recorded in a graybox report was reproduced against your running application. Candidates that static analysis raised but dynamic verification could not reproduce are recorded in a separate section of the report instead of as findings, so reading the report is enough to tell which vulnerabilities actually reproduce.</p>
<p>Each finding also documents the procedure used to reproduce it. A developer can follow the same steps to confirm that the vulnerability occurs, and can run them again after a fix to verify that the fix holds.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202608-takumi-graybox#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>This feature is available to all "Takumi byGMO" users and can be freely used within your monthly credit allowance. No additional fees or plan changes required.</p>
<p>Click the "Create Assessment" button in the "Assessment" tab of the global sidebar, then select "Graybox Assessment".</p>
<p>▼ User Guide: <a href="https://shisho.dev/docs/t/assessment/features/graybox-assessment">Graybox Assessment</a></p>]]></content>
        <author>
            <name>Tsubasa Umeuchi</name>
            <uri>https://github.com/Szarny</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi Assessments Now Support Email-Based MFA]]></title>
        <id>https://shisho.dev/docs/r/202608-takumi-disposable-mailbox</id>
        <link href="https://shisho.dev/docs/r/202608-takumi-disposable-mailbox"/>
        <updated>2026-08-17T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[Applications that require a one-time code delivered by email can now be assessed.]]></summary>
        <content type="html"><![CDATA[<p>Takumi assessments now support applications that require multi-factor authentication (MFA) by email.</p>
<p><img decoding="async" loading="lazy" alt="Credential configuration UI" src="https://shisho.dev/docs/assets/images/mailbox-setting-112cc62325fd8d2fa9c78424c23059f2.png" width="1568" height="339" class="img_aV4l"></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="overview">Overview<a href="https://shisho.dev/docs/r/202608-takumi-disposable-mailbox#overview" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Takumi did not support MFA by email, so it had to be turned off for every assessment to run properly.</p>
<p>With this release, blackbox assessments and penetration tests let you pick an email address that Takumi can receive mail at during the assessment.</p>
<p>This is not limited to one-time codes for MFA — it covers any feature that relies on email, such as magic links and sign-up confirmation messages.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202608-takumi-disposable-mailbox#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>This feature is available to all organizations from the blackbox assessment and penetration test dispatch screens.</p>
<p>When you add a credential, select "Takumi-managed email" as the account email, then either issue a new address or pick one your organization already holds. Up to 5 addresses can be registered.</p>
<p>For how to configure the address and register it on the target application, see <a href="https://shisho.dev/docs/t/assessment/features/blackbox-assessment#disposable-mailbox">Signing In With an Emailed One-Time Code</a>.</p>]]></content>
        <author>
            <name>Mokusou</name>
            <uri>https://github.com/0xMokusou</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Request to Update the AWS RDS Review Workflow in CSPM]]></title>
        <id>https://shisho.dev/docs/r/202608-rds-vpcless-aurora</id>
        <link href="https://shisho.dev/docs/r/202608-rds-vpcless-aurora"/>
        <updated>2026-08-07T02:00:00.000Z</updated>
        <summary type="html"><![CDATA[A notice for organizations using CSPM. Please update the workflow containing the managed review item to review Aurora clusters created with AWS's express configuration correctly.]]></summary>
        <content type="html"><![CDATA[<p>Due to <a href="https://docs.aws.amazon.com/AmazonRDS/latest/AuroraUserGuide/CHAP_GettingStartedAurora.AuroraPostgreSQL.ExpressConfig.html" target="_blank" rel="noopener noreferrer">express configuration</a>, a way of creating Aurora clusters without a VPC that AWS introduced in March 2026, we identified that the managed review item "Ensure that RDS instances are deployed in a VPC" (RDS.18) provided by Flatt Security could not judge instances in this configuration correctly.</p>
<p>We have published a workflow that addresses this issue, so please update yours.</p>
<div class="theme-admonition theme-admonition-info admonition_ODxW alert alert--info"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 14 16"><path fill-rule="evenodd" d="M7 2.3c3.14 0 5.7 2.56 5.7 5.7s-2.56 5.7-5.7 5.7A5.71 5.71 0 0 1 1.3 8c0-3.14 2.56-5.7 5.7-5.7zM7 1C3.14 1 0 4.14 0 8s3.14 7 7 7 7-3.14 7-7-3.14-7-7-7zm1 3H6v5h2V4zm0 6H6v2h2v-2z"></path></svg></span>info</div><div class="admonitionContent_Kqb4"><p>This notice concerns the managed reviews for AWS in CSPM. The update described here is not needed for organizations that match any of the following.</p><ul>
<li>Organizations using only Takumi byGMO</li>
<li>Organizations not reviewing AWS environments with CSPM</li>
<li>Organizations that have not registered the workflow "Prebundle: Review AWS RDS posture (FSBP)" described below</li>
</ul></div></div>
<h2 class="anchor anchorWithStickyNavbar_k394" id="background">Background<a href="https://shisho.dev/docs/r/202608-rds-vpcless-aurora#background" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>In March 2026, AWS introduced <a href="https://docs.aws.amazon.com/AmazonRDS/latest/AuroraUserGuide/CHAP_GettingStartedAurora.AuroraPostgreSQL.ExpressConfig.html" target="_blank" rel="noopener noreferrer">express configuration</a>, a way of creating Aurora clusters.</p>
<p>Unlike conventional Aurora clusters, a cluster created with <a href="https://docs.aws.amazon.com/AmazonRDS/latest/AuroraUserGuide/CHAP_GettingStartedAurora.AuroraPostgreSQL.ExpressConfig.html" target="_blank" rel="noopener noreferrer">express configuration</a> is not associated with a VPC.</p>
<p>The managed review item "Ensure that RDS instances are deployed in a VPC" (RDS.18) judges VPC membership from the DB subnet group the DB instance refers to. Aurora clusters created with <a href="https://docs.aws.amazon.com/AmazonRDS/latest/AuroraUserGuide/CHAP_GettingStartedAurora.AuroraPostgreSQL.ExpressConfig.html" target="_blank" rel="noopener noreferrer">express configuration</a> therefore fall outside this premise and could not be judged correctly.</p>
<p>Anticipating that Aurora clusters in this configuration will come into use, we would appreciate your cooperation in updating this review workflow to prevent incorrect review results.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="what-to-update">What to Update<a href="https://shisho.dev/docs/r/202608-rds-vpcless-aurora#what-to-update" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>The target of this update is a single job in the following workflow.</p>
<table><thead><tr><th>Target</th><th>ID</th><th>Name</th></tr></thead><tbody><tr><td>Workflow</td><td><code>prebundle-aws-fsbp-rds</code></td><td>Prebundle: Review AWS RDS posture (FSBP)</td></tr><tr><td>Job</td><td><code>instance-vpc</code></td><td>Review instance vpc</td></tr></tbody></table>
<h2 class="anchor anchorWithStickyNavbar_k394" id="what-you-need-to-do">What You Need to Do<a href="https://shisho.dev/docs/r/202608-rds-vpcless-aurora#what-you-need-to-do" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>The latest GraphQL query and Rego policy are available in the <a href="https://github.com/flatt-security/shisho-cloud-managed-workflows/tree/main/workflows/csp/aws-fsbp/rds/instance-vpc" target="_blank" rel="noopener noreferrer"><code>workflows/csp/aws-fsbp/rds/instance-vpc</code></a> directory of the <a href="https://github.com/flatt-security/shisho-cloud-managed-workflows" target="_blank" rel="noopener noreferrer">shisho-cloud-managed-workflows</a> repository. Please replace yours with them.</p>
<p>For reference, "Ensure that RDS instances are deployed in a VPC" (RDS.18) has already been removed from the review items of its source standard, <a href="https://docs.aws.amazon.com/securityhub/latest/userguide/fsbp-standard.html" target="_blank" rel="noopener noreferrer">AWS FSBP (AWS Foundational Security Best Practices standard)</a>.</p>
<p>Depending on your operational situation, removing the job itself is therefore also an option.</p>
<p>Depending on how you manage your workflows, update through one of the following methods. If the workflow does not appear in your workflow list, no update is needed.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="updating-with-shishoctl">Updating with shishoctl<a href="https://shisho.dev/docs/r/202608-rds-vpcless-aurora#updating-with-shishoctl" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>If you have workflow definitions obtained with <code>shishoctl workflow export</code>, replace the files corresponding to the <code>instance-vpc</code> job (the Rego policy, the GraphQL query, and the test) with the latest contents, and apply them to your organization with <code>shishoctl workflow apply</code>.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="editing-in-the-console">Editing in the Console<a href="https://shisho.dev/docs/r/202608-rds-vpcless-aurora#editing-in-the-console" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>Open "Prebundle: Review AWS RDS posture (FSBP)" from <strong>Workflows</strong>, find the job with <code>id: instance-vpc</code> under <code>jobs</code> in the manifest, and replace the contents of <code>rego:</code> in the <code>decide</code> block (the Rego policy) and <code>schema:</code> under <code>input</code> (the GraphQL query) with the published versions, then save.</p>
<p>No changes to other jobs or parameters are needed.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="managing-workflows-in-a-github-or-gitlab-repository">Managing Workflows in a GitHub or GitLab Repository<a href="https://shisho.dev/docs/r/202608-rds-vpcless-aurora#managing-workflows-in-a-github-or-gitlab-repository" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>Replace the three files corresponding to the <code>instance-vpc</code> job (the Rego policy, the GraphQL query, and the test) with the latest contents and push to your main branch.</p>
<p>Your deployment workflow, such as a configured GitHub Actions workflow, applies the changes to Shisho Cloud automatically.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="contact">Contact<a href="https://shisho.dev/docs/r/202608-rds-vpcless-aurora#contact" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>If you have any questions or concerns about the update, please contact our support desk.</p>
<p>We will assist you according to your situation.</p>]]></content>
        <author>
            <name>Yoshiaki Matsutomo</name>
            <uri>https://github.com/y-matsutomo</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi AI Penetration Testing Availability Expanded Further]]></title>
        <id>https://shisho.dev/docs/r/202608-takumi-pentest-update</id>
        <link href="https://shisho.dev/docs/r/202608-takumi-pentest-update"/>
        <updated>2026-08-07T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[We are widening access for customers who pre-registered, and we have improved how accurately Takumi finds the paths that lead to a given objective, along with the safeguards that keep tests within bounds.]]></summary>
        <content type="html"><![CDATA[<p>We are rolling out <strong>AI Penetration Testing</strong> to pre-registered customers more broadly than before.</p>
<p>We have also improved how accurately Takumi finds the paths that lead to a given objective, along with the safeguards that keep a test running safely.</p>
<p><img decoding="async" loading="lazy" alt="Takumi AI Penetration Testing Availability Expanded Further" src="https://shisho.dev/docs/assets/images/eyecatch-d4b765822033cf566cc0b16c5879e132.png" width="2400" height="1260" class="img_aV4l"></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="expanding-availability">Expanding Availability<a href="https://shisho.dev/docs/r/202608-takumi-pentest-update#expanding-availability" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>We have been introducing AI penetration testing to pre-registered customers in stages. Having accumulated operational experience, and having strengthened the safeguards that keep tests running safely, we are now widening that rollout further.</p>
<p>We continue to onboard pre-registered customers in order, so if you'd like to use the feature, start by registering from the <a href="https://flatt.tech/takumi/features/pentesting" target="_blank" rel="noopener noreferrer">application page</a>.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="improvements">Improvements<a href="https://shisho.dev/docs/r/202608-takumi-pentest-update#improvements" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Since our last announcement, we have made three improvements to exploration accuracy and to the safeguards that keep tests running safely.</p>
<ul>
<li><strong>Engine performance</strong>: Takumi is more accurate across the chain of judgments it makes — forming hypotheses from reconnaissance, chaining vulnerabilities, and turning each foothold into the next attack</li>
<li><strong>Destructive operation policies</strong>: You can now define in advance how far Takumi may go with operations that could affect the target system, such as deleting or modifying data</li>
<li><strong>Stronger scope control and monitoring</strong>: We have strengthened both the controls that keep exploration from reaching outside the configured scope and the detective controls that surface access to out-of-scope targets and other risky operations</li>
</ul>
<h2 class="anchor anchorWithStickyNavbar_k394" id="customer-feedback">Customer Feedback<a href="https://shisho.dev/docs/r/202608-takumi-pentest-update#customer-feedback" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>宮﨑 多朗様 (ウェルスナビ株式会社 システム基盤グループ/セキュリティエンジニア) shared the following feedback with us.</p>
<blockquote>
<p>これまでペネトレーションテストは専門会社に依頼するとコストが高くなる傾向があり、数百万円〜の費用に加え、シナリオの相談からレポート受領まで2ヶ月以上を要することもめずらしくありません。予算の確保や社内調整、さらに診断員のスケジュール調整にも時間がかかるため、私たちとしてもフットワーク軽く回すことが難しいという課題がありました。</p>
<p>Takumi の AIペネトレーションテスト機能では、従来であれば100万円を超える規模を見込むようなペネトレーションテストが、今回は数千円・数時間という圧倒的なコストとスピードで完了しました。専門会社の診断員のスケジュールに左右されず、必要なタイミングで自分たちの判断ですぐに実施できる点も大きな魅力です。事業会社が抱えるセキュリティエンジニアの数は必ずしも多くない組織もあるなかで、こうした調整ごとにかかる工数を短縮してくれるため、専門的な知識を持つメンバーはシナリオの設計・調整といった本質的な部分に注力できるようになりました。手軽に回せるだけでも十分な価値ですが、机上の評価では正直「刺さらないだろう」と考えていた箇所にミスコンフィギュレーションが見つかり、実際のリスクとして検知してくれた点には驚かされました。手軽さだけでなく成果の面でもしっかり応えてくれるため、私たちとしても今後、Web 経由のペネトレーションテストを積極的に活用していきたいと考えています。</p>
</blockquote>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202608-takumi-pentest-update#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>AI penetration testing is currently expanding its availability in stages.</p>
<div class="theme-admonition theme-admonition-info admonition_ODxW alert alert--info"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 14 16"><path fill-rule="evenodd" d="M7 2.3c3.14 0 5.7 2.56 5.7 5.7s-2.56 5.7-5.7 5.7A5.71 5.71 0 0 1 1.3 8c0-3.14 2.56-5.7 5.7-5.7zM7 1C3.14 1 0 4.14 0 8s3.14 7 7 7 7-3.14 7-7-3.14-7-7-7zm1 3H6v5h2V4zm0 6H6v2h2v-2z"></path></svg></span>info</div><div class="admonitionContent_Kqb4"><p>If you'd like to use it, register from the <a href="https://flatt.tech/takumi/features/pentesting" target="_blank" rel="noopener noreferrer">application page</a> and our team will get in touch.</p></div></div>
<p>▼ User Guide: <a href="https://shisho.dev/docs/t/assessment/features/pentest">Penetration Testing</a></p>]]></content>
        <author>
            <name>Tsubasa Umeuchi</name>
            <uri>https://github.com/Szarny</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Bot Trust Conditions Now Support Custom OIDC Providers]]></title>
        <id>https://shisho.dev/docs/r/202608-bot-custom-oidc</id>
        <link href="https://shisho.dev/docs/r/202608-bot-custom-oidc"/>
        <updated>2026-08-02T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[A bot can now federate with any OIDC-Discovery-compliant identity provider, not just GitHub Actions and GitLab CI.]]></summary>
        <content type="html"><![CDATA[<p>Bot trust conditions now accept ID tokens from <strong>any identity provider that complies with OIDC Discovery</strong>, not just GitHub Actions and GitLab CI.</p>
<p>Self-hosted CI/CD systems such as Jenkins, Buildkite, and CircleCI, another cloud's workload identity federation, GitHub Enterprise Server, and self-managed GitLab can all sign in as a bot without a static API key.</p>
<div class="theme-admonition theme-admonition-info admonition_ODxW alert alert--info"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 14 16"><path fill-rule="evenodd" d="M7 2.3c3.14 0 5.7 2.56 5.7 5.7s-2.56 5.7-5.7 5.7A5.71 5.71 0 0 1 1.3 8c0-3.14 2.56-5.7 5.7-5.7zM7 1C3.14 1 0 4.14 0 8s3.14 7 7 7 7-3.14 7-7-3.14-7-7-7zm1 3H6v5h2V4zm0 6H6v2h2v-2z"></path></svg></span>info</div><div class="admonitionContent_Kqb4"><p>Custom OIDC provider support is currently in beta.
Specifications and behavior may change without prior notice.</p></div></div>
<h2 class="anchor anchorWithStickyNavbar_k394" id="overview">Overview<a href="https://shisho.dev/docs/r/202608-bot-custom-oidc#overview" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>A trust condition is a rule, configured on a bot, that decides which OIDC ID tokens Shisho Cloud accepts as proof that the caller may sign in as that bot. Until now it understood two issuers, GitHub Actions and GitLab CI, so every other environment had to fall back on a bot API key - a static secret you have to store, rotate, and keep out of your logs.</p>
<p>The new <strong>Custom (OIDC)</strong> provider lets you point a trust condition at your own issuer instead. Your identity provider mints a short-lived ID token for each job, Shisho Cloud verifies it against the condition, and exchanges it for equally short-lived credentials scoped to that bot. Nothing persistent has to live on the CI side.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202608-bot-custom-oidc#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Open a bot's <strong>Trust Conditions</strong> tab in the Shisho Cloud console, add a trust condition, and select <strong>Custom (OIDC)</strong> as its provider. The condition takes three required inputs, plus an optional one.</p>
<ul>
<li><strong>Issuer</strong> - the <code>https://</code> URL of the ID token's issuer. It must be reachable on port 443 and serve an OIDC Discovery document at <code>/.well-known/openid-configuration</code>.</li>
<li><strong>Subject</strong> - the expected value of the ID token's <code>sub</code> claim, either an exact string or an expression in which <code>*</code> matches any sequence of characters, such as <code>repo:acme/app:*</code>. A subject of just <code>*</code> is rejected.</li>
<li><strong>Audience</strong> - the value the ID token's <code>aud</code> claim must contain. We recommend configuring your provider to issue <code>https://sts.cloud.shisho.dev</code>, so a token minted for Shisho Cloud can't be replayed against another relying party.</li>
<li><strong>Claims</strong> (optional) - up to 10 additional conditions on other top-level string claims of the token, each matched the same way as Subject.</li>
</ul>
<p>Once the condition is saved, the CI-side flow is the same as for GitHub Actions or GitLab CI. Obtain an ID token from your provider, then pass it to <code>shishoctl auth signin:bot</code>.</p>
<div class="theme-admonition theme-admonition-info admonition_ODxW alert alert--info"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 14 16"><path fill-rule="evenodd" d="M7 2.3c3.14 0 5.7 2.56 5.7 5.7s-2.56 5.7-5.7 5.7A5.71 5.71 0 0 1 1.3 8c0-3.14 2.56-5.7 5.7-5.7zM7 1C3.14 1 0 4.14 0 8s3.14 7 7 7 7-3.14 7-7-3.14-7-7-7zm1 3H6v5h2V4zm0 6H6v2h2v-2z"></path></svg></span>Limit</div><div class="admonitionContent_Kqb4"><p>An organization can have <strong>one</strong> custom OIDC trust condition in total, across all of its bots. GitHub Actions and GitLab CI trust conditions are not limited.</p><p>If you need more than one, contact support - whether we can accommodate the request depends on your plan.</p></div></div>
<p>For the full field reference, an example configuration, and security guidance, see <a href="https://shisho.dev/docs/c/bot/authentication#custom-oidc">Custom OIDC</a> in the bot authentication guide.</p>]]></content>
        <author>
            <name>Takashi Yoneuchi</name>
            <uri>https://github.com/lmt-swallow</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi Blackbox Assessment Now Supports UI-less APIs]]></title>
        <id>https://shisho.dev/docs/r/202607-takumi-bb-ui-less</id>
        <link href="https://shisho.dev/docs/r/202607-takumi-bb-ui-less"/>
        <updated>2026-07-28T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[APIs that have no web UI can now be crawled and assessed.]]></summary>
        <content type="html"><![CDATA[<p>In Takumi blackbox assessments, <strong>APIs that have no web UI</strong> can now be specified as an assessment target.</p>
<p>Instead of crawling with a web browser, Takumi extracts the endpoints to assess from the attached schema files, such as an OpenAPI specification or a GraphQL schema.</p>
<p><img decoding="async" loading="lazy" alt="Configuration UI" src="https://shisho.dev/docs/assets/images/api-setting-6513396274997ee414bcb6ab19bc3e55.png" width="1909" height="1048" class="img_aV4l"></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="overview">Overview<a href="https://shisho.dev/docs/r/202607-takumi-bb-ui-less#overview" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Blackbox assessments have relied on crawling a web browser to discover the endpoints to assess. This works well for applications operated through a browser, but not for APIs that serve no screen — there is nothing to crawl, so they could not be assessed. Many real-world targets, however, are API-only, such as backends for mobile apps and service-to-service APIs.</p>
<p>With this release, Takumi can assess those UI-less APIs directly. When you select API as the target type, Takumi does not crawl; it extracts the endpoints from the attached schema files instead.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202607-takumi-bb-ui-less#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>This feature is available to all organizations from the blackbox assessment dispatch screen.</p>
<p>For how to configure the schema files and authentication steps, see <a href="https://shisho.dev/docs/t/assessment/features/blackbox-assessment#api-assessment">Assessing an API</a>.</p>]]></content>
        <author>
            <name>Tsubasa Umeuchi</name>
            <uri>https://github.com/Szarny</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi AI Penetration Testing Availability Expanded]]></title>
        <id>https://shisho.dev/docs/r/202607-takumi-pentest</id>
        <link href="https://shisho.dev/docs/r/202607-takumi-pentest"/>
        <updated>2026-07-16T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[Set a target and an objective, and Takumi autonomously explores attack paths to verify whether that objective is reachable.]]></summary>
        <content type="html"><![CDATA[<p>We are expanding access to <strong>AI Penetration Testing</strong>, which we began rolling out on June 15, 2026, to more customers. The feature verifies whether a given objective is achievable, from the perspective of a real attacker.</p>
<p>Set a target and a concrete objective — such as <strong>accessing user data</strong> — and Takumi autonomously chains reconnaissance, vulnerability discovery, and exploitation.</p>
<p>The feature is not yet available to all customers, so if you'd like to use it, register from the <a href="https://flatt.tech/takumi/features/pentesting" target="_blank" rel="noopener noreferrer">application page</a>.</p>
<p><img decoding="async" loading="lazy" alt="AI Penetration Testing Availability Expanded" src="https://shisho.dev/docs/assets/images/eyecatch-c5e5073d71fa3ecf1e222969c6f856cd.png" width="2400" height="1260" class="img_aV4l"></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="background">Background<a href="https://shisho.dev/docs/r/202607-takumi-pentest#background" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Whitebox and blackbox assessments comprehensively detect vulnerabilities across an entire application using a feature-and-perspective matrix. In real-world operations, however, you often want to answer more than "what vulnerabilities exist" — you want to know whether an attacker could actually reach a specific objective in this environment. Individually minor weaknesses frequently chain together into a serious outcome, such as data exfiltration or a full system compromise.</p>
<p>AI penetration testing answers that question. Rather than enumerating every vulnerability, it focuses on whether a single defined objective is reachable, and Takumi autonomously explores the attack paths that lead to it. Much like a human penetration tester, it forms hypotheses from what it learns during reconnaissance, discovers and chains vulnerabilities, and turns each foothold into the next attack.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="how-it-works">How It Works<a href="https://shisho.dev/docs/r/202607-takumi-pentest#how-it-works" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>You start a run by configuring a target and an objective. Pick an objective from presets such as "accessing user data" or "gaining system access," and Takumi handles everything from reconnaissance to exploitation. Unlike a standard assessment, it doesn't just report vulnerabilities individually — it verifies how those vulnerabilities can be leveraged to actually reach the objective.</p>
<p>While a test runs and after it completes, you can follow a timeline of what the attack has reached and an intrusion map that visualizes the discovered attack paths. When the test finishes, Takumi produces a report of the operations it performed and whether the objective was achieved. Even if the objective was not reached, you can review the report, add further instructions, and resume the test from where it left off.</p>
<p><img decoding="async" loading="lazy" alt="Progress" src="https://shisho.dev/docs/assets/images/progress-d2d49f3adb34d5281b8d115393428919.png" width="2552" height="3024" class="img_aV4l"></p>
<p>For more detailed configuration and usage, see the user guide.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202607-takumi-pentest#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>AI penetration testing is currently expanding its availability in stages.</p>
<div class="theme-admonition theme-admonition-info admonition_ODxW alert alert--info"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 14 16"><path fill-rule="evenodd" d="M7 2.3c3.14 0 5.7 2.56 5.7 5.7s-2.56 5.7-5.7 5.7A5.71 5.71 0 0 1 1.3 8c0-3.14 2.56-5.7 5.7-5.7zM7 1C3.14 1 0 4.14 0 8s3.14 7 7 7 7-3.14 7-7-3.14-7-7-7zm1 3H6v5h2V4zm0 6H6v2h2v-2z"></path></svg></span>info</div><div class="admonitionContent_Kqb4"><p>If you'd like to use it, register from the <a href="https://flatt.tech/takumi/features/pentesting" target="_blank" rel="noopener noreferrer">application page</a> and our team will get in touch.</p></div></div>
<p>▼ User Guide: <a href="https://shisho.dev/docs/t/assessment/features/pentest">Penetration Testing</a></p>]]></content>
        <author>
            <name>Tsubasa Umeuchi</name>
            <uri>https://github.com/Szarny</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi Images Beta Released]]></title>
        <id>https://shisho.dev/docs/r/202607-takumi-images-beta</id>
        <link href="https://shisho.dev/docs/r/202607-takumi-images-beta"/>
        <updated>2026-07-08T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[Takumi Images provides maintained container images designed to keep known vulnerabilities out of your base images with minimal migration work.]]></summary>
        <content type="html"><![CDATA[<p>Takumi Images is now available in beta. It provides maintained container images that are continuously rebuilt and scanned so your applications can start from base images where known vulnerabilities have already been addressed.</p>
<p>The images are published through the OCI registry <code>images.flatt.tech</code>.</p>
<p><img decoding="async" loading="lazy" alt="Takumi Images" src="https://shisho.dev/docs/assets/images/og-image-4fde64cea7f90dde20dcff1f306f513f.jpg" width="1200" height="630" class="img_aV4l"></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="overview">Overview<a href="https://shisho.dev/docs/r/202607-takumi-images-beta#overview" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Development teams are being asked to apply security updates more frequently, while software supply chain attacks increasingly target the update process itself. Takumi Images is designed to reduce that operational tension: you can move to maintained base images without rebuilding your own patch pipeline for common runtime images.</p>
<p>When a corresponding image is available in the catalog, you can switch the base image reference and pull the latest Takumi image when updates are published, instead of investigating base-image packages, selecting patched dependency versions, and rebuilding those images yourself.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202607-takumi-images-beta#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>When the catalog includes a Takumi image that corresponds to your current base image, migration usually only requires changing the <code>FROM</code> line in your Dockerfile:</p>
<div class="language-diff codeBlockContainer_tXdS theme-code-block" style="--prism-color:#393A34;--prism-background-color:#f6f8fa"><div class="codeBlockContent_zXtR"><pre tabindex="0" class="prism-code language-diff codeBlock_qqWd thin-scrollbar" style="color:#393A34;background-color:#f6f8fa"><code class="codeBlockLines_CmGJ"><span class="token-line" style="color:#393A34"><span class="token plain">- FROM node:latest</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">+ FROM images.flatt.tech/takumi/node:latest</span><br></span></code></pre><div class="buttonGroup_yRlK"><button type="button" aria-label="Copy code to clipboard" title="Copy" class="clean-btn"><span class="copyButtonIcons_yBV4" aria-hidden="true"><svg viewBox="0 0 24 24" class="copyButtonIcon_Ctry"><path fill="currentColor" d="M19,21H8V7H19M19,5H8A2,2 0 0,0 6,7V21A2,2 0 0,0 8,23H19A2,2 0 0,0 21,21V7A2,2 0 0,0 19,5M16,1H4A2,2 0 0,0 2,3V17H4V3H16V1Z"></path></svg><svg viewBox="0 0 24 24" class="copyButtonSuccessIcon_FUe1"><path fill="currentColor" d="M21,7L9,19L3.5,13.5L4.91,12.09L9,16.17L19.59,5.59L21,7Z"></path></svg></span></button></div></div></div>
<p>After migration, pull the image again to receive the latest rebuilt image:</p>
<div class="language-bash codeBlockContainer_tXdS theme-code-block" style="--prism-color:#393A34;--prism-background-color:#f6f8fa"><div class="codeBlockContent_zXtR"><pre tabindex="0" class="prism-code language-bash codeBlock_qqWd thin-scrollbar" style="color:#393A34;background-color:#f6f8fa"><code class="codeBlockLines_CmGJ"><span class="token-line" style="color:#393A34"><span class="token function" style="color:#d73a49">docker</span><span class="token plain"> pull images.flatt.tech/takumi/node:latest</span><br></span></code></pre><div class="buttonGroup_yRlK"><button type="button" aria-label="Copy code to clipboard" title="Copy" class="clean-btn"><span class="copyButtonIcons_yBV4" aria-hidden="true"><svg viewBox="0 0 24 24" class="copyButtonIcon_Ctry"><path fill="currentColor" d="M19,21H8V7H19M19,5H8A2,2 0 0,0 6,7V21A2,2 0 0,0 8,23H19A2,2 0 0,0 21,21V7A2,2 0 0,0 19,5M16,1H4A2,2 0 0,0 2,3V17H4V3H16V1Z"></path></svg><svg viewBox="0 0 24 24" class="copyButtonSuccessIcon_FUe1"><path fill="currentColor" d="M21,7L9,19L3.5,13.5L4.91,12.09L9,16.17L19.59,5.59L21,7Z"></path></svg></span></button></div></div></div>
<p>For details, see the <a href="https://shisho.dev/docs/t/images/" target="_blank" rel="noopener noreferrer">Takumi Images documentation</a>.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="included-value">Included Value<a href="https://shisho.dev/docs/r/202607-takumi-images-beta#included-value" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Takumi Images makes base-image maintenance easier in three ways.</p>
<p>First, each image contains less by default. Takumi Images focuses on the main program and the minimum runtime libraries required to run it. This helps reduce scanner noise from dependencies that are inherited from the base image rather than from your application code.</p>
<p>Second, the provider handles the base-image side of the investigation. For software included in Takumi Images, the provider triages vulnerability impact and also checks upstream code for malware before incorporating updates. This reduces the amount of base-image findings and update-source risk that users have to track themselves.</p>
<p>Third, each image is published with verifiable supply chain metadata:</p>
<ul>
<li>Signed image artifacts</li>
<li>SBOM attestations</li>
<li>SLSA Provenance attestations</li>
<li>VEX attestations for vulnerability findings assessed by the provider</li>
</ul>
<p>These attestations let you inspect what is in the image, where it came from, and the current assessment for findings reported against the base image.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="roadmap">Roadmap<a href="https://shisho.dev/docs/r/202607-takumi-images-beta#roadmap" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>We plan to expand the image catalog further, focusing on databases, language runtimes, and middleware, and to provide image variants that address compliance requirements.</p>
<p>We also plan to detect vulnerability information before CVE IDs are assigned, incorporate those fixes early through nightly builds, and support international compliance requirements.</p>]]></content>
        <author>
            <name>Takashi Yoneuchi</name>
            <uri>https://github.com/lmt-swallow</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi Runner Trace Search Released]]></title>
        <id>https://shisho.dev/docs/r/202606-takumi-runner-trace-search</id>
        <link href="https://shisho.dev/docs/r/202606-takumi-runner-trace-search"/>
        <updated>2026-06-30T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[You can now search your organization's collected Takumi Runner trace data by date range.]]></summary>
        <content type="html"><![CDATA[<p>Takumi Runner now lets you search the trace data it has collected over a date range you specify. Previously you could only search the trace data of a single job, but with this search feature you can detect suspicious activity across every job within a given period.</p>
<p>This page also walks through how to use the search feature with real-world examples, such as the axios supply chain attack in March 2026. See <strong>Examples</strong> below.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202606-takumi-runner-trace-search#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>In the Shisho Cloud console, open <strong>Runner</strong> &gt; <strong>Trace Search</strong>.</p>
<p>First, choose a date range and select the event types you want to search. Enter your search criteria and click <strong>Search</strong> to start the search.</p>
<p><img decoding="async" loading="lazy" alt="Trace search page" src="https://shisho.dev/docs/assets/images/search-page-dd3b7e8e21028258c3959b5e5e5eb159.png" width="2662" height="1652" class="img_aV4l"></p>
<div class="theme-admonition theme-admonition-warning admonition_ODxW alert alert--warning"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 16 16"><path fill-rule="evenodd" d="M8.893 1.5c-.183-.31-.52-.5-.887-.5s-.703.19-.886.5L.138 13.499a.98.98 0 0 0 0 1.001c.193.31.53.501.886.501h13.964c.367 0 .704-.19.877-.5a1.03 1.03 0 0 0 .01-1.002L8.893 1.5zm.133 11.497H6.987v-2.003h2.039v2.003zm0-3.004H6.987V5.987h2.039v4.006z"></path></svg></span>warning</div><div class="admonitionContent_Kqb4"><p>Trace data before 2026-06-13 cannot be searched.</p></div></div>
<p>Once the search completes, you can review the search results. From this screen you can:</p>
<ul>
<li>Review statistics for the matched jobs and events</li>
<li>Inspect the matched jobs and events in detail</li>
<li>Download the search result data</li>
</ul>
<p><img decoding="async" loading="lazy" alt="Search results page" src="https://shisho.dev/docs/assets/images/results-page-f60887104370d8c0fc20b3d2ac58a145.png" width="2664" height="1652" class="img_aV4l"></p>
<p>Search results are retained for 72 hours.</p>
<p>For details, see the <a href="https://shisho.dev/docs/t/runner/features/trace-search">trace search documentation</a>.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="examples">Examples<a href="https://shisho.dev/docs/r/202606-takumi-runner-trace-search#examples" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<h3 class="anchor anchorWithStickyNavbar_k394" id="axios-supply-chain-attack---hostname-search">Axios supply chain attack - hostname search<a href="https://shisho.dev/docs/r/202606-takumi-runner-trace-search#axios-supply-chain-attack---hostname-search" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>In March 2026, the npm package for the HTTP client library axios was compromised in a supply chain attack. For details on this incident, see our <a href="https://blog.flatt.tech/entry/axios_compromise" target="_blank" rel="noopener noreferrer">blog post</a>.</p>
<p>Suppose an equivalent attack occurred three days ago. Based on our blog post and similar reports, the malware connects to <code>dangerous.example</code> (this page uses a fictional hostname that differs from the real one cited in the blog post).</p>
<p>Use the following search criteria to check whether any jobs executed by Takumi Runner were affected:</p>
<ul>
<li><strong>Date range</strong> - <code>&lt;3 days ago&gt; ~ &lt;day of search&gt;</code></li>
<li><strong>Event type</strong> - <code>dns_query</code></li>
<li><strong>Hostname</strong> - <code>*dangerous.example</code></li>
</ul>
<p><img decoding="async" loading="lazy" alt="Hostname search" src="https://shisho.dev/docs/assets/images/hostname-search-692d19125db9d8383cf9ba5f7d43224a.png" width="2010" height="1286" class="img_aV4l"></p>
<p>Add <code>*</code> at the beginning of the hostname so subdomains also match.</p>
<p>Run the search. If any jobs match, you can conclude they were affected by the attack.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="github-actions-compromise---file-access-search">GitHub Actions compromise - file access search<a href="https://shisho.dev/docs/r/202606-takumi-runner-trace-search#github-actions-compromise---file-access-search" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>Attacks that compromise GitHub Actions and steal credentials have already occurred several times this year. For details, see our <a href="https://blog.flatt.tech/entry/2026-github-actions-security-part1" target="_blank" rel="noopener noreferrer">blog post</a>.</p>
<p>Now suppose a similar GitHub Actions compromise occurred. Based on the blog post above, a typical pattern is reading credentials from process memory at <code>/proc/&lt;pid&gt;/mem</code>. If your jobs were affected, Takumi Runner retains trace data showing file access to <code>/proc/&lt;pid&gt;/mem</code>.</p>
<p>You can check for impact with the following search criteria:</p>
<ul>
<li><strong>Date range</strong> - <code>&lt;attack date&gt; ~ &lt;day of search&gt;</code></li>
<li><strong>Event type</strong> - <code>file_open</code></li>
<li><strong>File path</strong> - <code>/proc/*/mem</code></li>
</ul>
<p><img decoding="async" loading="lazy" alt="File access search" src="https://shisho.dev/docs/assets/images/fileopen-search-64c9a982905686501fb909f73adab920.png" width="2252" height="1422" class="img_aV4l"></p>
<p>Since <code>&lt;pid&gt;</code> is not fixed, use <code>*</code> in the search.</p>
<p>Run the search. If any jobs match, you can conclude they were affected by the attack.</p>]]></content>
        <author>
            <name>Rio Nishimori</name>
            <uri>https://github.com/rio828</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi Guard: Redesigned Log Browser]]></title>
        <id>https://shisho.dev/docs/r/202606-takumi-guard-log-browser</id>
        <link href="https://shisho.dev/docs/r/202606-takumi-guard-log-browser"/>
        <updated>2026-06-26T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[Investigate package installations across your whole organization from one screen — search, browse, group, and share.]]></summary>
        <content type="html"><![CDATA[<p>The Takumi Guard log viewer has been rebuilt as a single, unified <strong>Log Browser</strong> that replaces the previous log search page. Search a package, browse recent activity across your organization, group installs by repository, workflow, or user, and share a link to exactly what you are looking at.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="overview">Overview<a href="https://shisho.dev/docs/r/202606-takumi-guard-log-browser#overview" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Previously, viewing installation logs meant searching one package at a time. The new Log Browser keeps that search and adds organization-wide browsing and breakdowns in the same screen, so you can move from "did anyone install this package?" to "what is this repository pulling?" without switching pages.</p>
<p>It replaces the previous per-package log page — the package search you used before is now one mode within the browser.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202606-takumi-guard-log-browser#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Navigate to <strong>Guard</strong> &gt; <strong>Logs</strong> in the Shisho Cloud console. Choose your ecosystem (npm, PyPI, RubyGems, and others), then either search a package or browse recent activity.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="key-capabilities">Key Capabilities<a href="https://shisho.dev/docs/r/202606-takumi-guard-log-browser#key-capabilities" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<h3 class="anchor anchorWithStickyNavbar_k394" id="one-screen-for-search-and-browse">One screen for search and browse<a href="https://shisho.dev/docs/r/202606-takumi-guard-log-browser#one-screen-for-search-and-browse" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>Search a specific package to see every installation — who installed it, from which repository and workflow, and when — or browse all installation events across your organization from the same place.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="group-by-repository-workflow-or-user">Group by repository, workflow, or user<a href="https://shisho.dev/docs/r/202606-takumi-guard-log-browser#group-by-repository-workflow-or-user" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>Switch between a flat events feed and breakdowns grouped by package, repository, workflow, or user, each with download and blocked counts. Selecting any entity filters the view down to it, which is the quickest way to narrow an investigation.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="one-time-range-applied-everywhere">One time range, applied everywhere<a href="https://shisho.dev/docs/r/202606-takumi-guard-log-browser#one-time-range-applied-everywhere" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>A single range — 24 hours, 7 days, 14 days, or a custom range up to 14 days — scopes the summary, the events feed, and the breakdowns together, so every number on screen covers the same window. You can also filter to blocked installations only.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="always-know-what-you-are-looking-at-and-share-it">Always know what you are looking at, and share it<a href="https://shisho.dev/docs/r/202606-takumi-guard-log-browser#always-know-what-you-are-looking-at-and-share-it" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>A summary bar above the results states the active ecosystem, time range, and filters, and lets you clear each one. The current view is captured in the page URL, so you can send a teammate a link that reproduces the exact evidence on screen.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="notes">Notes<a href="https://shisho.dev/docs/r/202606-takumi-guard-log-browser#notes" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Installation logs remain searchable for <strong>14 days</strong>, and data is updated approximately every 15 minutes. Log queries are subject to a per-organization fair-use limit — 60 requests per minute and 5,000 per day — to keep the browser responsive for everyone. For full details, see the <a href="https://shisho.dev/docs/t/guard/features/installation-logs">Package Installation Logs</a> guide.</p>]]></content>
        <author>
            <name>Deividas Turskis</name>
            <uri>https://github.com/ren-</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi Guard: Admin Deployment Now Provisions Packagist]]></title>
        <id>https://shisho.dev/docs/r/202606-takumi-guard-admin-deployment-packagist</id>
        <link href="https://shisho.dev/docs/r/202606-takumi-guard-admin-deployment-packagist"/>
        <updated>2026-06-16T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[Takumi Guard admin deployment now configures Packagist on every target machine, alongside npm, PyPI, RubyGems, and Go modules.]]></summary>
        <content type="html"><![CDATA[<p>Takumi Guard <a href="https://shisho.dev/docs/t/guard/features/admin-deployment">admin deployment</a> now configures Packagist — the PHP/Composer ecosystem — on every target machine, alongside npm, PyPI, RubyGems, and Go modules.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="overview">Overview<a href="https://shisho.dev/docs/r/202606-takumi-guard-admin-deployment-packagist#overview" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p><a href="https://shisho.dev/docs/t/guard/features/admin-deployment">Admin deployment</a> lets administrators roll Takumi Guard out across their fleet without any per-developer steps: the setup script is distributed through your management tool (Jamf, Intune, Ansible, and so on) and silently configures every supported package manager on each device. That list covered npm, PyPI, RubyGems, and Go modules; Packagist now joins it as the fifth ecosystem, so PHP projects get the same protection as the rest, with nothing for individual developers to do.</p>
<p>On each device the setup script registers Takumi Guard as a Composer repository and disables the public Packagist (packagist.org), so <code>composer install</code> and <code>composer update</code> resolve through Takumi Guard and known-malicious packages are blocked before they are fetched. It configures Composer via the official <code>composer config</code> command when <code>composer</code> is on PATH, and writes the config files directly otherwise — so protection still lands in MDM contexts where the CLI is not reachable.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202606-takumi-guard-admin-deployment-packagist#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Setup script <strong>v0.10.0</strong> is available from:</p>
<ul>
<li><strong>macOS / Linux:</strong> <a href="https://shisho.dev/releases/takumi-guard-setup-0.10.0.sh" target="_blank" rel="noopener noreferrer">https://shisho.dev/releases/takumi-guard-setup-0.10.0.sh</a></li>
<li><strong>Windows:</strong> <a href="https://shisho.dev/releases/takumi-guard-setup-0.10.0.ps1" target="_blank" rel="noopener noreferrer">https://shisho.dev/releases/takumi-guard-setup-0.10.0.ps1</a></li>
</ul>
<p>Steps (if you already have a Bot and API key, skip to step 3):</p>
<ol>
<li>Create a Bot in the Shisho Cloud console (<strong>Settings</strong> &gt; <strong>Bots</strong>) and assign the "Takumi Guard Token Issuer" role</li>
<li>Generate an API key for the Bot</li>
<li>Download the setup script v0.10.0 from the URL above</li>
<li>Wrap the script with your management tool (Jamf, Intune, Ansible, etc.) and deploy</li>
</ol>
<p>All of npm, PyPI, RubyGems, Go modules, and Packagist are configured by default; pass <code>packagist</code> as the scope argument to target it alone. For detailed instructions and the latest wrapper examples, see the <a href="https://shisho.dev/docs/t/guard/features/admin-deployment">Admin Deployment guide</a>.</p>
<p>Developers configuring Composer on their own machine or in CI can follow the <a href="https://shisho.dev/docs/t/guard/quickstart/packagist">Packagist quickstart</a> instead.</p>
<div class="theme-admonition theme-admonition-warning admonition_ODxW alert alert--warning"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 16 16"><path fill-rule="evenodd" d="M8.893 1.5c-.183-.31-.52-.5-.887-.5s-.703.19-.886.5L.138 13.499a.98.98 0 0 0 0 1.001c.193.31.53.501.886.501h13.964c.367 0 .704-.19.877-.5a1.03 1.03 0 0 0 .01-1.002L8.893 1.5zm.133 11.497H6.987v-2.003h2.039v2.003zm0-3.004H6.987V5.987h2.039v4.006z"></path></svg></span>If you already use admin deployment</div><div class="admonitionContent_Kqb4"><p>The sample wrapper script we provide may have been revised. Update both the wrapper and the setup script to the latest versions as needed.</p></div></div>
<div class="theme-admonition theme-admonition-info admonition_ODxW alert alert--info"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 14 16"><path fill-rule="evenodd" d="M7 2.3c3.14 0 5.7 2.56 5.7 5.7s-2.56 5.7-5.7 5.7A5.71 5.71 0 0 1 1.3 8c0-3.14 2.56-5.7 5.7-5.7zM7 1C3.14 1 0 4.14 0 8s3.14 7 7 7 7-3.14 7-7-3.14-7-7-7zm1 3H6v5h2V4zm0 6H6v2h2v-2z"></path></svg></span>Paid Feature</div><div class="admonitionContent_Kqb4"><p>This feature requires an active Takumi subscription with Guard enabled. See <a href="https://shisho.dev/docs/t/guard/billing">Pricing &amp; Billing</a> for details.</p></div></div>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started-with-your-organization">Getting Started with Your Organization<a href="https://shisho.dev/docs/r/202606-takumi-guard-admin-deployment-packagist#getting-started-with-your-organization" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>To use Guard's organization features (admin deployment, installation log search, etc.), you need a Takumi subscription with Guard enabled.</p>
<ol>
<li>Go to <a href="https://cloud.shisho.dev/hello/takumi" target="_blank" rel="noopener noreferrer">https://cloud.shisho.dev/hello/takumi</a> and sign in</li>
<li>Register your organization and subscribe to Takumi</li>
<li>Navigate to <strong>Guard</strong> &gt; <strong>Settings</strong> from the sidebar</li>
<li>Click "Enable" to activate Guard</li>
</ol>
<p><img decoding="async" loading="lazy" alt="Guard settings page" src="https://shisho.dev/docs/assets/images/ui-guard-settings-6b26b5c78a1bd5b0b3ed5c3e029208e6.png" width="1001" height="373" class="img_aV4l"></p>
<p>Once Guard is enabled, follow the <a href="https://shisho.dev/docs/t/guard/features/admin-deployment">Admin Deployment guide</a> to begin setup.</p>]]></content>
        <author>
            <name>Yoshiaki Matsutomo</name>
            <uri>https://github.com/y-matsutomo</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi Guard Setup Script Healthcheck Subcommand Released]]></title>
        <id>https://shisho.dev/docs/r/202606-takumi-guard-healthcheck</id>
        <link href="https://shisho.dev/docs/r/202606-takumi-guard-healthcheck"/>
        <updated>2026-06-16T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[The setup script now includes a healthcheck subcommand to verify Guard is correctly configured and blocking malicious packages.]]></summary>
        <content type="html"><![CDATA[<p>Takumi Guard's setup script (<code>setup.sh</code> / <code>setup.ps1</code>) now includes a <strong><code>healthcheck</code></strong> subcommand that verifies Guard is correctly configured and actively blocking malicious packages — all without modifying any files or requiring API credentials.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="overview">Overview<a href="https://shisho.dev/docs/r/202606-takumi-guard-healthcheck#overview" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>After running <code>setup.sh install</code>, there was no automated way to confirm Guard was working end-to-end. The user guide provided manual verification steps (e.g. <code>npm install @panda-guard/test-malicious</code>), but these were easy to skip and not scriptable.</p>
<p>The <code>healthcheck</code> subcommand closes this gap. It runs a 3-phase verification for each supported ecosystem:</p>
<ol>
<li><strong>Config check</strong> — verifies the package manager is pointing to the Guard proxy</li>
<li><strong>Connectivity check</strong> — confirms the Guard proxy is reachable</li>
<li><strong>Block test</strong> — attempts to install a known-blocked test package and verifies it is rejected</li>
</ol>
<p>The subcommand is completely read-only and requires no API credentials (<code>TG_BOT_API_KEY</code> / <code>TG_BOT_ID</code> are not needed).</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202606-takumi-guard-healthcheck#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Run the healthcheck after completing <code>setup.sh install</code>:</p>
<div class="language-bash codeBlockContainer_tXdS theme-code-block" style="--prism-color:#393A34;--prism-background-color:#f6f8fa"><div class="codeBlockContent_zXtR"><pre tabindex="0" class="prism-code language-bash codeBlock_qqWd thin-scrollbar" style="color:#393A34;background-color:#f6f8fa"><code class="codeBlockLines_CmGJ"><span class="token-line" style="color:#393A34"><span class="token plain">./setup.sh healthcheck</span><br></span></code></pre><div class="buttonGroup_yRlK"><button type="button" aria-label="Copy code to clipboard" title="Copy" class="clean-btn"><span class="copyButtonIcons_yBV4" aria-hidden="true"><svg viewBox="0 0 24 24" class="copyButtonIcon_Ctry"><path fill="currentColor" d="M19,21H8V7H19M19,5H8A2,2 0 0,0 6,7V21A2,2 0 0,0 8,23H19A2,2 0 0,0 21,21V7A2,2 0 0,0 19,5M16,1H4A2,2 0 0,0 2,3V17H4V3H16V1Z"></path></svg><svg viewBox="0 0 24 24" class="copyButtonSuccessIcon_FUe1"><path fill="currentColor" d="M21,7L9,19L3.5,13.5L4.91,12.09L9,16.17L19.59,5.59L21,7Z"></path></svg></span></button></div></div></div>
<p>To check a specific ecosystem:</p>
<div class="language-bash codeBlockContainer_tXdS theme-code-block" style="--prism-color:#393A34;--prism-background-color:#f6f8fa"><div class="codeBlockContent_zXtR"><pre tabindex="0" class="prism-code language-bash codeBlock_qqWd thin-scrollbar" style="color:#393A34;background-color:#f6f8fa"><code class="codeBlockLines_CmGJ"><span class="token-line" style="color:#393A34"><span class="token plain">./setup.sh healthcheck golang</span><br></span></code></pre><div class="buttonGroup_yRlK"><button type="button" aria-label="Copy code to clipboard" title="Copy" class="clean-btn"><span class="copyButtonIcons_yBV4" aria-hidden="true"><svg viewBox="0 0 24 24" class="copyButtonIcon_Ctry"><path fill="currentColor" d="M19,21H8V7H19M19,5H8A2,2 0 0,0 6,7V21A2,2 0 0,0 8,23H19A2,2 0 0,0 21,21V7A2,2 0 0,0 19,5M16,1H4A2,2 0 0,0 2,3V17H4V3H16V1Z"></path></svg><svg viewBox="0 0 24 24" class="copyButtonSuccessIcon_FUe1"><path fill="currentColor" d="M21,7L9,19L3.5,13.5L4.91,12.09L9,16.17L19.59,5.59L21,7Z"></path></svg></span></button></div></div></div>
<h3 class="anchor anchorWithStickyNavbar_k394" id="exit-codes">Exit codes<a href="https://shisho.dev/docs/r/202606-takumi-guard-healthcheck#exit-codes" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>The healthcheck uses exit codes to signal the result, making it easy to integrate into management tool workflows and automation:</p>
<table><thead><tr><th>Exit code</th><th>Meaning</th></tr></thead><tbody><tr><td><code>0</code></td><td>All checks passed</td></tr><tr><td><code>1</code></td><td>One or more checks failed</td></tr><tr><td><code>2</code></td><td>Inconclusive (e.g. CLI not found, network issue)</td></tr></tbody></table>
<h3 class="anchor anchorWithStickyNavbar_k394" id="example-output">Example output<a href="https://shisho.dev/docs/r/202606-takumi-guard-healthcheck#example-output" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<div class="codeBlockContainer_tXdS theme-code-block" style="--prism-color:#393A34;--prism-background-color:#f6f8fa"><div class="codeBlockContent_zXtR"><pre tabindex="0" class="prism-code language-text codeBlock_qqWd thin-scrollbar" style="color:#393A34;background-color:#f6f8fa"><code class="codeBlockLines_CmGJ"><span class="token-line" style="color:#393A34"><span class="token plain">$ ./setup.sh healthcheck golang</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain" style="display:inline-block"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">[OK] go: GOPROXY → https://golang.flatt.tech</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">[OK] go: Guard proxy reachable</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">go: creating new go.mod: module healthcheck-tmp</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">[OK] go: sentinel module hola-takumi-go@v0.1.0 correctly blocked</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain" style="display:inline-block"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">[OK] All healthchecks passed</span><br></span></code></pre><div class="buttonGroup_yRlK"><button type="button" aria-label="Copy code to clipboard" title="Copy" class="clean-btn"><span class="copyButtonIcons_yBV4" aria-hidden="true"><svg viewBox="0 0 24 24" class="copyButtonIcon_Ctry"><path fill="currentColor" d="M19,21H8V7H19M19,5H8A2,2 0 0,0 6,7V21A2,2 0 0,0 8,23H19A2,2 0 0,0 21,21V7A2,2 0 0,0 19,5M16,1H4A2,2 0 0,0 2,3V17H4V3H16V1Z"></path></svg><svg viewBox="0 0 24 24" class="copyButtonSuccessIcon_FUe1"><path fill="currentColor" d="M21,7L9,19L3.5,13.5L4.91,12.09L9,16.17L19.59,5.59L21,7Z"></path></svg></span></button></div></div></div>
<h2 class="anchor anchorWithStickyNavbar_k394" id="ecosystems">Supported Ecosystems<a href="https://shisho.dev/docs/r/202606-takumi-guard-healthcheck#ecosystems" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>The healthcheck currently supports npm, RubyGems, and Go. PyPI support will be added in a future update once a test package is published.</p>
<table><thead><tr><th>Ecosystem</th><th>Scope argument</th><th>Test package</th></tr></thead><tbody><tr><td>npm</td><td><code>npm</code></td><td><code>@panda-guard/test-malicious</code></td></tr><tr><td>RubyGems</td><td><code>rubygems</code></td><td><code>hola-takumi</code> v0.1.0</td></tr><tr><td>Go</td><td><code>golang</code></td><td><code>github.com/flatt-security/hola-takumi-go</code> v0.1.0</td></tr><tr><td>PyPI</td><td><code>pypi</code></td><td><em>(coming soon)</em></td></tr></tbody></table>
<p>For full documentation on the healthcheck subcommand, see the <a href="https://shisho.dev/docs/t/guard/features/admin-deployment#healthcheck">Admin Deployment — Healthcheck</a> section of the user guide.</p>]]></content>
        <author>
            <name>Cheng-Jui Chen</name>
            <uri>https://github.com/isaswa</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi Guard: npm Lockfile Behavior Change for npm v11.15.0+ Compatibility]]></title>
        <id>https://shisho.dev/docs/r/202606-takumi-guard-npm-lockfile</id>
        <link href="https://shisho.dev/docs/r/202606-takumi-guard-npm-lockfile"/>
        <updated>2026-06-12T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[npm v11.15.0+ users will see Takumi Guard's registry URL in package-lock.json so that installs keep working with npm's new supply chain checks.]]></summary>
        <content type="html"><![CDATA[<p>Takumi Guard now rewrites tarball download URLs for npm v11.15.0 and later, keeping installs working with <strong>npm's new supply chain protections</strong>. Users on these npm versions will see Takumi Guard's registry URL in their <code>package-lock.json</code> files.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="background">Background<a href="https://shisho.dev/docs/r/202606-takumi-guard-npm-lockfile#background" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>npm v11.15.0 introduced enforcement of the <code>--allow-remote</code> supply chain control. With this check, a dependency whose tarball download URL points to a host different from the configured registry is classified as a "remote" dependency, and downloads of such transitive dependencies are rejected.</p>
<p>Previously, Takumi Guard served upstream <code>registry.npmjs.org</code> tarball URLs to npm clients verbatim. Under the new check, npm sees a mismatch between the configured registry (<code>npm.flatt.tech</code>) and the tarball host, so installs through Takumi Guard could fail with <code>EALLOWREMOTE</code> errors on npm v11.15.0 and later.</p>
<p>Takumi Guard now rewrites tarball URLs to its own host for npm v11.15.0+ clients, which restores the correct "registry" classification. Upcoming npm releases are set to tighten these checks further — for example, by also requiring tarball URLs to live under the configured registry's path — so this change is a necessary step to keep Takumi Guard compatible with current and future npm versions.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="what-changes">What Changes<a href="https://shisho.dev/docs/r/202606-takumi-guard-npm-lockfile#what-changes" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<h3 class="anchor anchorWithStickyNavbar_k394" id="npm-v11150-and-later">npm v11.15.0 and later<a href="https://shisho.dev/docs/r/202606-takumi-guard-npm-lockfile#npm-v11150-and-later" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>Lockfile (<code>package-lock.json</code>) entries that are added or updated will record Takumi Guard's registry URL (<code>https://npm.flatt.tech/...</code>) in their <code>resolved</code> fields instead of the upstream <code>registry.npmjs.org</code> URL. <strong>This is expected behavior</strong> and is necessary for installs to work under npm's supply chain checks.</p>
<p>Package integrity is unaffected — <code>integrity</code> hashes are unchanged, and <code>npm audit signatures</code> continues to verify registry signatures and attestations as before.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="npm-versions-before-v11150">npm versions before v11.15.0<a href="https://shisho.dev/docs/r/202606-takumi-guard-npm-lockfile#npm-versions-before-v11150" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>No change. Older npm clients continue to receive upstream tarball URLs, and their lockfiles are unaffected.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="pnpm-yarn-and-bun">pnpm, Yarn, and Bun<a href="https://shisho.dev/docs/r/202606-takumi-guard-npm-lockfile#pnpm-yarn-and-bun" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>No change in this release. pnpm does not record full tarball URLs in <code>pnpm-lock.yaml</code>, so its lockfile never contains registry hosts. Yarn v1 already records Takumi Guard's URL in <code>yarn.lock</code> as described in a <a href="https://shisho.dev/docs/r/202604-takumi-guard-yarn-v1-lockfile">previous release note</a>; Yarn v2–v4 (Berry) and Bun are unaffected.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="recommendation">Recommendation<a href="https://shisho.dev/docs/r/202606-takumi-guard-npm-lockfile#recommendation" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>If you prefer to keep registry URLs out of your lockfile entirely, consider migrating to <strong>pnpm</strong>. pnpm does not embed tarball URLs in its lockfile, works seamlessly with Takumi Guard, and offers strong supply chain security features out of the box.</p>]]></content>
        <author>
            <name>Deividas Turskis</name>
            <uri>https://github.com/ren-</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi Guard Packagist Support Released]]></title>
        <id>https://shisho.dev/docs/r/202606-takumi-guard-packagist</id>
        <link href="https://shisho.dev/docs/r/202606-takumi-guard-packagist"/>
        <updated>2026-06-12T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[Takumi Guard now protects PHP projects by blocking malicious Packagist packages.]]></summary>
        <content type="html"><![CDATA[<p>Takumi Guard now supports <strong>Packagist</strong> alongside npm, PyPI, RubyGems, and Go.</p>
<p>PHP projects using <strong>Composer</strong> can now route <code>composer install</code> and <code>composer update</code> through Takumi Guard to block known-malicious packages before they reach your CI or development environment.</p>
<p><img decoding="async" loading="lazy" alt="Takumi Guard now supports Packagist" src="https://shisho.dev/docs/assets/images/eyecatch-e03dacb4465d01e03e32d905310dd4e6.png" width="2400" height="1260" class="img_aV4l"></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="overview">Overview<a href="https://shisho.dev/docs/r/202606-takumi-guard-packagist#overview" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Takumi Guard is a security proxy that sits between your package manager and the upstream registry. It checks every install request against GMO Flatt Security's threat database and blocks known-malicious packages.</p>
<p>With this release, the same protection that npm, Python, Ruby, and Go users have is now available for the PHP ecosystem:</p>
<ul>
<li><strong><a href="https://shisho.dev/docs/t/guard/features/package-blocking">Package Blocking</a></strong>: Malicious packages are blocked before any code is fetched</li>
<li><strong><a href="https://shisho.dev/docs/t/guard/features/installation-logs">Download Tracking</a></strong>: Records install history for authenticated users</li>
<li><strong><a href="https://shisho.dev/docs/t/guard/features/breach-notifications">Breach Notifications</a></strong>: Get notified if a package you installed is later flagged as malicious</li>
</ul>
<p>The proxy speaks the standard <a href="https://getcomposer.org/doc/05-repositories.md#composer" target="_blank" rel="noopener noreferrer">Composer repository protocol</a>, the same mechanism used by Private Packagist and Toran Proxy — so no tooling changes are needed, just a one-time repository configuration.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="getting-started">Getting Started<a href="https://shisho.dev/docs/r/202606-takumi-guard-packagist#getting-started" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>The following works anonymously — no account or registration required. Add Takumi Guard as a Composer repository and disable the default Packagist.org so every package resolves through the proxy:</p>
<div class="language-bash codeBlockContainer_tXdS theme-code-block" style="--prism-color:#393A34;--prism-background-color:#f6f8fa"><div class="codeBlockContent_zXtR"><pre tabindex="0" class="prism-code language-bash codeBlock_qqWd thin-scrollbar" style="color:#393A34;background-color:#f6f8fa"><code class="codeBlockLines_CmGJ"><span class="token-line" style="color:#393A34"><span class="token function" style="color:#d73a49">composer</span><span class="token plain"> config </span><span class="token parameter variable" style="color:#36acaa">--global</span><span class="token plain"> repositories.takumi-guard </span><span class="token function" style="color:#d73a49">composer</span><span class="token plain"> https://packagist.flatt.tech</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain"></span><span class="token function" style="color:#d73a49">composer</span><span class="token plain"> config </span><span class="token parameter variable" style="color:#36acaa">--global</span><span class="token plain"> repositories.packagist.org </span><span class="token boolean" style="color:#36acaa">false</span><br></span></code></pre><div class="buttonGroup_yRlK"><button type="button" aria-label="Copy code to clipboard" title="Copy" class="clean-btn"><span class="copyButtonIcons_yBV4" aria-hidden="true"><svg viewBox="0 0 24 24" class="copyButtonIcon_Ctry"><path fill="currentColor" d="M19,21H8V7H19M19,5H8A2,2 0 0,0 6,7V21A2,2 0 0,0 8,23H19A2,2 0 0,0 21,21V7A2,2 0 0,0 19,5M16,1H4A2,2 0 0,0 2,3V17H4V3H16V1Z"></path></svg><svg viewBox="0 0 24 24" class="copyButtonSuccessIcon_FUe1"><path fill="currentColor" d="M21,7L9,19L3.5,13.5L4.91,12.09L9,16.17L19.59,5.59L21,7Z"></path></svg></span></button></div></div></div>
<p>That's the whole setup. Blocking applies to <code>composer install</code> and <code>composer update</code> — <strong>including installs from an existing <code>composer.lock</code></strong> (Composer 2.10+), so projects with a committed lock file are protected without any migration step.</p>
<div class="theme-admonition theme-admonition-info admonition_ODxW alert alert--info"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 14 16"><path fill-rule="evenodd" d="M7 2.3c3.14 0 5.7 2.56 5.7 5.7s-2.56 5.7-5.7 5.7A5.71 5.71 0 0 1 1.3 8c0-3.14 2.56-5.7 5.7-5.7zM7 1C3.14 1 0 4.14 0 8s3.14 7 7 7 7-3.14 7-7-3.14-7-7-7zm1 3H6v5h2V4zm0 6H6v2h2v-2z"></path></svg></span>Optional: download tracking</div><div class="admonitionContent_Kqb4"><p>To be notified about the exact versions you installed, run <code>composer update mirrors</code> once per project (identical to <code>composer update --lock</code> — it refreshes the lock file's download URLs without changing versions). This routes artifact downloads through the proxy and is <strong>not required for blocking</strong>.</p></div></div>
<h3 class="anchor anchorWithStickyNavbar_k394" id="github-actions">GitHub Actions<a href="https://shisho.dev/docs/r/202606-takumi-guard-packagist#github-actions" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>Use the <a href="https://github.com/flatt-security/setup-takumi-guard-packagist" target="_blank" rel="noopener noreferrer"><code>flatt-security/setup-takumi-guard-packagist</code></a> action. Blocking-only requires no account or token — it configures the repository, and your existing <code>composer install</code> is protected (committed lock files included):</p>
<div class="language-yaml codeBlockContainer_tXdS theme-code-block" style="--prism-color:#393A34;--prism-background-color:#f6f8fa"><div class="codeBlockContent_zXtR"><pre tabindex="0" class="prism-code language-yaml codeBlock_qqWd thin-scrollbar" style="color:#393A34;background-color:#f6f8fa"><code class="codeBlockLines_CmGJ"><span class="token-line" style="color:#393A34"><span class="token key atrule" style="color:#00a4db">jobs</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">  </span><span class="token key atrule" style="color:#00a4db">build</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">    </span><span class="token key atrule" style="color:#00a4db">runs-on</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> ubuntu</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">latest</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">    </span><span class="token key atrule" style="color:#00a4db">steps</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">      </span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain"> </span><span class="token key atrule" style="color:#00a4db">uses</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> actions/checkout@v4</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">      </span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain"> </span><span class="token key atrule" style="color:#00a4db">uses</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> shivammathur/setup</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">php@v2</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">        </span><span class="token key atrule" style="color:#00a4db">with</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">          </span><span class="token key atrule" style="color:#00a4db">php-version</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> </span><span class="token string" style="color:#e3116c">"8.3"</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">          </span><span class="token key atrule" style="color:#00a4db">tools</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> composer</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain">v2</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">      </span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain"> </span><span class="token key atrule" style="color:#00a4db">uses</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> flatt</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">security/setup</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">takumi</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">guard</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">packagist@v1</span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">      </span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain"> </span><span class="token key atrule" style="color:#00a4db">run</span><span class="token punctuation" style="color:#393A34">:</span><span class="token plain"> composer install </span><span class="token punctuation" style="color:#393A34">-</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">no</span><span class="token punctuation" style="color:#393A34">-</span><span class="token plain">interaction</span><br></span></code></pre><div class="buttonGroup_yRlK"><button type="button" aria-label="Copy code to clipboard" title="Copy" class="clean-btn"><span class="copyButtonIcons_yBV4" aria-hidden="true"><svg viewBox="0 0 24 24" class="copyButtonIcon_Ctry"><path fill="currentColor" d="M19,21H8V7H19M19,5H8A2,2 0 0,0 6,7V21A2,2 0 0,0 8,23H19A2,2 0 0,0 21,21V7A2,2 0 0,0 19,5M16,1H4A2,2 0 0,0 2,3V17H4V3H16V1Z"></path></svg><svg viewBox="0 0 24 24" class="copyButtonSuccessIcon_FUe1"><path fill="currentColor" d="M21,7L9,19L3.5,13.5L4.91,12.09L9,16.17L19.59,5.59L21,7Z"></path></svg></span></button></div></div></div>
<p>For organization-level download tracking and <a href="https://shisho.dev/docs/t/guard/features/breach-notifications">breach notifications</a>, add a <code>bot-id</code> and grant <code>id-token: write</code> — the action does the OIDC → short-lived-token exchange automatically, no long-lived secret in CI. See <a href="https://shisho.dev/docs/t/guard/quickstart/packagist#setup-ci">the Packagist quickstart</a> for the full pattern.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="verify">Verify Your Setup<a href="https://shisho.dev/docs/r/202606-takumi-guard-packagist#verify" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Confirm blocking is active by trying to require our published test package, <code>flatt-security/hola-takumi-php</code> — a harmless package that is permanently on the blocklist:</p>
<div class="language-bash codeBlockContainer_tXdS theme-code-block" style="--prism-color:#393A34;--prism-background-color:#f6f8fa"><div class="codeBlockContent_zXtR"><pre tabindex="0" class="prism-code language-bash codeBlock_qqWd thin-scrollbar" style="color:#393A34;background-color:#f6f8fa"><code class="codeBlockLines_CmGJ"><span class="token-line" style="color:#393A34"><span class="token function" style="color:#d73a49">composer</span><span class="token plain"> require --dry-run flatt-security/hola-takumi-php</span><br></span></code></pre><div class="buttonGroup_yRlK"><button type="button" aria-label="Copy code to clipboard" title="Copy" class="clean-btn"><span class="copyButtonIcons_yBV4" aria-hidden="true"><svg viewBox="0 0 24 24" class="copyButtonIcon_Ctry"><path fill="currentColor" d="M19,21H8V7H19M19,5H8A2,2 0 0,0 6,7V21A2,2 0 0,0 8,23H19A2,2 0 0,0 21,21V7A2,2 0 0,0 19,5M16,1H4A2,2 0 0,0 2,3V17H4V3H16V1Z"></path></svg><svg viewBox="0 0 24 24" class="copyButtonSuccessIcon_FUe1"><path fill="currentColor" d="M21,7L9,19L3.5,13.5L4.91,12.09L9,16.17L19.59,5.59L21,7Z"></path></svg></span></button></div></div></div>
<p>This must <strong>fail</strong> with a flagged-package error. If it resolves successfully, requests are not going through Takumi Guard — re-check <code>composer config --global --list | grep -E 'repositories|packagist'</code>. A package on the blocklist is rejected during <code>composer install</code>, <code>composer update</code>, and <code>composer require</code>. For details, see <a href="https://shisho.dev/docs/t/guard/quickstart/packagist#verify-setup">"Verify Your Setup" in the Packagist quickstart</a>.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="email-registration">Email Registration Unlocks More (Free)<a href="https://shisho.dev/docs/r/202606-takumi-guard-packagist#email-registration" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Register your email to receive notifications if a package you installed is later found to be malicious. Free of charge.</p>
<div class="theme-admonition theme-admonition-info admonition_ODxW alert alert--info"><div class="admonitionHeading_X5mK"><span class="admonitionIcon_kMTu"><svg viewBox="0 0 14 16"><path fill-rule="evenodd" d="M7 2.3c3.14 0 5.7 2.56 5.7 5.7s-2.56 5.7-5.7 5.7A5.71 5.71 0 0 1 1.3 8c0-3.14 2.56-5.7 5.7-5.7zM7 1C3.14 1 0 4.14 0 8s3.14 7 7 7 7-3.14 7-7-3.14-7-7-7zm1 3H6v5h2V4zm0 6H6v2h2v-2z"></path></svg></span>info</div><div class="admonitionContent_Kqb4"><p>If you already have an org user token or email-verified token from using Takumi Guard with npm, PyPI, RubyGems, or Go, you don't need to register again — the same token works for Composer.</p></div></div>
<p><strong>Step 1:</strong> Register your email</p>
<div class="language-bash codeBlockContainer_tXdS theme-code-block" style="--prism-color:#393A34;--prism-background-color:#f6f8fa"><div class="codeBlockContent_zXtR"><pre tabindex="0" class="prism-code language-bash codeBlock_qqWd thin-scrollbar" style="color:#393A34;background-color:#f6f8fa"><code class="codeBlockLines_CmGJ"><span class="token-line" style="color:#393A34"><span class="token function" style="color:#d73a49">curl</span><span class="token plain"> </span><span class="token parameter variable" style="color:#36acaa">-X</span><span class="token plain"> POST https://packagist.flatt.tech/api/v1/tokens </span><span class="token punctuation" style="color:#393A34">\</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">  </span><span class="token parameter variable" style="color:#36acaa">-H</span><span class="token plain"> </span><span class="token string" style="color:#e3116c">"Content-Type: application/json"</span><span class="token plain"> </span><span class="token punctuation" style="color:#393A34">\</span><span class="token plain"></span><br></span><span class="token-line" style="color:#393A34"><span class="token plain">  </span><span class="token parameter variable" style="color:#36acaa">-d</span><span class="token plain"> </span><span class="token string" style="color:#e3116c">'{"email": "you@example.com"}'</span><br></span></code></pre><div class="buttonGroup_yRlK"><button type="button" aria-label="Copy code to clipboard" title="Copy" class="clean-btn"><span class="copyButtonIcons_yBV4" aria-hidden="true"><svg viewBox="0 0 24 24" class="copyButtonIcon_Ctry"><path fill="currentColor" d="M19,21H8V7H19M19,5H8A2,2 0 0,0 6,7V21A2,2 0 0,0 8,23H19A2,2 0 0,0 21,21V7A2,2 0 0,0 19,5M16,1H4A2,2 0 0,0 2,3V17H4V3H16V1Z"></path></svg><svg viewBox="0 0 24 24" class="copyButtonSuccessIcon_FUe1"><path fill="currentColor" d="M21,7L9,19L3.5,13.5L4.91,12.09L9,16.17L19.59,5.59L21,7Z"></path></svg></span></button></div></div></div>
<p><strong>Step 2:</strong> Get your API key from the welcome email. The key is included directly in the email body — no link to click.</p>
<p><strong>Step 3:</strong> Store the token so Composer authenticates with it on every fetch</p>
<div class="language-bash codeBlockContainer_tXdS theme-code-block" style="--prism-color:#393A34;--prism-background-color:#f6f8fa"><div class="codeBlockContent_zXtR"><pre tabindex="0" class="prism-code language-bash codeBlock_qqWd thin-scrollbar" style="color:#393A34;background-color:#f6f8fa"><code class="codeBlockLines_CmGJ"><span class="token-line" style="color:#393A34"><span class="token function" style="color:#d73a49">composer</span><span class="token plain"> config </span><span class="token parameter variable" style="color:#36acaa">--global</span><span class="token plain"> </span><span class="token parameter variable" style="color:#36acaa">--auth</span><span class="token plain"> http-basic.packagist.flatt.tech token tg_anon_xxxxxx</span><br></span></code></pre><div class="buttonGroup_yRlK"><button type="button" aria-label="Copy code to clipboard" title="Copy" class="clean-btn"><span class="copyButtonIcons_yBV4" aria-hidden="true"><svg viewBox="0 0 24 24" class="copyButtonIcon_Ctry"><path fill="currentColor" d="M19,21H8V7H19M19,5H8A2,2 0 0,0 6,7V21A2,2 0 0,0 8,23H19A2,2 0 0,0 21,21V7A2,2 0 0,0 19,5M16,1H4A2,2 0 0,0 2,3V17H4V3H16V1Z"></path></svg><svg viewBox="0 0 24 24" class="copyButtonSuccessIcon_FUe1"><path fill="currentColor" d="M21,7L9,19L3.5,13.5L4.91,12.09L9,16.17L19.59,5.59L21,7Z"></path></svg></span></button></div></div></div>
<p>Composer uses HTTP Basic auth keyed by host name — the username is ignored, and the token goes in the password field. Your installs are now tracked, and you will be notified if a downloaded package is later flagged.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="private-packages">Private Packages<a href="https://shisho.dev/docs/r/202606-takumi-guard-packagist#private-packages" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Public packages go through Takumi Guard; private packages (e.g. a private GitHub repository) should bypass the proxy. Declare them as their own <code>vcs</code> or <code>path</code> repositories alongside the Guard repository, and Composer fetches each package from the repository that provides it. See the <a href="https://shisho.dev/docs/t/guard/quickstart/packagist#private-packages">Packagist quickstart</a> for details.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="organization-setup">Organization-Wide Management, Too<a href="https://shisho.dev/docs/r/202606-takumi-guard-packagist#organization-setup" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Running Takumi Guard across your team? <a href="https://shisho.dev/docs/t/guard/features/installation-logs">Installation log search</a>, <a href="https://shisho.dev/docs/t/guard/features/token-management">centralized org user token management</a>, and <a href="https://shisho.dev/docs/t/guard/features/breach-notifications">breach-notification webhooks</a> are all available for organization-wide operations. Get started with a Takumi subscription (Guard enabled):</p>
<ol>
<li>Go to <a href="https://cloud.shisho.dev/hello/takumi" target="_blank" rel="noopener noreferrer">https://cloud.shisho.dev/hello/takumi</a> and sign in</li>
<li>Register your organization and subscribe to Takumi</li>
<li>Navigate to <strong>Guard</strong> &gt; <strong>Settings</strong> from the sidebar</li>
<li>Click "Enable" to activate Guard</li>
</ol>
<p><img decoding="async" loading="lazy" alt="Guard settings page" src="https://shisho.dev/docs/assets/images/ui-guard-settings-6b26b5c78a1bd5b0b3ed5c3e029208e6.png" width="1001" height="373" class="img_aV4l"></p>
<p>Once Guard is enabled, configure your CI or developer machines using the <a href="https://shisho.dev/docs/t/guard/quickstart/packagist">Packagist quickstart</a>.</p>
<p>If you only need a <a href="https://shisho.dev/docs/t/guard/quickstart/packagist#setup-org-user-token">long-lived org token</a> from GitHub Actions, <strong>no payment is required</strong>. A payment screen appears during organization registration, but you can skip it — simply register your GitHub organization from the Guard page to receive an org token.</p>]]></content>
        <author>
            <name>Deividas Turskis</name>
            <uri>https://github.com/ren-</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
    <entry>
        <title type="html"><![CDATA[Takumi byGMO's Policy on the Mythos-Class Model Claude Fable 5]]></title>
        <id>https://shisho.dev/docs/r/202606-takumi-fable-policy</id>
        <link href="https://shisho.dev/docs/r/202606-takumi-fable-policy"/>
        <updated>2026-06-10T00:00:00.000Z</updated>
        <summary type="html"><![CDATA[Our policy at Takumi byGMO regarding the new Mythos-class model Claude Fable 5.]]></summary>
        <content type="html"><![CDATA[<p>Anthropic's new Mythos-class model, Claude Fable 5, was released today, June 10, 2026. Here we share how Takumi byGMO, our AI agent for security assessment and penetration testing, will support this model.</p>
<p><img decoding="async" loading="lazy" alt="Takumi byGMO&amp;#39;s policy on the Mythos-class model Claude Fable 5" src="https://shisho.dev/docs/assets/images/eyecatch-dd8bbd9a1e73bdb4dd52705fdc54c534.png" width="1200" height="630" class="img_aV4l"></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="overview-of-claude-fable-5-and-our-existing-plans">Overview of Claude Fable 5 and Our Existing Plans<a href="https://shisho.dev/docs/r/202606-takumi-fable-policy#overview-of-claude-fable-5-and-our-existing-plans" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>Claude Fable 5 is Anthropic's latest AI model, released on June 10, 2026. It is rooted in the same underlying model weights as "Claude Mythos 5", the model widely noted for its strong cybersecurity capabilities. On top of that, it has stronger safeguards against misuse than Mythos 5.</p>
<blockquote>
<p>From <a href="https://www-cdn.anthropic.com/d00db56fa754a1b115b6dd7cb2e3c342ee809620.pdf" target="_blank" rel="noopener noreferrer">"System Card: Claude Fable 5 &amp; Claude Mythos 5"</a>:</p>
<p>Fable 5 is being released for general access—it has the same underlying model weights as Mythos 5, but has additional safeguards to prevent misuse for cybersecurity and biology.</p>
</blockquote>
<p>The Claude Fable 5 and Claude Mythos 5 models have drawn particular expectation and interest for use in cybersecurity.</p>
<p>As a notable result related to these models, "Claude Mythos Preview", the predecessor of Claude Mythos 5, has already contributed to the discovery of 23,000 vulnerabilities (see <a href="https://www.anthropic.com/research/glasswing-initial-update" target="_blank" rel="noopener noreferrer">"Project Glasswing: An initial update"</a>), to the point where government agencies including Japan's Financial Services Agency and Ministry of Health, Labour and Welfare have issued advisories to critical institutions (see <a href="https://www.fsa.go.jp/news/r7/sonota/20260522-5/20260522.html" target="_blank" rel="noopener noreferrer">the FSA advisory</a>).</p>
<p>In light of this, Takumi byGMO had reported the following plan for the period after the general release of Mythos-class models, with the aim of supporting security engineers who protect Japanese businesses in their use of these models (<a href="https://prtimes.jp/main/html/rd/p/000000072.000027502.html" target="_blank" rel="noopener noreferrer">original</a>).</p>
<blockquote>
<p><strong>Deployment plan following the general release of "Mythos-class models"</strong></p>
<ul>
<li>AI penetration testing (a new feature in which an AI agent attempts to break into a system until it reaches a goal): deployed and available within at most 5 business days after the model's general release</li>
<li>AI security assessment and automated fixing (an AI agent automatically discovers and fixes vulnerabilities): we maintain delivery on current-tier models, while adding a mode that lets you specify the use of Mythos-class models (and comparable high-end models), particularly for inspecting and fixing business logic</li>
<li>"Takumi Guard" and "Takumi Runner" (features that protect the software supply chain): deployed first into our underlying Threat Intelligence platform and used for malware discovery and analysis, resulting in faster and more accurate detection of malicious OSS packages than before</li>
</ul>
<p>Note: For tasks where our own benchmarks show that a "Mythos-class model" is not necessarily required, we use existing models. This achieves maximum inspection performance at minimum cost.</p>
</blockquote>
<h2 class="anchor anchorWithStickyNavbar_k394" id="our-policy-on-claude-fable-5">Our Policy on Claude Fable 5<a href="https://shisho.dev/docs/r/202606-takumi-fable-policy#our-policy-on-claude-fable-5" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>After evaluation by our specialist team, <strong>we have decided to hold off on deploying Claude Fable 5 for the AI penetration testing feature (the new feature to be released) as we judged it unnecessary for this release, and to instead begin operating it on Opus 4.8 and models of an equivalent tier, which already record sufficient performance</strong>. Our approach to other features is the same: in principle, we continue to operate on models other than Fable 5 that deliver sufficient performance.</p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="background-to-this-policy">Background to This Policy<a href="https://shisho.dev/docs/r/202606-takumi-fable-policy#background-to-this-policy" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>The background to this policy is as follows.</p>
<ul>
<li><strong>The model's safeguards can be triggered excessively.</strong> As a result, even security reviews and penetration tests that we judge not to violate the model provider's terms, our own terms, or applicable laws may fail to deliver stable performance.</li>
<li><strong>Existing models (Claude Opus 4.8, and other models from Google and OpenAI) already show certain results with our harness.</strong> While we expect further performance gains from high-end models in the future, multi-stage attacks are realistically achievable in scenarios that do not require special 0-day (or complex 1-day) vulnerabilities.</li>
</ul>
<h3 class="anchor anchorWithStickyNavbar_k394" id="our-view-on-the-performance-of-existing-models">Our View on the Performance of Existing Models<a href="https://shisho.dev/docs/r/202606-takumi-fable-policy#our-view-on-the-performance-of-existing-models" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>The latter point in particular, that models up to and including Opus 4.8 have already reached a certain level, deserves attention.</p>
<p>The <a href="https://www-cdn.anthropic.com/d00db56fa754a1b115b6dd7cb2e3c342ee809620.pdf" target="_blank" rel="noopener noreferrer">System Card for Claude Mythos 5 and Fable 5</a> and similar materials describe performance gains on benchmarks such as ExploitBench, OSS-Fuzz, and CyberGym. These generally have the exploitation of browsers and binaries in mind, and their evaluation of the ability to compromise web systems and cloud is limited.</p>
<p>The set of capabilities improved in Claude Mythos 5 can be imagined to be very important for <strong>organizations that face threats which exploit 0-day or highly complex N-day vulnerabilities</strong>.</p>
<p><strong>On the other hand, the organizations that should assume threats of this intensity are limited.</strong> Typical system compromises start with people as the entry point, or with more basic mistakes (for example, unintentionally exposed admin consoles, weak passwords, well-known arbitrary code execution vectors such as React2Shell, unmaintained VPN appliances, unintentionally left secrets, and so on). The attack process after an attacker has completed initial intrusion also does not necessarily require complex 0-day or N-day vulnerabilities.</p>
<p>Assuming this minimal set of threats that most of our customers should be aware of, we believe that <strong>models prior to Claude Fable 5, such as Opus 4.8, are capable of sufficient simulated attacks</strong>. For example, our benchmark set includes scenarios that steal data on the cloud through multi-stage attacks with the simple configuration shown below. This is well within reach of pre-Opus 4.8 models combined with our harness.</p>
<p><img decoding="async" loading="lazy" alt="Scenario demo of the AI penetration testing feature" src="https://shisho.dev/docs/assets/images/pentesting-demo-e26eb4bd3953814de2d9f3a3f602ba63.png" width="1394" height="879" class="img_aV4l"></p>
<h3 class="anchor anchorWithStickyNavbar_k394" id="our-commitment-to-safety">Our Commitment to Safety<a href="https://shisho.dev/docs/r/202606-takumi-fable-policy#our-commitment-to-safety" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h3>
<p>If the model's safeguards are relaxed in the future, and once we have confirmed that we have safe safeguards and a harness appropriate to the model's performance, we will reconsider deploying Claude Fable 5.</p>
<p>In the use of AI for cybersecurity, the fact that benign and malicious use are two sides of the same coin is an unavoidable and important problem. Takumi byGMO and its provider, GMO Flatt Security, have kept this in mind and have applied basic controls such as <a href="https://shisho.dev/docs/t/assessment/features/assessment-authentication">organization authentication and ownership verification</a>. We will continue to coordinate with model providers and with international efforts on AI safety, and we remain committed to the safe delivery of AI technology.</p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="availability-of-the-ai-penetration-testing-feature">Availability of the AI Penetration Testing Feature<a href="https://shisho.dev/docs/r/202606-takumi-fable-policy#availability-of-the-ai-penetration-testing-feature" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>The AI penetration testing feature, which we had said would be deployed and available within at most 5 business days after the general release of Mythos-class models, will be rolled out to customers in stages from Monday, June 15, after internal re-adjustment. To ensure stable delivery, the feature will be made available gradually.</p>
<p>Unlike the existing assessment features, the AI penetration testing feature has the AI attempt highly flexible attacks until it reaches a given goal (for example, stealing information within a specific cloud resource in scope). It is effective when you have already identified important information and components that would be damaging if compromised, through cloud asset inventory, threat modeling, and the like.</p>
<p><img decoding="async" loading="lazy" alt="AI penetration testing feature" src="https://shisho.dev/docs/assets/images/pentesting-f33fc71bcd03c0f123b3218fe1e24c13.jpeg" width="1950" height="1341" class="img_aV4l"></p>
<h2 class="anchor anchorWithStickyNavbar_k394" id="contact">Contact<a href="https://shisho.dev/docs/r/202606-takumi-fable-policy#contact" class="hash-link" aria-label="Direct link to heading" title="Direct link to heading">​</a></h2>
<p>As we roll out the AI penetration testing feature from June 15 onward, customers who would like priority access, or who are interested in the details of the feature, can contact their sales representative or reach out through <a href="https://flatt.tech/takumi" target="_blank" rel="noopener noreferrer">our website</a>.</p>]]></content>
        <author>
            <name>Takashi Yoneuchi</name>
            <uri>https://github.com/lmt-swallow</uri>
        </author>
        <category label="release-note" term="release-note"/>
    </entry>
</feed>